Manufacturing Ransomware Recovery Example
  • Sep, Wed, 2026

Manufacturing Ransomware Recovery Example

A production line stopped at 6:12 a.m. is not an IT inconvenience. It is missed shipments, idle labor, delayed raw-material deliveries, and customers asking whether their orders will move this week. This manufacturing ransomware recovery example shows what a disciplined response can look like when an attack reaches systems that support the shop floor.

The scenario is a composite based on common manufacturing risks, not a single company. The details matter because ransomware recovery is not simply restoring files. A manufacturer must make safe decisions about identity systems, production scheduling, ERP data, quality records, plant connectivity, and the evidence needed for insurance, legal, and regulatory obligations.

The manufacturing ransomware recovery example

A mid-sized components manufacturer operates one primary facility and a small distribution warehouse. Its 180 employees rely on Microsoft 365 for communications, an ERP platform for orders and inventory, a file server for engineering drawings, and network-connected workstations used for production scheduling and quality documentation. Some production equipment is isolated from the corporate network, but the scheduling terminals are not.

On a Monday morning, employees report that shared files will not open. Within minutes, the IT team finds ransomware notes on file shares and encrypted virtual machines. The attackers have also disabled several endpoint tools and used a compromised administrator account to move through the environment.

The immediate temptation is to bring systems back online as quickly as possible. That is how organizations reinfect restored systems or lose forensic evidence. The recovery team instead treats the first hours as a business continuity event with a security investigation running alongside it.

First priority: contain the spread without stopping safe production

The company disconnects affected servers and workstations from the network, disables the compromised accounts, and blocks remote access paths until they can be reviewed. The team preserves logs, ransom notes, and system images before making major changes. Its cyber insurance carrier and legal counsel are notified early, which helps coordinate breach-response obligations and communications.

Plant leadership is brought into the response immediately. Rather than shutting down every machine, operations identifies what can continue safely using local controls, printed work orders, and manual inventory checks. The company pauses new automated scheduling changes, but keeps several production cells running where equipment is segmented and operators can verify specifications without relying on compromised systems.

This distinction is critical. The goal is not to keep every process moving at any cost. It is to maintain safe, controlled production while preventing the attacker from reaching additional systems or corrupting business records.

Recovery begins with clean systems, not encrypted files

The incident response team determines that the ransomware entered through a phishing email and then exploited an account without multifactor authentication. The attacker had access long enough to identify backup systems and attempt to delete recovery points. Fortunately, the manufacturer had separate, immutable backups that could not be altered through the compromised administrator account.

Before restoring data, the team rebuilds core identity services from known-good configurations. Administrator passwords are reset, multifactor authentication is enforced, stale accounts are removed, and endpoint security tools are reinstalled. This takes time, but restoring servers before securing identity would hand the attacker a second opportunity.

The company restores in a deliberate order. Communications and identity come first, allowing leaders and employees to coordinate through approved channels. Next comes the ERP environment, because it drives orders, purchasing, inventory, and shipping. Engineering drawings and quality documentation follow, then less time-sensitive departmental file shares.

Not every workload requires the same recovery target. A production schedule may need restoration within hours, while archived HR documents can wait. Defining these priorities before an incident prevents a technical team from spending valuable time on the wrong systems.

Validate data before returning it to operations

A restored ERP database is not automatically trustworthy. The manufacturer compares restored order data to recent exports, warehouse records, and paper documentation created during the outage. Quality leaders confirm that current revision-controlled drawings are available before production resumes at full capacity. Finance reconciles invoices and purchase orders that may have been entered or changed near the time of the attack.

This validation step creates a trade-off. It delays full normalization, but it avoids a more expensive problem: producing the wrong part, shipping against inaccurate inventory, or losing traceability for regulated customers. For manufacturers serving aerospace, healthcare, defense, or automotive supply chains, incomplete records can create compliance and contractual exposure long after the encryption is removed.

Why this recovery worked better than most

The company did not avoid disruption. It lost access to key systems for nearly two days and ran reduced operations while the recovery team worked. What limited the damage was preparation built around business dependencies rather than a generic backup checklist.

Several controls made the difference. Backups were protected from routine administrative access and tested regularly. Network segmentation reduced the attacker’s ability to move directly from office systems into every production asset. Leadership had documented recovery priorities and knew who could authorize downtime decisions. The company also had a managed security team monitoring alerts around the clock, which accelerated detection and helped preserve evidence.

Most significantly, the organization had practiced the question that matters during a ransomware event: what must be restored first for the business to operate safely? The answer was not “all servers.” It was a sequence of capabilities: secure communication, verified identity, order visibility, production scheduling, quality control, and shipping.

That sequence may differ by facility. A make-to-order manufacturer may place engineering files ahead of warehouse systems. A high-volume operation may prioritize manufacturing execution software and plant-floor connectivity. The right plan reflects how revenue, safety, and customer commitments actually move through the organization.

Where manufacturing recovery plans commonly fail

Many manufacturers maintain backups but cannot state whether those backups are isolated, immutable, complete, or fast enough to meet production requirements. A backup that takes five days to restore may protect data, yet still fail the business when customers expect shipments in 48 hours.

Another common failure is treating operational technology and IT as separate conversations. Production equipment may be segmented, but the systems used to schedule work, store specifications, manage quality records, or remotely support machinery often connect the two environments. Recovery planning must account for those dependencies without allowing a rushed IT restoration to create a plant-floor safety issue.

Communication also breaks down when responsibility is unclear. Executives need concise updates on downtime, financial exposure, and decision points. Operations needs practical direction about what can run manually. Employees need a trusted communication channel so they do not use personal email, unapproved file-sharing tools, or suspicious instructions from an attacker impersonating leadership.

Turn the example into a recovery plan

A practical ransomware recovery plan starts with a short, accurate inventory of systems that affect production, shipping, finance, engineering, and compliance. For each system, document its business owner, dependencies, acceptable downtime, recovery source, and validation process. Include cloud services, third-party vendors, remote access tools, and shared accounts, not just servers in the rack.

Then test the plan under realistic conditions. Restore a critical application into an isolated environment. Confirm that users can authenticate, that the recovered data is usable, and that the process can be completed within the promised recovery window. Tabletop exercises should include operations, finance, HR, legal, and leadership, because ransomware decisions are rarely made by IT alone.

Security controls should support recovery, not compete with it. Multifactor authentication, least-privilege access, endpoint detection and response, monitored backups, network segmentation, and 24/7 alerting all reduce the chance that a single compromised account becomes a plant-wide outage. For smaller manufacturers without a large internal security team, a managed IT and security partner can provide the monitoring, documentation, and response coordination that recovery requires.

The best time to measure whether your organization can recover is during a controlled test, when a delayed shipment is hypothetical. A clear recovery plan gives leadership room to make deliberate decisions when the factory floor is anything but calm.
Microsoft 365 Migration Example for SMBs
  • Sep, Tue, 2026

Microsoft 365 Migration Example for SMBs

A Microsoft 365 migration example is most useful when it reflects the reality of a growing business: email cannot stop, client records cannot disappear, and employees still need to work while the change is underway. A well-run migration is not simply a mailbox transfer. It is a controlled business continuity project that improves security, collaboration, and accountability without creating avoidable disruption.

Consider a 75-person professional services firm with offices in Dallas and North Texas. The firm relies on a mix of aging email hosting, shared network drives, personal cloud storage accounts, and a basic remote-access setup. It handles confidential client documents, must retain certain records, and has employees working from offices, homes, and client locations. Leadership wants a standard platform that can support growth without adding administrative burden to its operations team.

Microsoft 365 is the right destination, but the outcome depends on how the firm plans, secures, and governs the move.

Microsoft 365 Migration Example: The Starting Point

Before migration, the firm’s email was hosted through a legacy provider. Most staff accessed mail through Outlook, but mobile configurations varied widely. Some employees forwarded business email to personal accounts for convenience. File storage was even less consistent: active projects lived on a shared server, completed work sat in archived folders, and several teams used unsanctioned file-sharing tools to exchange large documents.

This arrangement created more than an inconvenience. It made access difficult to manage, complicated offboarding, and left leadership with limited visibility into where sensitive information resided. A ransomware event, a lost phone, or a departing employee could expose weaknesses that had accumulated over years.

The goal was not to move every file and setting exactly as it existed. That approach only carries old problems into a new platform. The goal was to establish a secure, usable operating model built around Exchange Online, Teams, SharePoint, OneDrive, and identity controls.

Phase One: Assess What Should Move

The first step was discovery. The IT team identified 82 mailboxes, including active users, shared addresses, conference rooms, and former employee accounts. It also reviewed aliases, distribution lists, external forwarding rules, mobile devices, line-of-business applications that send email, and DNS records.

For files, the firm reviewed approximately 3 TB of data. Not all of it belonged in Microsoft 365. Old software installers, redundant archives, and duplicate departmental folders were excluded or moved to lower-cost archival storage. Active client work, current templates, internal policies, and department-owned documents were categorized for SharePoint or Teams. Individual working files moved to OneDrive.

This classification work takes time, but it reduces risk. A migration team needs answers to practical questions before data starts moving: Who owns this folder? Who should retain access? Does it contain regulated or confidential information? Is there a retention requirement? Can the business safely dispose of it?

For a healthcare, legal, financial, or engineering firm, these questions are also compliance questions. Microsoft 365 can support stronger controls, but no platform automatically fixes weak data ownership or poor retention practices.

Phase Two: Build Security Before the Cutover

The firm did not wait until after the migration to address security. Before the first mailbox moved, the project team established a baseline configuration designed to protect accounts from common threats.

Multifactor authentication was required for all users, with stronger sign-in requirements for administrators. Legacy authentication protocols were reviewed and disabled where they were no longer necessary. Conditional access policies were configured to restrict risky sign-ins and require compliant devices for sensitive access. Administrative roles were limited according to job responsibility rather than assigned broadly for convenience.

Email security was also strengthened. Anti-phishing, anti-malware, and spam policies were tuned to the firm’s risk profile. External sender labeling and mailbox auditing helped users and administrators distinguish legitimate communication from impersonation attempts. Domain protection settings were prepared to reduce the risk of email spoofing.

These controls are often treated as technical details. They are business safeguards. Email remains one of the most common entry points for account compromise, wire fraud, and ransomware. Moving to Microsoft 365 without configuring identity and email security can simply place valuable data in a better-known target.

Phase Three: Pilot With the People Who Will Notice Problems

The firm selected 12 pilot users from operations, finance, leadership, and client service. The group included both technically confident employees and people who preferred established processes. That mix was intentional. A pilot that includes only power users may miss the usability issues that create help desk volume later.

Pilot mailboxes were migrated first, followed by a limited set of shared files and Teams channels. The team tested calendar sharing, mobile access, large attachments, external collaboration, multifunction printer scanning, and email delivery from the firm’s practice management system.

One issue surfaced quickly: several automated systems still relied on outdated SMTP settings. Another was more operational. Client-service staff needed a clearer process for sharing documents externally without creating anonymous public links. Both issues were corrected before the organization-wide cutover.

The pilot also shaped training. Employees did not need a long technical presentation about every Microsoft 365 feature. They needed to know where their files would live, how to access them from approved devices, how to identify suspicious messages, and whom to contact when something did not work.

Phase Four: Move Email and Files in Controlled Waves

The final migration took place in stages. Mailboxes were pre-synchronized in advance so that only recent changes needed to transfer during each cutover window. Users were scheduled in groups based on department needs and time sensitivity. Finance and executive mailboxes received additional planning because even short disruptions could affect approvals and client commitments.

The migration team communicated clearly before each wave. Staff received their scheduled cutover date, sign-in instructions, MFA enrollment guidance, mobile-device steps, and a direct support path. Managers were briefed on what to expect so they could plan around high-priority meetings or deadlines.

File migration required a different pace. The firm moved department libraries into SharePoint and Teams with permissions based on business roles. Instead of replicating every legacy folder permission, the team simplified access where possible. Excessively complex permissions can be hard to audit and even harder to support.

Personal working files moved to OneDrive, with training on when to use OneDrive versus a shared Teams or SharePoint location. That distinction matters. OneDrive is appropriate for an individual’s draft work and controlled sharing. Team-owned records, client deliverables, and operational documents should live where the appropriate group retains access when an employee changes roles or leaves.

What Changed After the Migration

Within weeks, the firm had a more consistent work environment. Employees used a single business identity for email, files, meetings, and approved collaboration. Mobile access was easier to manage. New hires could be provisioned with defined groups and standardized applications rather than inheriting access through informal requests.

Security improved because the firm had fewer unmanaged accounts, stronger authentication, better logging, and clearer control over external sharing. The organization also gained a foundation for retention policies, device management, backup planning, and incident response.

There were trade-offs. Some long-tenured employees needed extra support as familiar shared-drive workflows changed. SharePoint structure required governance, or it could become another place for documents to sprawl. Licensing needed periodic review as roles and security requirements evolved. Microsoft 365 reduces infrastructure overhead, but it does not remove the need for ongoing administration.

The Difference Between a Move and a Managed Environment

A successful migration is measured by more than whether mail arrives on Monday morning. The stronger test is whether the business is easier to protect, support, audit, and scale afterward.

For many small and mid-sized businesses, that requires a partner who can manage the technical project alongside the operational details: security policies, user communications, data decisions, cutover support, documentation, and post-migration governance. Sigma Networks approaches Microsoft 365 work as part of a broader security-first IT strategy, not as a one-time data transfer.

The right migration creates breathing room for the business. When identity, email, collaboration, and data protection are organized with intent, leaders can spend less time worrying about where information lives and more time directing where the company goes next.

Cloud Firewall vs Traditional Firewall Explained
  • Sep, Mon, 2026

Cloud Firewall vs Traditional Firewall Explained

A firewall used to be a physical appliance in a server closet, protecting a clearly defined office network. That model still has a place. But when employees work remotely, applications run in Microsoft 365 and cloud platforms, and data moves beyond one building, the cloud firewall vs traditional firewall decision becomes a business continuity and risk-management question.

For small and mid-sized businesses, the right answer is rarely about choosing the newest technology. It is about protecting the people, data, applications, and locations that keep the business running without adding unnecessary complexity or blind spots.

Cloud Firewall vs Traditional Firewall: The Core Difference

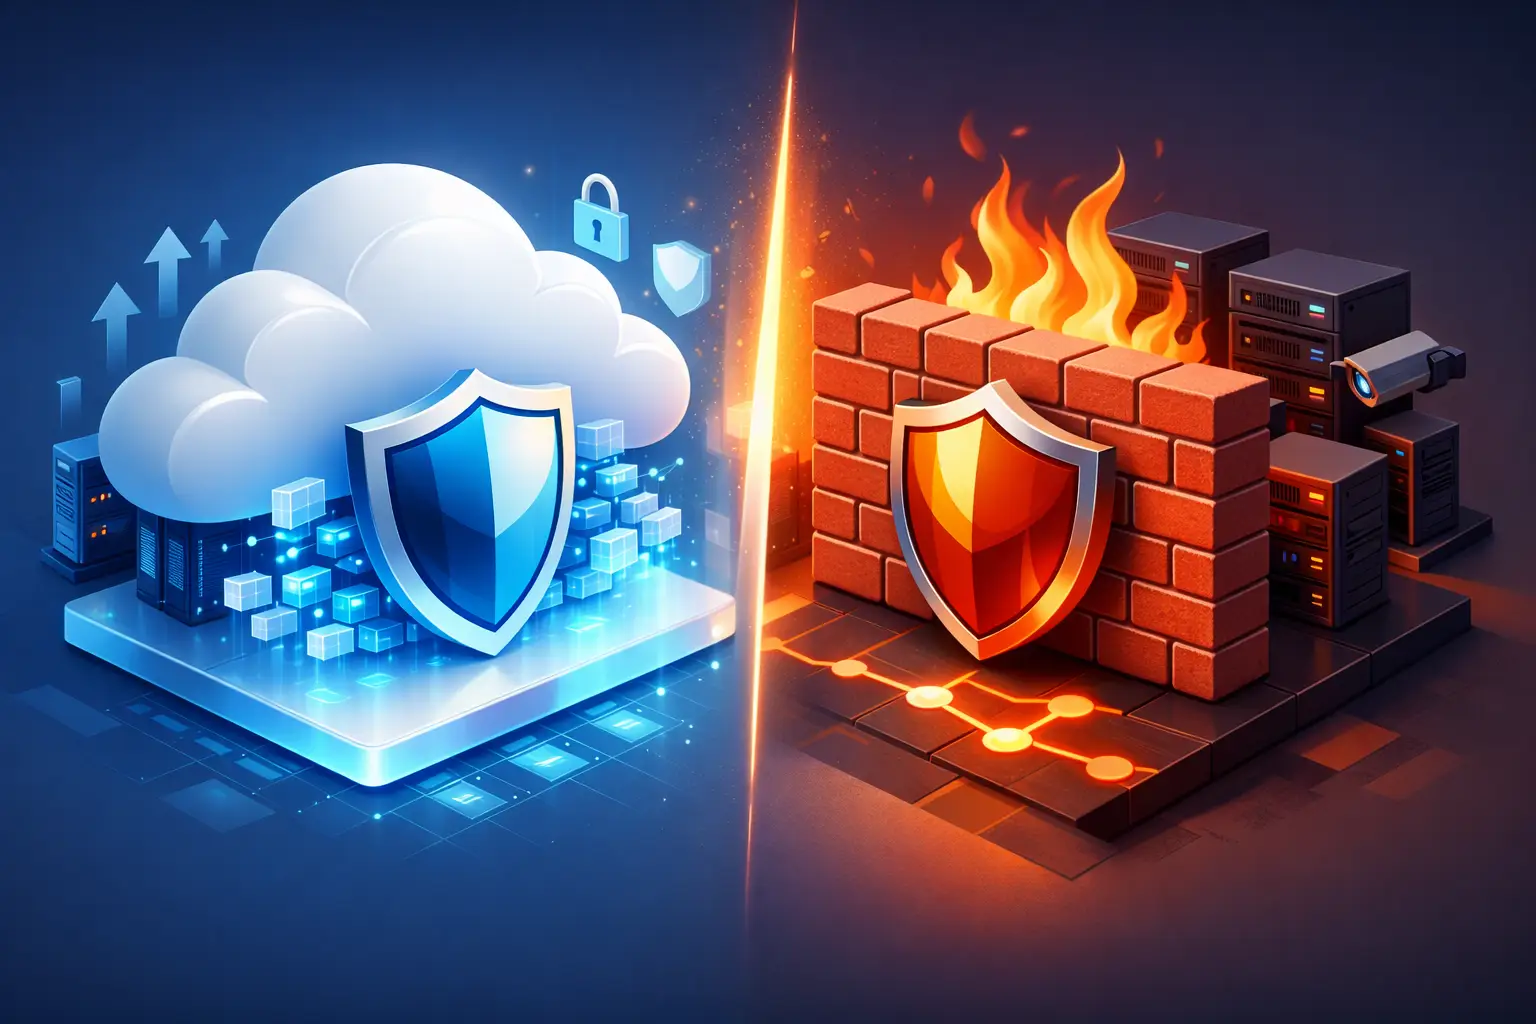
A traditional firewall is typically a physical or virtual device deployed at the edge of a network. It inspects traffic entering and leaving an office, branch location, data center, or other defined environment. Policies are configured around that location, its internet connection, and the devices connected to it.

A cloud firewall delivers similar traffic inspection and policy enforcement from cloud-based infrastructure. Rather than relying entirely on a device at one office, it can apply security controls to users, devices, and cloud workloads wherever they connect. It is often delivered as Firewall as a Service, or FWaaS, and may be part of a broader secure access service edge, commonly called SASE.

Both models can filter traffic, block malicious activity, control applications, and support network segmentation. The difference is where enforcement happens and how easily protection extends beyond the physical perimeter.

That distinction matters when a Dallas office has employees working from home, traveling to client sites, accessing cloud accounting systems, or opening files in Microsoft 365. The old perimeter is no longer the only place where risk enters the business.

How Traditional Firewalls Protect the Business

Traditional firewalls remain a strong choice for organizations with a central office, on-premises servers, specialized equipment, or strict requirements for local network control. A well-configured next-generation firewall can provide intrusion prevention, web filtering, virtual private network access, application control, and detailed network segmentation.

For example, a manufacturing company may need to isolate production equipment from office workstations. A healthcare practice may need to separate guest Wi-Fi, clinical systems, and administrative devices. A physical firewall at each location can enforce those boundaries close to the devices and maintain predictable local performance.

There are trade-offs. Hardware must be sized correctly, maintained, patched, monitored, and eventually replaced. Security policies can become inconsistent when a business has multiple offices or a mix of firewalls from different vendors. Remote users often connect through a VPN, which may route their traffic back through the office before it reaches cloud applications. That can create performance problems and leave IT teams managing more infrastructure than the business needs.

A traditional firewall also only protects what passes through it. If an employee uses a personal internet connection and accesses cloud applications directly, the office firewall may have limited visibility into that activity unless other security controls are in place.

Where Cloud Firewalls Fit Best

Cloud firewalls are designed for businesses whose workforce, applications, and data are distributed. Instead of treating the office as the center of security, they enforce policy based on identity, device condition, user location, application, and risk level.

This approach can make security more consistent. A user working at headquarters, at home, or from a hotel can receive the same web filtering, threat prevention, and access rules. IT teams can manage policy from a centralized console rather than configuring each office separately.

Cloud-based enforcement is particularly useful when a business depends heavily on Software as a Service applications. Routing users directly and securely to Microsoft 365, cloud file platforms, customer relationship management systems, and other approved services can improve the user experience while keeping security controls in place.

Scalability is another practical advantage. When a company opens a new location, hires remote staff, or acquires another business, cloud firewall capacity and policies can usually be extended without waiting for new appliances to be purchased, delivered, and installed. Costs tend to shift from capital purchases and refresh cycles toward recurring subscription expenses.

However, cloud firewalls depend on reliable internet connectivity and thoughtful design. Not every application performs well when traffic is routed through cloud security points of presence. Some legacy systems, industrial controls, and local server environments need protections that remain close to the network. Cloud services also do not remove the need for active monitoring, policy review, identity security, and incident response.

Security Coverage Is More Than a Firewall Choice

A firewall is a critical control, but it is not a complete cybersecurity program. Attackers commonly gain access through stolen credentials, phishing, unpatched systems, misconfigured cloud applications, and compromised vendors. A firewall alone cannot stop every one of those paths.

Effective protection combines network security with multi-factor authentication, endpoint detection and response, email security, backup and disaster recovery, security awareness training, vulnerability management, and 24/7 monitoring. For regulated organizations, documentation and evidence of these controls matter as much as the technology itself.

This is where many businesses make an expensive mistake: they compare firewall features without evaluating who will manage the environment after deployment. An advanced firewall with outdated firmware, permissive rules, ignored alerts, or no tested incident process is not delivering the protection it was purchased to provide.

Whether the firewall is cloud-based or appliance-based, accountability should be clear. Someone must own configuration standards, change management, logging, patching, alert triage, access reviews, and regular security reporting.

Choosing the Right Model for Your Environment

The decision should start with business operations, not product brochures. Consider where employees work, where applications and data reside, how many sites need protection, and how much local infrastructure remains essential.

A traditional firewall may be the better foundation when most work happens at one or several fixed locations, critical systems are on-premises, and local segmentation is a priority. It can also be appropriate where internet reliability is inconsistent or where specialized equipment requires direct local controls.

A cloud firewall may be a better fit when users are distributed, cloud applications are central to daily work, and the business needs the same policies to follow employees across locations. It can reduce administrative overhead for a growing organization with multiple sites or a hybrid workforce.

In many cases, the best answer is a hybrid design. A business may retain next-generation firewalls at offices to protect local devices and networks while using cloud firewall services to secure remote users and access to cloud applications. This layered approach often provides the strongest balance of control, performance, and flexibility.

Questions Leaders Should Ask Before Making a Change

Before replacing a firewall or moving security controls to the cloud, leadership should ask whether the proposed design improves visibility across all users and locations. They should understand which traffic will be inspected, how remote access will work, what happens if an internet connection fails, and who will respond when the firewall detects suspicious behavior.

It is also worth asking how the design supports compliance obligations. Healthcare, legal, financial, and professional services organizations may need documented access controls, audit logs, data protection measures, and incident response procedures. Technology choices should support those requirements rather than create another disconnected tool to manage.

Finally, evaluate the total operating cost. Appliance pricing is only part of the picture. Include licensing, support contracts, internet bandwidth, implementation, monitoring, staff time, hardware refreshes, and the cost of downtime. A lower upfront price can become expensive when it creates gaps that require manual work or slow down employees.

Build Security Around How Your Business Works

The cloud firewall vs traditional firewall discussion should lead to a clearer security architecture, not a rushed product swap. The right design reflects how your people work, where your data lives, and what downtime or a breach would cost the organization.

For many growing businesses, that means combining local network protection with cloud-delivered controls, managed monitoring, and a documented plan for responding to threats. Sigma Networks helps organizations make those decisions with the same discipline used to manage the rest of the technology environment: protect what matters, verify what is working, and plan before risk becomes disruption.

A useful next step is to map one ordinary workday from login to file sharing to customer communication. The places where users, devices, and data leave the office are often the places where your firewall strategy needs to become smarter.

DFW Managed Services That Reduce Business Risk
  • Sep, Sun, 2026

DFW Managed Services That Reduce Business Risk

A ransomware alert at 6:15 a.m. should not force an office manager, controller, or business owner to decide whether the company can open for the day. Yet for many North Texas businesses, that is what IT support still looks like: an urgent call, uncertain recovery options, and no clear owner of the problem.

DFW managed services should change that equation. The right partner does more than answer tickets. It monitors systems before failures interrupt work, manages security around the clock, documents the environment, and helps leadership make technology decisions with business risk in mind.

For small and mid-sized organizations, this is not simply a question of outsourcing help desk support. It is a decision about how much downtime, cyber exposure, and operational uncertainty the business is willing to carry.

What DFW Managed Services Should Deliver

Managed services are a recurring model for operating and improving a company’s technology. Instead of calling a provider only when equipment fails, the business receives ongoing support, monitoring, maintenance, security oversight, and planning under a defined service relationship.

That distinction matters. Break-fix support is reactive by design. It may solve the immediate issue, but it does not necessarily address the missing software patch, weak access policy, aging firewall, untested backup, or undocumented network change that caused the issue in the first place.

A capable managed service provider takes ownership of the technology operating model. That typically includes user support, endpoint management, network oversight, Microsoft 365 administration, backup monitoring, vendor coordination, and strategic guidance. For businesses with an internal IT employee or team, co-managed services can fill gaps in coverage, specialized security, escalation capacity, and long-term planning.

The security component deserves separate attention. An MSP keeps IT operating. An MSSP adds focused security operations, such as managed detection and response, continuous alert monitoring, incident response support, vulnerability management, and security policy guidance. Many businesses need both, particularly when they handle protected health information, financial records, client files, engineering data, or sensitive legal communications.

Why Reactive IT Costs More Than It Appears

The invoice for an emergency repair rarely represents the real cost of a technology failure. The larger loss often comes from employees unable to work, missed customer commitments, delayed billing, lost data, reputational damage, and leadership time diverted from the business.

Consider a professional services firm that loses access to its shared files before a client deadline. Or a manufacturer whose network issue interrupts production scheduling. Or a medical practice that cannot access patient systems. The technical root cause may be small, but the business consequence is not.

Reactive support also makes budgeting difficult. Major expenses arrive without warning because assets were not tracked, lifecycle plans were not created, and risks were not identified early. A managed approach replaces a portion of that uncertainty with visibility. Leadership can see what technology is in place, what needs attention, and where investment will reduce risk or support growth.

That does not mean every IT problem disappears. Hardware fails, software vendors have outages, and threats evolve. The difference is preparation. A documented environment, tested recovery process, monitored security stack, and accountable support team give the organization a far stronger position when something goes wrong.

Security Is Now an Operating Requirement

Cybersecurity is no longer a separate project that can wait until the next budget cycle. Attackers frequently target small and mid-sized businesses because they expect weaker controls, limited monitoring, and backups that may be accessible from the same network they compromise.

Effective protection is layered. Multi-factor authentication helps prevent account takeovers, but it does not replace endpoint monitoring. A firewall matters, but it does not stop every phishing-driven credential theft. Backups are essential, but they must be protected, monitored, and regularly tested to be useful during recovery.

For organizations in healthcare, financial services, legal services, and other regulated fields, security also intersects with compliance. Requirements may vary by industry and customer contract, but the operational expectations are familiar: control access, protect data, retain documentation, train employees, manage vendors, and demonstrate that safeguards are actually working.

A managed security program should translate those expectations into practical action. That includes identifying high-risk gaps, establishing standards, monitoring for suspicious activity, and maintaining evidence that supports audits, cyber insurance reviews, and client security questionnaires. The goal is not to create paperwork for its own sake. It is to reduce the chance that a preventable failure becomes a business crisis.

The Right Service Model Depends on Your Team

Not every business needs the same level of outsourced IT. A 25-person firm with no internal technical staff has different needs than a 200-person organization with an IT manager who needs better security coverage and escalation support.

Fully managed IT is often the best fit when the business wants one accountable partner to run day-to-day technology. The provider becomes the primary resource for support, maintenance, security coordination, cloud administration, and strategic planning. This model gives leadership a clear point of accountability without the cost of building a full enterprise IT department.

Co-managed IT is appropriate when an internal team already understands the business and handles selected responsibilities well. The outside partner can provide 24/7 monitoring, cybersecurity operations, specialized projects, documentation discipline, backup expertise, and support during employee absences or high-volume periods. A good co-managed relationship strengthens internal IT rather than competing with it.

Some companies only seek a security service after an incident or an insurance renewal exposes weaknesses. That can be a reasonable starting point, but security works best when it is connected to daily IT operations. A security team needs visibility into identities, devices, networks, cloud systems, and backup status. Fragmented responsibility creates blind spots.

Questions to Ask Before Choosing a Provider

The best conversations with managed service providers move beyond hourly rates and ticket counts. Start with accountability. Ask who owns security monitoring after business hours, how incidents are escalated, and whether the provider has a defined process for communicating with leadership during an outage.

Ask how the provider documents your environment and whether you retain access to that documentation. If the relationship ends, your business should not be left without network diagrams, administrative credentials, asset records, licensing details, or recovery procedures.

Ask about service scope as well. Does the agreement include Microsoft 365 administration, endpoint protection, backup oversight, firewall management, user onboarding and offboarding, vendor coordination, and strategic reviews? If services are excluded, make sure leadership understands who is responsible for them.

You should also ask how the provider measures success. Fast response matters, but it is only one signal. Meaningful measures include recurring issue reduction, patch compliance, backup recovery testing, security remediation progress, asset lifecycle status, and completion of planned technology initiatives.

Finally, examine the provider’s approach to recommendations. Technology planning should connect to business objectives, not a product quota. A growing firm may need better collaboration tools, stronger remote access, new communications capabilities, or a network redesign. A stable firm may prioritize lifecycle replacement and security hardening. The right recommendation depends on the organization’s risk tolerance, workflow, and growth plans.

Build a Technology Roadmap Leadership Can Use

IT strategy becomes useful when it is understandable outside the IT department. Executives should be able to see the current state, major risks, recommended priorities, expected costs, and business reasons behind each decision.

A practical roadmap typically addresses near-term remediation, such as closing security gaps or replacing unsupported equipment, while also looking ahead to office expansion, cloud adoption, acquisitions, compliance demands, and workforce changes. It should clarify what must happen now, what can be scheduled, and what is optional.

This is where vCIO or vCTO guidance adds value. Business leaders do not need more technical jargon. They need informed advice that connects technology choices to operational resilience, financial planning, and growth. When IT has a seat in planning conversations, companies can avoid expensive last-minute decisions.

A Better Standard for IT Accountability

Dallas-Fort Worth businesses operate in a market where responsiveness and trust affect every client relationship. Technology should support that standard, not undermine it. The right managed services partner brings disciplined operations, security-first thinking, clear communication, and a plan that evolves with the business.

Sigma Networks helps organizations treat IT as a managed business function rather than a collection of urgent problems. The strongest next step is not waiting for the next outage. It is identifying the gaps that could interrupt your people, customers, and growth, then putting accountable ownership around them.

Best Compliance Tools for Financial Firms
  • Sep, Sat, 2026

Best Compliance Tools for Financial Firms

A regulator, auditor, or client due-diligence team asks for evidence of access controls, security training, retained communications, and incident-response testing. The problem is rarely that a financial firm has no documentation. The problem is that the evidence is scattered across inboxes, shared drives, disconnected IT systems, and individual employees’ knowledge. The best compliance tools financial firms use bring that evidence, accountability, and oversight into a process the business can defend.

For small and mid-sized financial organizations, the right answer is not necessarily the largest governance platform on the market. It is a coordinated set of tools that supports the firm’s actual regulatory obligations, technology environment, and capacity to manage them. A tool that produces more alerts than the team can review creates a new risk instead of reducing one.

What Makes a Compliance Tool Worth the Investment?

Financial firms operate under overlapping expectations. Depending on the business model, that may include SEC or FINRA recordkeeping rules, the Gramm-Leach-Bliley Act Safeguards Rule, state privacy requirements, contractual security obligations, and cybersecurity insurance controls. The tool selection process should begin with those requirements, not with a vendor feature list.

The most useful platforms do three jobs well. They make required activity easier to perform, preserve evidence that the activity occurred, and give leadership a clear view of open risk. If a solution handles only reporting while employees continue to bypass the process, it will not stand up well during a review.

Ease of administration also matters. A regional wealth management firm with a small operations team may not have a dedicated compliance systems administrator. Look for clear ownership, useful reporting, integrations with Microsoft 365 or the firm’s existing identity platform, and a manageable alert volume. Compliance technology should strengthen daily operations, not become another system that requires constant rescue.

The Best Compliance Tools for Financial Firms by Function

The strongest programs typically use a focused technology stack rather than one all-purpose platform. Each category below solves a different control problem.

Governance, Risk, and Compliance Management

GRC platforms centralize policies, risk registers, control assignments, audit evidence, vendor reviews, and remediation tasks. Options such as LogicGate, OneTrust, and Archer are commonly evaluated for this role. They can replace spreadsheets and email-based follow-up with assigned owners, due dates, approval workflows, and audit trails.

For firms with mature compliance teams or multiple regulatory frameworks, a GRC platform can create needed discipline across the organization. The trade-off is implementation effort. A highly configurable platform can be more than a 20-person advisory firm needs, especially if there is no one accountable for maintaining its control library and workflows. Smaller firms may be better served by a simpler compliance management process paired with strong security tooling.

Communications Archiving and Supervision

For broker-dealers, registered investment advisers, and other firms with retention obligations, communications compliance is a distinct requirement. Email retention alone may not be enough. The firm may need to capture, retain, search, and supervise business communications across email, text messaging, collaboration platforms, and mobile devices.

Platforms such as Smarsh and Global Relay are built for this purpose. They support retention and review workflows that standard email backups were not designed to provide. The key question is scope: which communication channels are employees actually using to conduct business? If advisors text clients from personal phones or discuss client matters in unapproved chat apps, the firm has a policy and enforcement issue in addition to a technology issue.

Identity and Access Management

Access control is one of the most visible indicators of a firm’s security maturity. Identity platforms such as Microsoft Entra ID and Okta help enforce multi-factor authentication, conditional access, single sign-on, and timely account removal when employees leave.

For many financial firms, Microsoft Entra ID is a practical starting point because it aligns closely with Microsoft 365. Conditional access can restrict risky logins, require stronger authentication, and limit access based on device health or location. The real value comes from policy design and ongoing review. A firm should know who has administrative privileges, who can access sensitive client data, and whether access is still appropriate after a role change.

Email Security and Data Protection

Email remains a common route for account compromise, wire fraud, and the accidental disclosure of nonpublic personal information. Secure email gateways and advanced phishing protections help reduce malicious messages before users see them. Microsoft Defender for Office 365 and Proofpoint are frequently considered in this category.

Data loss prevention tools add another layer by identifying sensitive information and restricting inappropriate sharing through email, cloud storage, or collaboration tools. Microsoft Purview is often a strong fit for firms already using Microsoft 365 because it supports data classification, retention, eDiscovery, and DLP from the same ecosystem. Configuration is critical. Overly broad policies can interrupt legitimate work, while weak policies can create a false sense of control.

Security Monitoring, Vulnerability Management, and MDR

A written cybersecurity policy does not protect a firm at 2:00 a.m. when an attacker attempts to use stolen credentials. Continuous endpoint monitoring, log analysis, and rapid response are essential controls for organizations handling financial and personal data.

Managed detection and response services, endpoint detection and response platforms, and security information and event management tools provide visibility into suspicious activity. Microsoft Defender for Endpoint, Microsoft Sentinel, CrowdStrike, Rapid7, and Tenable may each have a role, depending on the environment. Vulnerability management identifies systems that need patches or configuration changes; MDR adds skilled human investigation and response when an alert may represent a real threat.

The decision often comes down to staffing. Purchasing a powerful monitoring platform without personnel to tune alerts, investigate incidents, and document outcomes leaves a gap. For smaller firms, a managed security partner can provide the 24/7 oversight and reporting needed to turn security telemetry into a functioning control.

Backup, Recovery, and Business Continuity

Recovery capability is a compliance issue because downtime can affect client service, record availability, and regulatory response. Backup tools should protect key systems, cloud data, and critical line-of-business applications. They should also support immutable or otherwise protected copies that cannot be easily altered by ransomware.

The tool itself is only part of the control. Financial firms should test restoration regularly and document the results. An auditor or insurer will care less about a dashboard showing that backups ran successfully than proof that the firm can recover the files, systems, and data it needs within an acceptable timeframe.

How to Select the Right Compliance Stack

Start with a current-state assessment. Identify the regulations and contractual commitments that apply, where client and financial data resides, which communications channels require retention, and who owns each control. This creates a practical baseline before evaluating products.

Then prioritize the gaps with the greatest business impact. In many firms, the first investments should be multi-factor authentication, secure identity management, protected backups, endpoint security, phishing protection, and documented incident response. A sophisticated GRC platform may be valuable later, but it cannot compensate for unmanaged administrator accounts or missing security logs.

Integration deserves close attention. If security alerts, identity records, device inventories, and evidence repositories remain isolated, reporting becomes manual and slow. A cohesive Microsoft 365 environment, for example, can provide meaningful advantages when identity, email security, endpoint protection, data governance, and audit logging are configured to work together.

Finally, assign operational ownership before signing a contract. Someone must review exceptions, close remediation tasks, test recovery procedures, validate user access, and prepare evidence. Sigma Networks helps financial firms align these technical controls with ongoing management, documentation, and security oversight so compliance is not dependent on a single employee or an annual scramble.

Tools Support Compliance. Accountability Sustains It.

The best technology choices make compliance easier to demonstrate, but they do not replace leadership, policies, training, or consistent enforcement. A financial firm is in a stronger position when its tools produce clear evidence of how it protects client information, manages access, retains required records, and responds when something goes wrong. Build the stack around those outcomes, review it as the business changes, and treat every control as part of the firm’s long-term responsibility to its clients.

Top Backup Mistakes Small Businesses Make
  • Sep, Fri, 2026

Top Backup Mistakes Small Businesses Make

A backup can look successful right up until the moment a business needs it. A green status message, a monthly invoice, and a folder in the cloud do not prove that critical systems can be restored after ransomware, hardware failure, accidental deletion, or a site outage. That gap is behind many of the top backup mistakes small businesses make.

For a law firm, medical practice, manufacturer, or professional services company, recovery is not an IT housekeeping task. It is a business continuity requirement. Lost files can interrupt billing, delay client service, expose regulated data, and turn a manageable incident into days of operational disruption. The right backup strategy is built around what the business must recover, how quickly it must recover it, and who is accountable for proving it works.

The Top Backup Mistakes Small Businesses Make

Treating backup as the same thing as disaster recovery

Backup is a copy of data. Disaster recovery is the ability to restore the systems, applications, access, and communications needed to operate. A company may have protected its file server but still be unable to access email, line-of-business software, network configurations, cloud data, or the credentials required to bring systems back online.

This distinction matters when an outage affects more than one device. If a server fails, can employees work from a replacement system? If the office loses power or becomes inaccessible, can the team operate remotely? If Microsoft 365 is disrupted by deletion or account compromise, is the organization prepared to restore the affected data and identities?

A practical recovery plan identifies dependencies rather than assuming files are the whole story. It documents the order of recovery, responsible contacts, access requirements, and alternate work procedures. The plan should reflect the way your organization actually works, not the way its network looked three years ago.

Assuming cloud applications are automatically backed up

Microsoft 365, Google Workspace, accounting platforms, CRM systems, and industry-specific cloud applications provide valuable availability features. That does not always mean they provide the retention, point-in-time recovery, or independent copy your business needs.

The shared-responsibility model is often misunderstood. A cloud provider is responsible for operating its platform. Your business remains responsible for its users, permissions, records, configuration, and the impact of accidental or malicious deletion. A compromised administrator account can create a serious recovery problem even when the underlying cloud service remains online.

Review every major cloud application individually. Confirm what data can be restored, how far back recovery can go, how long restoration takes, and whether your retention settings satisfy legal, contractual, and regulatory requirements. For healthcare, financial services, and legal organizations, those details may affect more than productivity.

Keeping every backup connected to the production environment

Ransomware operators do not stop at the primary server. They actively look for backup repositories, administrative tools, saved credentials, and cloud management portals. If attackers can reach, encrypt, or delete every copy of your data, the presence of a backup platform offers little protection.

This is why a modern strategy should include isolated or immutable backup copies. Immutability prevents data from being altered or deleted for a defined retention period, even by an account that has been compromised. Offline copies and separate administrative credentials add another layer of protection.

The familiar 3-2-1 approach remains useful: maintain at least three copies of important data, on two different types of storage, with one copy kept offsite. Many businesses now strengthen that approach with an additional immutable or offline copy. The right design depends on your risk profile and budget, but one connected backup destination is rarely enough.

Never testing a real restoration

A backup job can complete without proving that the data inside it is usable. Files may be incomplete, encryption keys may be unavailable, application databases may not be consistent, and recovery instructions may be missing. These problems are often discovered under pressure, when the business can least afford delay.

Testing should go beyond opening a random document. Restore representative files, folders, mailboxes, databases, virtual machines, and key cloud records. Verify that restored applications launch correctly and that users can access the information they need. Record how long each recovery takes.

The goal is to validate two business measures: recovery point objective and recovery time objective. The recovery point objective defines how much data loss is acceptable, such as four hours of work. The recovery time objective defines how quickly a service must be operating again. A company that backs up nightly may accept up to a day of lost changes. For some organizations, that may be tolerable. For others, it is a material operational and compliance risk.

Using one retention policy for everything

Not all data carries the same value or risk. An engineering project, patient record, financial report, signed contract, and temporary marketing file should not necessarily have identical retention and recovery requirements. Yet many organizations apply a default retention period because it is easy to configure, not because it supports the business.

Short retention can be especially dangerous with slow-moving threats. An attacker may gain access, alter data, or establish persistence weeks before detection. If backups roll over too quickly, clean recovery points may no longer exist. On the other hand, retaining all data indefinitely can raise storage costs, complicate records management, and create unnecessary exposure during legal discovery.

Set retention according to business value, contractual obligations, and applicable rules. In regulated industries, align backup retention with formal records policies rather than treating it as an isolated IT setting. This is an area where legal, compliance, operations, and technology leadership should agree on the standard.

Forgetting the systems around the data

Business recovery depends on more than documents and databases. Network configurations, firewall rules, endpoint settings, encryption keys, passwords, software licenses, phone system settings, and vendor contacts can determine whether a restoration proceeds smoothly or stalls.

A useful question is simple: if the office and primary systems were unavailable tomorrow morning, what would the team need to rebuild and resume service? The answer often reveals overlooked dependencies. For example, restoring a server is not enough if the firewall configuration is missing, multifactor authentication cannot be administered, or the accounting application requires a license file that no one can locate.

Maintain secure, current documentation outside the affected environment. Document privileged access procedures carefully, with appropriate controls. The objective is not to create a binder nobody reads. It is to ensure authorized people can act decisively during an incident.

Leaving backup monitoring to chance

Backup failures are common enough that “set it and forget it” is not a strategy. Storage fills up, credentials expire, agents stop reporting, jobs run too slowly, and new devices or workloads are never added to protection. An organization may discover a gap only after the system that was supposed to be protected has already failed.

Backup monitoring should include daily review of failed and missed jobs, capacity trends, unusual deletion activity, and changes to protected workloads. Alerts need a clear owner and escalation path. If an internal IT manager handles this responsibility, leadership should still receive periodic confirmation that recovery controls are being tested and maintained.

For many small and mid-sized businesses, continuous oversight is difficult to sustain alongside normal support demands. Managed backup and disaster recovery services can provide monitoring, documented testing, and accountability, but the provider should be able to explain exactly what is protected, how it is isolated, and how recovery will be coordinated.

Build a Backup Program That Can Recover the Business

A dependable backup program starts with a business impact discussion, not a storage purchase. Identify the systems that support revenue, client service, compliance, and daily operations. Decide the maximum acceptable downtime and data loss for each. Then select backup frequency, retention, isolation, and recovery methods that meet those expectations.

The plan should be reviewed after major changes, including a new line-of-business application, office move, acquisition, cloud migration, or shift to remote work. These changes alter recovery dependencies quickly. A yearly review may be adequate for a stable environment, while a growing company may need more frequent validation.

Sigma Networks helps organizations turn backup from a hopeful safety net into a tested business continuity control. The most useful next step is not waiting for an outage. It is scheduling a recovery test for one critical system, measuring the result honestly, and closing the gaps before they become a business emergency.

Healthcare Access Controls That Protect Care
  • Sep, Thu, 2026

Healthcare Access Controls That Protect Care

A former employee’s active login, a shared front-desk password, or an administrator account used for routine email can create more risk than a sophisticated cyberattack. Healthcare access controls determine who can view, change, send, or delete sensitive information across electronic health records, Microsoft 365, billing systems, imaging platforms, and connected devices. When those controls are poorly managed, patient privacy, clinical operations, and the practice’s reputation are all exposed.

For small and mid-sized healthcare organizations, the objective is not to make every system difficult to use. It is to give the right people the right level of access for the work they are responsible for, then remove that access promptly when roles change. That discipline supports HIPAA compliance, limits the damage from compromised credentials, and helps care teams keep moving when pressure is high.

Why Healthcare Access Controls Are a Business Issue

Access management is often treated as an IT task. In a healthcare setting, it is also an operational and risk-management responsibility. A receptionist may need appointment schedules and demographic information but not clinical notes. A billing specialist may need claims data without unrestricted access to patient charts. A physician may require broad chart access, while a temporary contractor should have a narrow, time-limited account.

The difference matters because most security incidents do not begin with an attacker breaking through a firewall. They often begin with a legitimate account being misused. That can happen after a phishing email captures a password, when a shared credential is passed around, or when an account remains active after an employee leaves.

The consequences reach beyond a compliance finding. Unauthorized access can interrupt appointments, delay claims, expose protected health information, and force leaders to spend valuable time responding to an incident rather than serving patients. For practices operating with lean administrative and IT teams, even a short disruption can create a meaningful financial and patient-service problem.

HIPAA’s Security Rule requires covered entities and business associates to implement reasonable administrative, physical, and technical safeguards. Access controls are a central part of that expectation. They also provide evidence that the organization has made deliberate decisions about who can access electronic protected health information and why.

The Building Blocks of Effective Healthcare Access Controls

Strong controls are not one product or one policy document. They are a coordinated set of technical safeguards, documented processes, and regular oversight. The starting point is an accurate inventory of users, systems, devices, and data.

Role-based access keeps permissions aligned with work

Role-based access control assigns permissions according to a person’s job function rather than personal preference or convenience. Instead of granting broad access each time someone asks for it, the organization defines appropriate access profiles for roles such as physician, nurse, scheduler, billing specialist, office manager, and IT administrator.

This approach reduces unnecessary exposure while making onboarding more consistent. It also makes reviews more practical. Leaders can ask whether a role needs a particular capability rather than examining an unstructured collection of individual permissions.

Role-based access does require nuance. In a small clinic, staff may cover multiple responsibilities, especially during absences or periods of growth. The answer is not to abandon least privilege. It is to document approved exceptions, limit them to the necessary systems, and set an expiration date when temporary elevated access is granted.

Multi-factor authentication protects against stolen passwords

Passwords alone are no longer a sufficient control for email, remote access, cloud applications, or privileged accounts. Multi-factor authentication, or MFA, requires a second verification step such as an authenticator application, security key, or approved push notification.

MFA is especially valuable because email accounts are often the launch point for business email compromise, phishing, and account takeover. Once an attacker controls a mailbox, they may reset passwords for other systems, impersonate leadership, or search for patient and financial information.

Not every MFA method provides equal protection. Text-message codes can be better than passwords alone, but authenticator apps and phishing-resistant security keys generally offer stronger protection for higher-risk accounts. The right choice depends on the practice’s technology environment, workforce needs, and risk profile. What should not be negotiable is MFA for administrators, remote access, email, and any system that stores or provides access to protected health information.

Separate administrative accounts from daily work

IT administrators need elevated privileges to manage systems, but those privileges should not be attached to the same account used for everyday email, browsing, and document work. A compromised standard user account is serious. A compromised administrator account can give an attacker broad control over endpoints, cloud services, backups, and identity systems.

Dedicated administrative accounts, restricted privileged access, and approval workflows create valuable separation. They also improve accountability because administrative actions can be traced to the individual who performed them. For organizations without a full internal security team, managed monitoring of privileged activity can provide another layer of visibility.

Fast onboarding and offboarding close common gaps

Access is not static. New hires need the correct accounts before their first day. Employees moving into a new role need their permissions adjusted. Departing staff, contractors, and temporary workers need access removed immediately when their relationship with the organization ends.

A reliable process connects HR, department leadership, and IT. The notification should identify the person, role, start or end date, required systems, manager approval, and any special access needed. For offboarding, the process should include email, cloud applications, EHR access, remote access, phone systems, shared drives, mobile devices, and physical access where applicable.

The timing is critical. Disabling access at the end of the final working day may be appropriate in some cases. In others, such as an involuntary separation, access must be removed before the conversation occurs. The procedure should support both scenarios without relying on an informal email or memory.

How to Put Healthcare Access Controls Into Practice

A practical improvement plan begins with a risk-based assessment, not a blanket effort to rebuild every permission overnight. Identify the systems that contain protected health information, financial records, credentials, or operationally critical data. Then determine who has access, whether that access is necessary, and whether MFA and logging are enabled.

From there, prioritize the controls that reduce the most risk quickly:

  • Remove inactive accounts, shared credentials, and unnecessary local administrator rights.
  • Enforce MFA for email, remote access, cloud applications, and privileged accounts.
  • Define access roles for major departments and document approved exceptions.
  • Establish a repeatable onboarding, role-change, and offboarding workflow.
  • Schedule periodic access reviews, with closer scrutiny for administrators and high-risk applications.

Periodic reviews are where good intentions become sustained control. Department managers should confirm that their employees still need access, while IT validates that technical permissions match those decisions. A quarterly review may be appropriate for many systems, but privileged accounts and sensitive clinical platforms may warrant more frequent oversight. The right cadence depends on staff turnover, application complexity, and the volume of sensitive data involved.

Logging also matters. If a patient record is accessed unexpectedly, leaders need a way to investigate. Audit logs should be enabled where available, retained according to organizational requirements, and reviewed when alerts or concerns arise. Collecting logs without anyone responsible for monitoring them provides limited value.

Avoid Controls That Disrupt Clinical Work

Security controls fail when employees feel forced to work around them. A nurse who must repeatedly sign in during patient care may seek shortcuts. A physician using an unmanaged personal device may create an unapproved path to information. These behaviors are signals that the workflow needs attention, not simply that the user needs another reminder.

Healthcare organizations need controls that account for real conditions: shared workstations, shift changes, urgent care needs, remote providers, and third-party vendors. Session timeouts, badge-based sign-in, secure password managers, managed mobile devices, and single sign-on can reduce friction when designed thoughtfully.

Convenience should not override security, but security should be implemented with operational context. A strategic IT partner can help a practice balance protection with usability by testing workflows, documenting exceptions, and measuring whether controls are actually being followed.

Accountability Is the Control Behind the Controls

Technology can enforce permissions, but leadership creates the discipline that makes those permissions meaningful. Every healthcare organization should know who owns access decisions, who approves exceptions, who performs reviews, and who is accountable when a control is not working.

For many small and mid-sized practices, that accountability is difficult to maintain internally while managing patients, staffing, billing, and growth. Sigma Networks helps healthcare organizations establish and manage the security processes that protect sensitive systems without turning IT into a constant leadership burden.

The most effective access-control program is not the one with the most restrictions. It is the one that gives clinicians and staff dependable access to what they need, while making unauthorized access difficult, visible, and short-lived. That is how better security supports better care.

VoIP vs Unified Communications: Which Fits?
  • Sep, Wed, 2026

VoIP vs Unified Communications: Which Fits?

A receptionist answers calls at the front desk, a project manager works from a client site, and an executive joins a meeting from a laptop. If each experience requires a different app, number, login, or support process, communications quickly become an operational problem. The VoIP vs unified communications decision is not simply about replacing desk phones. It is about deciding how reliably your people can connect, collaborate, and serve customers without creating more risk for IT.

For small and mid-sized businesses, the distinction matters because the wrong fit can produce hidden costs: missed calls, unmanaged personal devices, confusing licensing, poor call quality, and limited visibility when something fails. The right platform should support how your organization works now while giving leadership a clear path for growth.

VoIP vs Unified Communications: The Core Difference

VoIP, or Voice over Internet Protocol, is the technology that carries phone calls over an internet connection rather than traditional phone lines. A business VoIP service typically provides phone numbers, call routing, voicemail, desk phones or softphone applications, auto attendants, call queues, and basic administrative controls.

Unified communications, often called UC or UCaaS when delivered as a cloud service, is a broader communications environment. It usually includes VoIP calling but brings together additional tools such as team messaging, video meetings, presence status, file sharing, SMS capabilities, and integrations with business applications.

That makes this less of an either-or choice than it first appears. VoIP is often one component of unified communications. The real question is whether your business needs dependable internet-based calling alone or a centrally managed collaboration platform that connects calling with the rest of daily work.

A company with a stable office-based team and straightforward call handling may be well served by a focused VoIP deployment. A distributed professional-services firm that moves between client meetings, office work, and remote collaboration may gain more value from unified communications. Neither option is automatically better. The best decision follows your workflows, compliance obligations, support capacity, and growth plans.

When Business VoIP Is the Right Fit

Business VoIP is a practical choice when voice is the primary requirement and your team does not need every collaboration tool under one platform. It can modernize an aging phone system without forcing a major change in how employees communicate internally.

A well-designed VoIP environment gives organizations useful control over inbound calls. An auto attendant can direct callers to the right department, call queues can prevent busy signals during peak periods, and mobile applications can allow approved employees to answer their business number away from the office. For customer-facing teams, those capabilities can improve responsiveness without adding complicated processes.

VoIP may be the better fit when your organization already has established tools for chat, meetings, and document collaboration. For example, a business that relies heavily on Microsoft 365 might only need a phone solution that works cleanly alongside its existing environment. Buying a broad communications suite with overlapping features can create unnecessary licensing costs and employee confusion.

However, low advertised per-user pricing should not be the deciding factor. Call quality depends on more than the phone service itself. Internet bandwidth, network configuration, Wi-Fi coverage, firewall settings, power protection, and traffic prioritization all affect the experience. A low-cost service on an unmanaged network can still lead to dropped calls and frustrated clients.

When Unified Communications Delivers More Value

Unified communications is designed for businesses where conversations frequently move between calls, meetings, messages, and shared work. Instead of treating each channel as a separate system, UC gives employees a common place to see who is available, start a chat, place a call, schedule a meeting, or continue a customer conversation.

The operational benefit is consistency. A team member can use the same business identity from a desk phone, mobile device, or computer. Managers have fewer disconnected tools to administer, and employees spend less time switching between applications. This is particularly useful for hybrid teams, multi-location organizations, and firms with project-based work.

Consider an engineering firm coordinating site visits, design reviews, and client approvals. Or a legal office where calls, internal messages, and meetings must be available to authorized staff without relying on personal phone numbers. In these cases, unified communications can reduce friction and improve accountability.

UC also supports better continuity when it is planned correctly. If an office loses access to its physical location, authorized employees may still be able to take calls and communicate from another location. That does not eliminate the need for a business continuity plan, but it can make communications more resilient than an on-premises phone system tied to one building.

The trade-off is complexity. More channels, integrations, and device types require stronger user governance. Without clear standards, unified communications can turn into another collection of uncontrolled accounts, chat spaces, and data-sharing paths. The platform should be configured around business roles and security policies, not simply activated with default settings.

Security and Compliance Are Part of the Decision

Voice and collaboration systems carry sensitive information every day: client details, appointment schedules, financial discussions, legal strategy, internal conversations, and authentication requests. For regulated businesses, communications technology must be evaluated as part of the security and compliance program, not as a stand-alone office utility.

Start with identity controls. Multi-factor authentication, role-based access, secure password policies, and prompt removal of former employees reduce the chance that an account becomes an entry point for unauthorized access. Mobile access should be governed as well. Convenience matters, but employees should not be forwarding sensitive business communications into unmanaged personal accounts or applications.

Retention and recording requirements also vary. A financial services organization may need to retain certain communications, while a healthcare or legal business may need careful policies around recordings, transcripts, and shared files. Features can support compliance, but features alone do not establish compliance. Your organization still needs documented policies, appropriate configurations, access reviews, and user training.

Network security matters just as much. Voice traffic should be separated and prioritized where appropriate, firewalls should be correctly configured, and unusual activity should be monitored. Toll fraud, account compromise, phishing delivered through collaboration platforms, and unauthorized call forwarding are real business risks. A security-first provider will assess the full environment instead of treating the phone system as outside the cybersecurity scope.

Evaluate the Experience Beyond the Feature List

Most providers can offer calling, voicemail, video, and chat. The more meaningful differences appear in deployment quality, management discipline, and support accountability.

Before selecting a platform, map the calls and conversations that keep your business running. How are after-hours calls handled? Which employees need mobile access? Do receptionists require busy-lamp fields or advanced routing? Are there shared areas, warehouses, conference rooms, or locations with poor Wi-Fi? Do teams need to send business text messages, and how will those messages be retained or monitored?

Also consider integrations with the systems your staff already uses. A CRM integration may help sales teams document customer interactions. A help desk or scheduling integration may make service calls easier to manage. But every integration adds administrative and security considerations. Choose integrations that solve a specific workflow problem rather than adding features no one owns.

Cost should be measured as total operating cost, not just monthly licenses. Include implementation, porting numbers, devices, headsets, network upgrades, training, support, compliance needs, and the internal time required to administer the platform. A cheaper service that requires frequent troubleshooting can become the more expensive choice.

Questions leadership should ask

Ask providers how they handle emergency calling and location updates, what happens during an internet outage, and whether call routing can fail over to mobile devices or alternate sites. Confirm who owns number porting, user onboarding, changes, and offboarding. Request clarity on support response expectations, billing terms, feature limitations, and the security controls included in the service.

These questions are especially valuable for DFW businesses with multiple offices, field staff, or plans to grow through acquisition. Communications problems tend to surface at the worst time: during a client emergency, office move, staffing transition, or network outage. Designing for those moments is more valuable than selecting a platform based on a demonstration alone.

Make Communications a Managed Business Service

The strongest communications strategy is not defined by whether it is labeled VoIP or unified communications. It is defined by whether calls reach the right people, employees can work productively from approved devices, leaders can manage costs and access, and the system remains dependable during disruption.

Treat your communications platform as part of your broader IT, security, and continuity plan. With the right assessment, clear governance, and ongoing support, it becomes a dependable service your team barely has to think about – which is exactly how business communications should feel.

PCI DSS Readiness Guide for Growing Businesses
  • Aug, Mon, 2026

PCI DSS Readiness Guide for Growing Businesses

A PCI DSS readiness guide should begin with one practical question: where does cardholder data actually enter, move through, and leave your business? Many organizations assume PCI compliance is an IT checklist. It is a business-wide responsibility that affects payment workflows, vendors, employee access, incident response, and the evidence you can produce when an acquirer asks for it.

For small and mid-sized businesses, the goal is not to create an oversized compliance program. The goal is to reduce the card-data environment to the smallest practical footprint, apply the right controls consistently, and make accountability clear. That approach lowers assessment burden while reducing the likelihood that a payment-card incident disrupts operations, damages customer trust, or creates costly contractual exposure.

Start With PCI DSS Scope

PCI DSS applies to organizations that store, process, or transmit cardholder data, as well as systems that can affect the security of the cardholder data environment. Scope is often broader than leaders expect. A workstation that accesses a payment portal, a network segment connected to payment systems, or an administrator account capable of changing a payment-related configuration may all be relevant.

Begin by documenting each payment path. Include in-person terminals, e-commerce checkout pages, virtual terminals, mobile devices, recurring billing platforms, call-center processes, and any third-party payment service providers. Then identify the people, devices, applications, networks, and vendors involved at each point.

This exercise frequently reveals unnecessary risk. For example, an employee may be writing card numbers in a ticket, spreadsheet, or email before entering them into a virtual terminal. Even if the payment platform itself is compliant, that manual process can pull additional systems into scope. Reworking the workflow to use a hosted payment page or approved terminal can reduce both risk and compliance effort.

Scope reduction is not a shortcut around PCI DSS. It is disciplined architecture. The less cardholder data your business handles directly, the easier it is to protect the environment that remains.

Determine Your Validation Path

Your merchant bank or acquirer determines the validation requirements that apply to your organization. Depending on transaction volume, payment channels, and the way your systems handle card data, you may be required to complete a Self-Assessment Questionnaire, an Attestation of Compliance, quarterly vulnerability scans, or a formal Report on Compliance performed by a qualified assessor.

Do not select an SAQ simply because it appears easiest. The correct questionnaire depends on your payment model and technical environment. A business using only validated, standalone terminals has a different obligation than one that accepts payments through an e-commerce site or key-enters payments through a browser-based virtual terminal.

A readiness effort should confirm three things early: which validation documents apply, who owns submission deadlines, and what evidence must be retained throughout the year. Treating compliance as an annual form-filling event creates unnecessary pressure and often exposes control gaps too late.

Build Controls Around the Highest-Risk Gaps

PCI DSS contains detailed requirements, but most readiness challenges fall into a handful of operational areas. Leadership should focus on whether those controls work consistently, not merely whether a policy says they exist.

Protect Card Data From the Start

The strongest control is avoiding storage when there is no business need to retain cardholder data. Confirm that staff are prohibited from collecting card data through email, text messages, chat platforms, paper notes, or unapproved applications. If data must be retained for a legitimate and documented reason, encryption, retention limits, secure deletion, and tightly controlled access become essential.

Never assume masking makes a system safe to include card data. Systems that display, transmit, or can reconstruct protected information still require careful evaluation. Payment tokens can reduce exposure, but the implementation and surrounding workflow still matter.

Secure Identities and Administrative Access

Compromised credentials remain one of the most common paths into business systems. Multifactor authentication should protect remote access, administrative accounts, cloud management portals, and access to the cardholder data environment. Each user needs a unique account, and access should be based on job function rather than convenience.

Review access regularly, especially after role changes and terminations. Shared administrator credentials, old vendor accounts, and broad permissions create gaps that are difficult to defend during an assessment and even harder to investigate after an incident.

Maintain Secure Systems and Networks

Payment systems need a defined patching process, endpoint protection, secure configuration standards, and vulnerability management. The practical standard is straightforward: know what you have, know what software is running, know which systems are exposed, and address meaningful weaknesses within established timelines.

Network segmentation can materially reduce scope, but only when it is designed and tested. Separating payment devices or payment-related systems from general office networks limits the impact of a compromised user device. A firewall rule on paper is not enough. Configuration reviews and periodic testing should demonstrate that the separation actually works.

Monitor, Log, and Test

When a security event occurs, the organization must be able to determine what happened, who accessed affected systems, and whether card data was exposed. Centralized logging, time synchronization, alerting, and log review support that investigation capability.

Testing is equally important. External vulnerability scans may be required through an approved scanning vendor, while internal scanning and penetration testing expectations depend on the environment and validation path. Failed scans should trigger remediation, retesting, and documented closure. A scan report without follow-through is not evidence of readiness.

Make Documentation Match Reality

Policies are valuable only when they describe the controls employees actually follow. A PCI DSS program should include clear ownership for access management, vulnerability remediation, vendor oversight, incident response, security awareness, and evidence collection.

Keep documentation usable. An access-control policy should identify who approves access, how often access is reviewed, and how emergency access is handled. An incident response plan should name decision-makers, explain how payment partners are contacted, and define how evidence is preserved. A vendor register should identify which providers touch payment processes and confirm that their compliance responsibilities have been reviewed.

Employee training deserves more than a yearly checkbox. Staff who answer phones, manage invoices, process payments, support customers, or administer systems need instructions that match their role. They should know how to recognize prohibited card-data handling, phishing attempts, suspicious payment activity, and escalation procedures.

Use Evidence as a Management Tool

Assessment readiness improves when evidence is collected as controls operate. Maintain records of completed access reviews, patch reports, scan results, security awareness training, vendor attestations, firewall changes, incident exercises, and remediation decisions.

This creates two benefits. First, it prevents the familiar scramble to reconstruct a year of activity before an assessment. Second, it gives leadership a better view of whether security operations are working between audits. Compliance evidence is not administrative overhead when it reveals missed deadlines, unmanaged assets, or unclear ownership before those gaps become incidents.

For businesses with limited internal IT capacity, this is where a managed IT and cybersecurity partner can add real value. The right partner can help maintain asset inventories, monitor systems, coordinate remediation, document recurring controls, and provide executive reporting. Accountability should remain clear, however. Outsourcing a function does not outsource the business responsibility to protect payment data.

A Practical PCI DSS Readiness Guide Timeline

A focused readiness project often begins with discovery and scope confirmation, followed by a gap assessment against the applicable PCI DSS requirements. The next phase should prioritize high-risk issues such as unsupported systems, missing multifactor authentication, excessive access, unsegmented networks, weak payment workflows, and absent logging.

After remediation, validate the changes through scans, testing, and evidence review. Then complete the appropriate assessment documents only after the controls are operating as intended. The timeline depends on the complexity of the environment. A company using outsourced terminals may have a relatively narrow project, while a business with e-commerce integrations, multiple locations, or legacy applications may need a longer, more coordinated effort.

Avoid treating every requirement as equally urgent. A risk-based plan should address exposures that could allow unauthorized access to payment systems first, while also building the operating discipline needed to sustain compliance. That balance is what turns PCI DSS from a stressful annual event into a manageable part of business operations.

Payment security is ultimately a trust commitment. Start by mapping the real flow of card data, assign owners to the controls that protect it, and keep evidence as the work is done. That gives your business a stronger position long before the next assessment request arrives.

Legal Office Data Retention Policy Basics
  • Aug, Sat, 2026

Legal Office Data Retention Policy Basics

A misplaced client file is an operational problem. A deleted file needed for litigation, a bar complaint, an audit, or a malpractice defense can become a business-critical event. A legal office data retention policy gives a firm a defensible way to decide what it keeps, where it is stored, who can access it, and when it can be securely destroyed.

For small and mid-sized firms, this is not simply a records-management exercise. Retention affects client confidentiality, e-discovery readiness, cyber insurance, cloud administration, storage cost, and the ability to recover after ransomware. The right policy must be practical enough for attorneys and staff to follow every day, while being controlled enough to stand up to scrutiny.

What a Legal Office Data Retention Policy Should Accomplish

A retention policy is a documented set of rules for preserving and disposing of information. In a legal environment, those rules need to account for professional conduct obligations, client agreements, applicable statutes of limitation, court rules, tax requirements, and the firm’s own risk tolerance.

The policy should cover more than closed matter folders in a document management system. Law firms create and retain information across email, Microsoft 365 or Google Workspace, legal case-management platforms, file shares, scanned documents, voicemail, text messages, accounting systems, backups, endpoint devices, and collaboration tools. If the policy applies only to one repository, the firm still has unmanaged records elsewhere.

A sound policy has two equally important purposes: preserving information that must remain available and eliminating information that no longer serves a legal, contractual, or business purpose. Keeping everything forever may feel safer, but it increases storage expense, discovery exposure, and the impact of a breach. Deleting information too early creates an even more obvious risk. The goal is a controlled, documented middle ground.

Start With Record Categories, Not One Universal Timeline

A single rule such as “keep all files for seven years” is rarely sufficient. Different records have different retention needs, and a firm’s governing jurisdictions and practice areas matter. A family law firm, a personal injury practice, and a corporate law office may face different client-file requirements and evidentiary considerations.

Begin by inventorying the types of information your firm holds. Client matter files, engagement letters, trust-account records, billing data, attorney work product, personnel files, tax documents, vendor contracts, security logs, and marketing contacts should not automatically receive the same retention period.

For each category, assign an owner and define the retention trigger. The trigger might be matter closure, final payment, contract termination, employee separation, or the end of a tax year. This detail prevents confusion. “Seven years” is not actionable unless staff know seven years from when.

Your firm should also document the authority behind each timeline. That may include state bar guidance, a court rule, a client contract, an insurance requirement, or advice from legal counsel. Technology providers can help implement retention controls, but the firm should have qualified legal guidance on the retention periods themselves.

Litigation Holds Override Routine Deletion

The most important exception in any retention policy is the legal hold. When a firm reasonably anticipates litigation, receives a subpoena, faces an investigation, or becomes aware of a relevant dispute, routine deletion must stop for potentially relevant information.

This is where many otherwise well-written policies fail. A schedule may say that email is automatically deleted after a set period, but an automated rule cannot continue removing messages subject to a hold. The firm needs a clear process to identify custodians, preserve relevant data sources, suspend deletion, document the hold, and release it only when the matter is resolved.

Legal holds should extend beyond email. Relevant information may be in shared drives, Teams or Slack messages, mobile devices, voicemail systems, cloud applications, backup archives, and personal devices approved for business use. A policy that ignores these systems creates false confidence.

Build the Policy Around How Your Firm Actually Works

A policy nobody can follow is not a control. It is a liability. The most effective approach maps retention requirements to the firm’s real workflows, from client intake through matter closure and final disposition.

For example, designate who closes a matter, who confirms the file is complete, who sends any required client notice, and who authorizes destruction after the retention period ends. Define where the official client record lives. If attorneys are saving versions on local desktops, in personal cloud accounts, and in email inboxes, the firm cannot reliably apply retention or prove that destruction was complete.

The policy should also address client requests. Some clients may require longer retention, a particular secure return method, or preservation of original records. Those requirements should be captured in the engagement process rather than handled informally after a matter closes.

A workable operating model typically includes these controls:

  • A records schedule that identifies categories, retention periods, triggers, owners, and governing authority.
  • A documented legal-hold procedure that suspends deletion across all relevant systems.
  • Approved storage locations with role-based access, multifactor authentication, encryption, and audit logging.
  • A repeatable destruction process that records what was deleted, when it was deleted, and under whose authority.

These controls make retention measurable. They also reduce dependence on individual attorneys remembering deadlines or manually cleaning out old files.

Secure Storage Is Part of Retention

Retaining a document is not the same as protecting it. A legal office holds highly sensitive material: personally identifiable information, financial records, privileged communications, medical information, business plans, and credentials. A retention policy should therefore work alongside the firm’s cybersecurity program.

At a minimum, retained records should be stored in approved systems protected by multifactor authentication and access based on job role. Administrative access should be limited and reviewed regularly. Encryption should protect data at rest and in transit, while audit logs should show who accessed, changed, shared, or deleted important records.

Backup strategy deserves special attention. Backups support recovery from accidental deletion, hardware failure, and ransomware, but they are not a substitute for a retention policy. Backup copies may preserve data beyond its normal disposal date, and immutable backups may be intentionally difficult to alter or delete. The policy should define backup retention separately, explain how legal holds affect backups, and ensure recovery testing is performed on a regular schedule.

For firms using Microsoft 365, cloud file sharing, and multiple legal applications, retention settings must be coordinated. Otherwise, a document deleted from one platform may remain in a mailbox, a recycle bin, a synced laptop, or a third-party backup. Central visibility matters because unmanaged copies are a common source of both discovery risk and data leakage.

Do Not Treat Disposal as a Simple Delete Button

When the approved retention period ends and no hold applies, records should be disposed of in a way that is secure and defensible. Paper files may require cross-cut shredding or a vetted destruction provider. Electronic records may require secure deletion procedures, deletion from active systems, and appropriate handling of physical drives at end of life.

Not every copy can disappear instantly from every backup archive, particularly where immutable backup architecture is used. That is acceptable when the firm understands the limitation, restricts access to those archives, and allows the data to age out according to a defined schedule. What matters is that the process is deliberate, documented, and aligned with the firm’s stated controls.

Maintain a destruction log for significant records. The log does not need to expose confidential client details, but it should establish the category of information, authorized disposal date, method, and approving party. If questions arise later, this documentation helps show that deletion followed an ordinary policy rather than an attempt to conceal information.

Review the Policy as Systems and Risks Change

A retention policy should be reviewed at least annually and whenever the firm changes a major system, opens a new practice area, adopts AI-enabled tools, merges with another practice, or experiences a security incident. Technology changes faster than many written policies. If staff begin using a new collaboration platform before it is included in retention and legal-hold procedures, the firm has created a blind spot.

Training is equally necessary. Attorneys, paralegals, and administrative staff should understand the official storage locations, the difference between routine cleanup and a legal hold, and the process for reporting a suspected preservation issue. Brief, recurring training is usually more effective than a lengthy policy sent once by email.

For DFW legal offices and firms operating across Texas, a disciplined retention program is a practical sign of operational maturity. It protects client trust, reduces avoidable exposure, and makes the firm easier to defend when a request for records arrives. The strongest policy is not the longest document. It is the one your people can follow, your technology can enforce, and your leadership can confidently explain.

Office hours:

Send us a message: