Manufacturing Ransomware Recovery Example
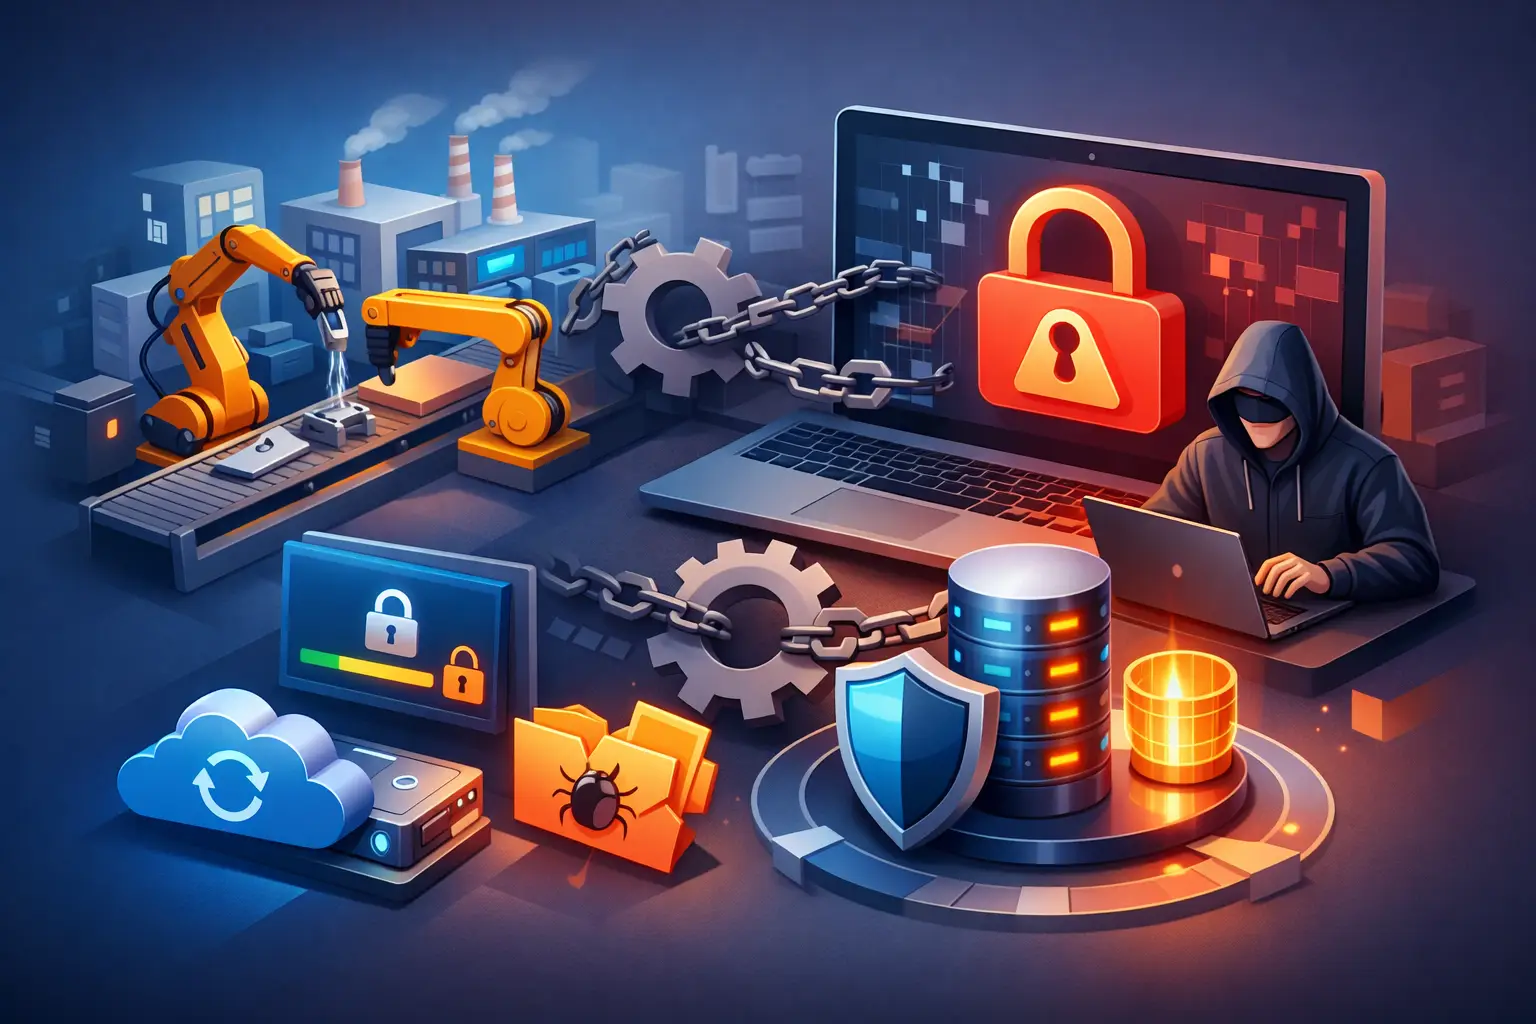
A production line stopped at 6:12 a.m. is not an IT inconvenience. It is missed shipments, idle labor, delayed raw-material deliveries, and customers asking whether their orders will move this week. This manufacturing ransomware recovery example shows what a disciplined response can look like when an attack reaches systems that support the shop floor.
The scenario is a composite based on common manufacturing risks, not a single company. The details matter because ransomware recovery is not simply restoring files. A manufacturer must make safe decisions about identity systems, production scheduling, ERP data, quality records, plant connectivity, and the evidence needed for insurance, legal, and regulatory obligations.
The manufacturing ransomware recovery example
A mid-sized components manufacturer operates one primary facility and a small distribution warehouse. Its 180 employees rely on Microsoft 365 for communications, an ERP platform for orders and inventory, a file server for engineering drawings, and network-connected workstations used for production scheduling and quality documentation. Some production equipment is isolated from the corporate network, but the scheduling terminals are not.
On a Monday morning, employees report that shared files will not open. Within minutes, the IT team finds ransomware notes on file shares and encrypted virtual machines. The attackers have also disabled several endpoint tools and used a compromised administrator account to move through the environment.
The immediate temptation is to bring systems back online as quickly as possible. That is how organizations reinfect restored systems or lose forensic evidence. The recovery team instead treats the first hours as a business continuity event with a security investigation running alongside it.
First priority: contain the spread without stopping safe production
The company disconnects affected servers and workstations from the network, disables the compromised accounts, and blocks remote access paths until they can be reviewed. The team preserves logs, ransom notes, and system images before making major changes. Its cyber insurance carrier and legal counsel are notified early, which helps coordinate breach-response obligations and communications.
Plant leadership is brought into the response immediately. Rather than shutting down every machine, operations identifies what can continue safely using local controls, printed work orders, and manual inventory checks. The company pauses new automated scheduling changes, but keeps several production cells running where equipment is segmented and operators can verify specifications without relying on compromised systems.
This distinction is critical. The goal is not to keep every process moving at any cost. It is to maintain safe, controlled production while preventing the attacker from reaching additional systems or corrupting business records.
Recovery begins with clean systems, not encrypted files
The incident response team determines that the ransomware entered through a phishing email and then exploited an account without multifactor authentication. The attacker had access long enough to identify backup systems and attempt to delete recovery points. Fortunately, the manufacturer had separate, immutable backups that could not be altered through the compromised administrator account.
Before restoring data, the team rebuilds core identity services from known-good configurations. Administrator passwords are reset, multifactor authentication is enforced, stale accounts are removed, and endpoint security tools are reinstalled. This takes time, but restoring servers before securing identity would hand the attacker a second opportunity.
The company restores in a deliberate order. Communications and identity come first, allowing leaders and employees to coordinate through approved channels. Next comes the ERP environment, because it drives orders, purchasing, inventory, and shipping. Engineering drawings and quality documentation follow, then less time-sensitive departmental file shares.
Not every workload requires the same recovery target. A production schedule may need restoration within hours, while archived HR documents can wait. Defining these priorities before an incident prevents a technical team from spending valuable time on the wrong systems.
Validate data before returning it to operations
A restored ERP database is not automatically trustworthy. The manufacturer compares restored order data to recent exports, warehouse records, and paper documentation created during the outage. Quality leaders confirm that current revision-controlled drawings are available before production resumes at full capacity. Finance reconciles invoices and purchase orders that may have been entered or changed near the time of the attack.
This validation step creates a trade-off. It delays full normalization, but it avoids a more expensive problem: producing the wrong part, shipping against inaccurate inventory, or losing traceability for regulated customers. For manufacturers serving aerospace, healthcare, defense, or automotive supply chains, incomplete records can create compliance and contractual exposure long after the encryption is removed.
Why this recovery worked better than most
The company did not avoid disruption. It lost access to key systems for nearly two days and ran reduced operations while the recovery team worked. What limited the damage was preparation built around business dependencies rather than a generic backup checklist.
Several controls made the difference. Backups were protected from routine administrative access and tested regularly. Network segmentation reduced the attacker’s ability to move directly from office systems into every production asset. Leadership had documented recovery priorities and knew who could authorize downtime decisions. The company also had a managed security team monitoring alerts around the clock, which accelerated detection and helped preserve evidence.
Most significantly, the organization had practiced the question that matters during a ransomware event: what must be restored first for the business to operate safely? The answer was not “all servers.” It was a sequence of capabilities: secure communication, verified identity, order visibility, production scheduling, quality control, and shipping.
That sequence may differ by facility. A make-to-order manufacturer may place engineering files ahead of warehouse systems. A high-volume operation may prioritize manufacturing execution software and plant-floor connectivity. The right plan reflects how revenue, safety, and customer commitments actually move through the organization.
Where manufacturing recovery plans commonly fail
Many manufacturers maintain backups but cannot state whether those backups are isolated, immutable, complete, or fast enough to meet production requirements. A backup that takes five days to restore may protect data, yet still fail the business when customers expect shipments in 48 hours.
Another common failure is treating operational technology and IT as separate conversations. Production equipment may be segmented, but the systems used to schedule work, store specifications, manage quality records, or remotely support machinery often connect the two environments. Recovery planning must account for those dependencies without allowing a rushed IT restoration to create a plant-floor safety issue.
Communication also breaks down when responsibility is unclear. Executives need concise updates on downtime, financial exposure, and decision points. Operations needs practical direction about what can run manually. Employees need a trusted communication channel so they do not use personal email, unapproved file-sharing tools, or suspicious instructions from an attacker impersonating leadership.
Turn the example into a recovery plan
A practical ransomware recovery plan starts with a short, accurate inventory of systems that affect production, shipping, finance, engineering, and compliance. For each system, document its business owner, dependencies, acceptable downtime, recovery source, and validation process. Include cloud services, third-party vendors, remote access tools, and shared accounts, not just servers in the rack.
Then test the plan under realistic conditions. Restore a critical application into an isolated environment. Confirm that users can authenticate, that the recovered data is usable, and that the process can be completed within the promised recovery window. Tabletop exercises should include operations, finance, HR, legal, and leadership, because ransomware decisions are rarely made by IT alone.
Security controls should support recovery, not compete with it. Multifactor authentication, least-privilege access, endpoint detection and response, monitored backups, network segmentation, and 24/7 alerting all reduce the chance that a single compromised account becomes a plant-wide outage. For smaller manufacturers without a large internal security team, a managed IT and security partner can provide the monitoring, documentation, and response coordination that recovery requires.
The best time to measure whether your organization can recover is during a controlled test, when a delayed shipment is hypothetical. A clear recovery plan gives leadership room to make deliberate decisions when the factory floor is anything but calm.
