Microsoft 365 Migration Example for SMBs
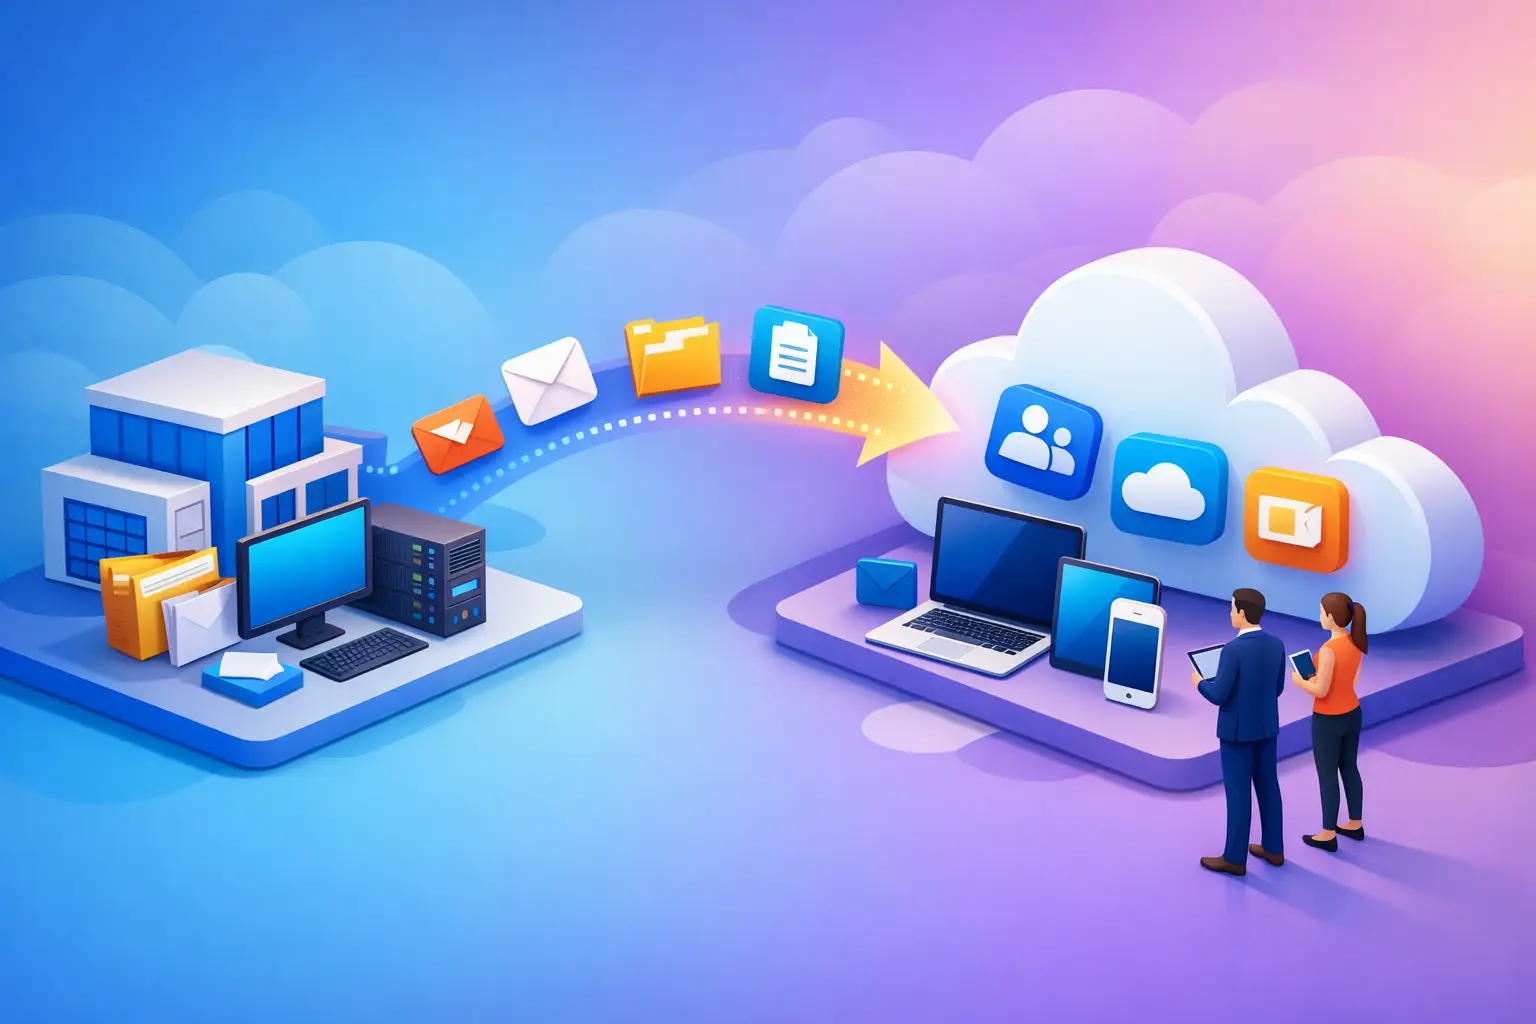
A Microsoft 365 migration example is most useful when it reflects the reality of a growing business: email cannot stop, client records cannot disappear, and employees still need to work while the change is underway. A well-run migration is not simply a mailbox transfer. It is a controlled business continuity project that improves security, collaboration, and accountability without creating avoidable disruption.
Consider a 75-person professional services firm with offices in Dallas and North Texas. The firm relies on a mix of aging email hosting, shared network drives, personal cloud storage accounts, and a basic remote-access setup. It handles confidential client documents, must retain certain records, and has employees working from offices, homes, and client locations. Leadership wants a standard platform that can support growth without adding administrative burden to its operations team.
Microsoft 365 is the right destination, but the outcome depends on how the firm plans, secures, and governs the move.
Microsoft 365 Migration Example: The Starting Point
Before migration, the firm’s email was hosted through a legacy provider. Most staff accessed mail through Outlook, but mobile configurations varied widely. Some employees forwarded business email to personal accounts for convenience. File storage was even less consistent: active projects lived on a shared server, completed work sat in archived folders, and several teams used unsanctioned file-sharing tools to exchange large documents.
This arrangement created more than an inconvenience. It made access difficult to manage, complicated offboarding, and left leadership with limited visibility into where sensitive information resided. A ransomware event, a lost phone, or a departing employee could expose weaknesses that had accumulated over years.
The goal was not to move every file and setting exactly as it existed. That approach only carries old problems into a new platform. The goal was to establish a secure, usable operating model built around Exchange Online, Teams, SharePoint, OneDrive, and identity controls.
Phase One: Assess What Should Move
The first step was discovery. The IT team identified 82 mailboxes, including active users, shared addresses, conference rooms, and former employee accounts. It also reviewed aliases, distribution lists, external forwarding rules, mobile devices, line-of-business applications that send email, and DNS records.
For files, the firm reviewed approximately 3 TB of data. Not all of it belonged in Microsoft 365. Old software installers, redundant archives, and duplicate departmental folders were excluded or moved to lower-cost archival storage. Active client work, current templates, internal policies, and department-owned documents were categorized for SharePoint or Teams. Individual working files moved to OneDrive.
This classification work takes time, but it reduces risk. A migration team needs answers to practical questions before data starts moving: Who owns this folder? Who should retain access? Does it contain regulated or confidential information? Is there a retention requirement? Can the business safely dispose of it?
For a healthcare, legal, financial, or engineering firm, these questions are also compliance questions. Microsoft 365 can support stronger controls, but no platform automatically fixes weak data ownership or poor retention practices.
Phase Two: Build Security Before the Cutover
The firm did not wait until after the migration to address security. Before the first mailbox moved, the project team established a baseline configuration designed to protect accounts from common threats.
Multifactor authentication was required for all users, with stronger sign-in requirements for administrators. Legacy authentication protocols were reviewed and disabled where they were no longer necessary. Conditional access policies were configured to restrict risky sign-ins and require compliant devices for sensitive access. Administrative roles were limited according to job responsibility rather than assigned broadly for convenience.
Email security was also strengthened. Anti-phishing, anti-malware, and spam policies were tuned to the firm’s risk profile. External sender labeling and mailbox auditing helped users and administrators distinguish legitimate communication from impersonation attempts. Domain protection settings were prepared to reduce the risk of email spoofing.
These controls are often treated as technical details. They are business safeguards. Email remains one of the most common entry points for account compromise, wire fraud, and ransomware. Moving to Microsoft 365 without configuring identity and email security can simply place valuable data in a better-known target.
Phase Three: Pilot With the People Who Will Notice Problems
The firm selected 12 pilot users from operations, finance, leadership, and client service. The group included both technically confident employees and people who preferred established processes. That mix was intentional. A pilot that includes only power users may miss the usability issues that create help desk volume later.
Pilot mailboxes were migrated first, followed by a limited set of shared files and Teams channels. The team tested calendar sharing, mobile access, large attachments, external collaboration, multifunction printer scanning, and email delivery from the firm’s practice management system.
One issue surfaced quickly: several automated systems still relied on outdated SMTP settings. Another was more operational. Client-service staff needed a clearer process for sharing documents externally without creating anonymous public links. Both issues were corrected before the organization-wide cutover.
The pilot also shaped training. Employees did not need a long technical presentation about every Microsoft 365 feature. They needed to know where their files would live, how to access them from approved devices, how to identify suspicious messages, and whom to contact when something did not work.
Phase Four: Move Email and Files in Controlled Waves
The final migration took place in stages. Mailboxes were pre-synchronized in advance so that only recent changes needed to transfer during each cutover window. Users were scheduled in groups based on department needs and time sensitivity. Finance and executive mailboxes received additional planning because even short disruptions could affect approvals and client commitments.
The migration team communicated clearly before each wave. Staff received their scheduled cutover date, sign-in instructions, MFA enrollment guidance, mobile-device steps, and a direct support path. Managers were briefed on what to expect so they could plan around high-priority meetings or deadlines.
File migration required a different pace. The firm moved department libraries into SharePoint and Teams with permissions based on business roles. Instead of replicating every legacy folder permission, the team simplified access where possible. Excessively complex permissions can be hard to audit and even harder to support.
Personal working files moved to OneDrive, with training on when to use OneDrive versus a shared Teams or SharePoint location. That distinction matters. OneDrive is appropriate for an individual’s draft work and controlled sharing. Team-owned records, client deliverables, and operational documents should live where the appropriate group retains access when an employee changes roles or leaves.
What Changed After the Migration
Within weeks, the firm had a more consistent work environment. Employees used a single business identity for email, files, meetings, and approved collaboration. Mobile access was easier to manage. New hires could be provisioned with defined groups and standardized applications rather than inheriting access through informal requests.
Security improved because the firm had fewer unmanaged accounts, stronger authentication, better logging, and clearer control over external sharing. The organization also gained a foundation for retention policies, device management, backup planning, and incident response.
There were trade-offs. Some long-tenured employees needed extra support as familiar shared-drive workflows changed. SharePoint structure required governance, or it could become another place for documents to sprawl. Licensing needed periodic review as roles and security requirements evolved. Microsoft 365 reduces infrastructure overhead, but it does not remove the need for ongoing administration.
The Difference Between a Move and a Managed Environment
A successful migration is measured by more than whether mail arrives on Monday morning. The stronger test is whether the business is easier to protect, support, audit, and scale afterward.
For many small and mid-sized businesses, that requires a partner who can manage the technical project alongside the operational details: security policies, user communications, data decisions, cutover support, documentation, and post-migration governance. Sigma Networks approaches Microsoft 365 work as part of a broader security-first IT strategy, not as a one-time data transfer.
The right migration creates breathing room for the business. When identity, email, collaboration, and data protection are organized with intent, leaders can spend less time worrying about where information lives and more time directing where the company goes next.
