IT Consultant Versus MSP: Which Fits Your Business?
A server failure at 9:00 a.m., a suspicious Microsoft 365 login, or a compliance questionnaire due Friday exposes a critical question: who owns the outcome? When comparing an IT consultant versus MSP, the real difference is not simply who can fix technology. It is whether your business has dependable, ongoing accountability for technology performance, cybersecurity, and planning.
For a small or mid-sized business, either model can be useful. The right choice depends on your internal capabilities, risk profile, growth plans, and tolerance for downtime. The mistake is assuming a talented individual consultant and a managed service provider deliver the same operating model.
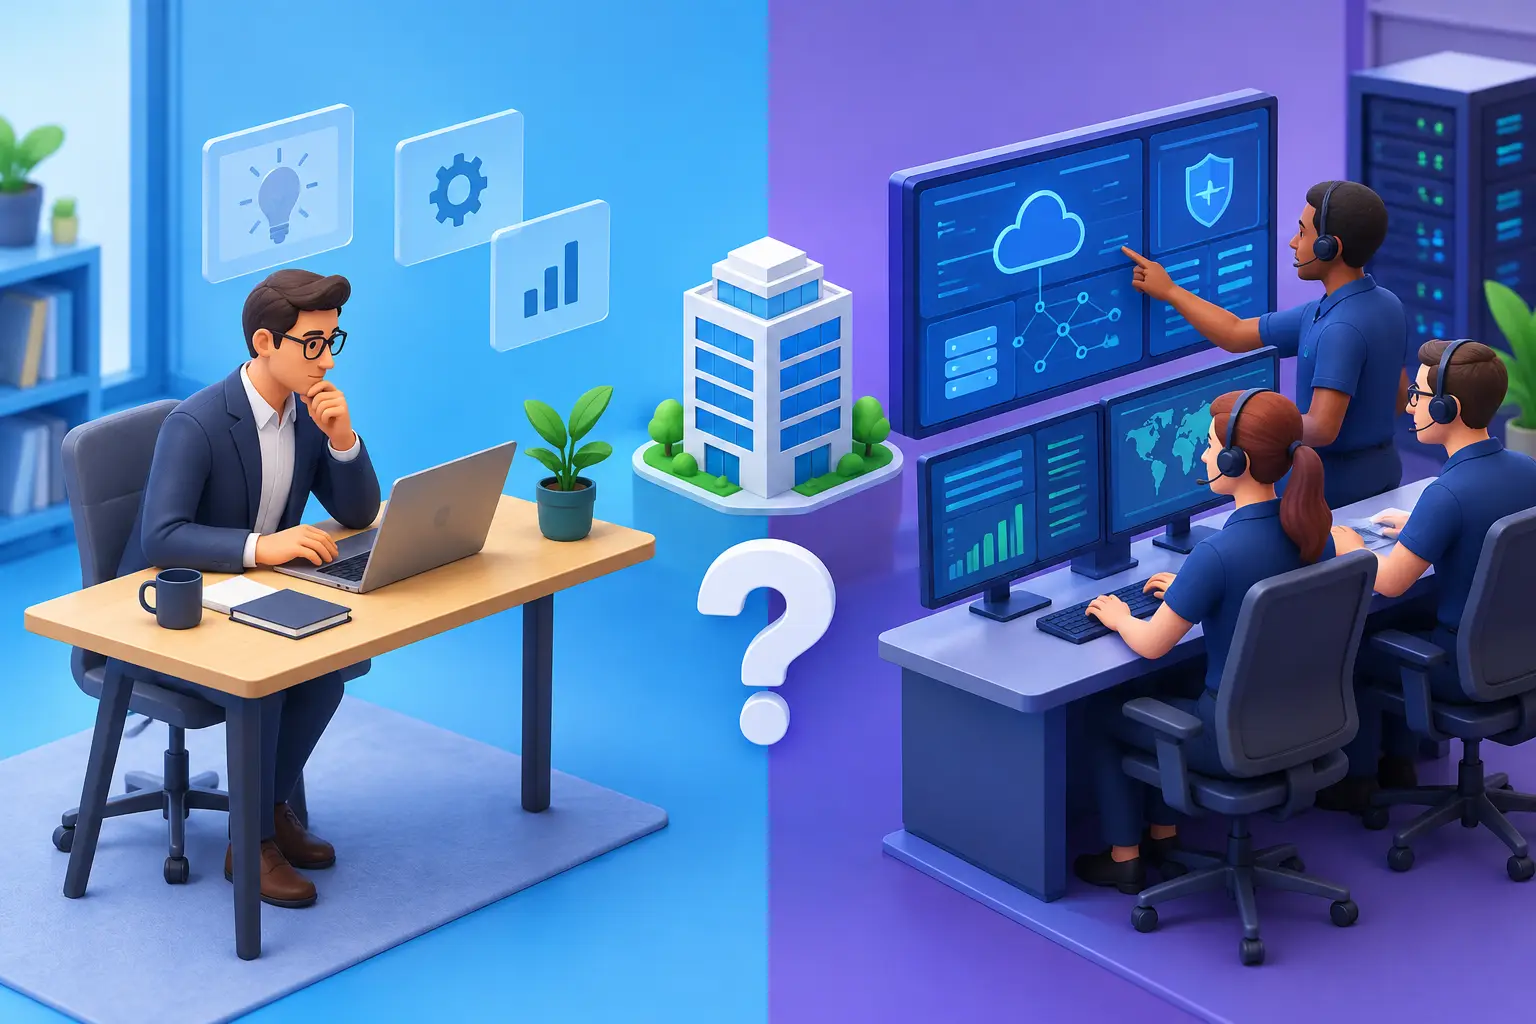
IT Consultant Versus MSP: The Core Difference
An IT consultant is typically engaged for expertise, projects, advice, or specific technical problems. They may design a network, lead a cloud migration, assess security gaps, help select software, or step in when internal staff need specialized knowledge. A strong consultant can bring valuable perspective without requiring a long-term service commitment.
An MSP, or managed service provider, takes recurring responsibility for defined areas of your IT environment. That commonly includes user support, device management, network monitoring, patching, backups, vendor coordination, cybersecurity tools, documentation, and technology planning. The relationship is designed around continuous operation rather than a series of individual requests.
That distinction matters because businesses do not experience technology risk only during projects. Risks develop between projects: an unpatched laptop, an employee who clicks a credential-harvesting email, a backup that has not been tested, or an internet outage with no documented failover plan. An MSP is built to identify and reduce those recurring operational risks.
What an IT consultant does well
A consultant is often an effective choice when the work has a clear beginning, end, and scope. For example, a 25-person architecture firm may need an assessment before moving files and applications to the cloud. A manufacturer may need help selecting a new ERP platform. A business with a capable internal IT manager may bring in a consultant to validate a network redesign or address a difficult compliance requirement.
This model can be flexible. You pay for a defined outcome, gain access to specialized skills, and avoid paying for services you do not need. It can also be a practical way to get executive-level guidance before committing to a broader technology strategy.
The trade-off is continuity. A consultant may know your environment well during an engagement, but they are not necessarily monitoring it every day, managing every endpoint, documenting every change, or responding to after-hours security alerts. Those responsibilities must remain with internal staff or be assigned elsewhere.
What an MSP is designed to manage
An MSP provides a repeatable operating model for businesses that need technology to work consistently without building a full enterprise IT department. Instead of waiting for a problem to become disruptive, the provider monitors systems, applies maintenance, standardizes configurations, and tracks issues over time.
A mature MSP relationship should include more than a help desk. It should establish clear service ownership, documented standards, predictable support channels, and regular conversations about business priorities. If your company opens a second location, hires rapidly, adopts new applications, or must meet client security requirements, your IT provider should help prepare the environment rather than merely react after the fact.
For many organizations, security is the deciding factor. Managed IT services can include endpoint protection, identity controls, email security, vulnerability management, backup oversight, and incident response coordination. When these services are paired with 24/7 monitoring and managed detection and response, the provider moves closer to an MSSP model focused specifically on security operations.
Compare the Models by Business Outcome
Cost is often the first comparison point, but it should not be the only one. Hourly consulting can appear less expensive until a prolonged outage, ransomware event, failed audit, or repeated emergency call exposes the cost of gaps in coverage.
An IT consultant usually bills by the hour, project, or retainer. This can work well for discrete needs and makes spending easy to tie to a particular initiative. However, the budget may become unpredictable when problems arise unexpectedly. There can also be pressure to defer preventive work because it creates immediate billable expense without an obvious short-term crisis.
An MSP typically uses a monthly recurring model based on users, devices, locations, or a defined service package. The right agreement makes ongoing IT costs more predictable and encourages prevention. Because the provider is responsible for maintaining a stable environment, reducing recurring incidents benefits both parties.
Responsiveness also differs. A consultant may be highly responsive, especially if they have a long-standing relationship with your company. But availability is tied to that person’s schedule and capacity. If they are in the middle of another client project, on vacation, or no longer available, your business may have limited coverage.
An MSP should provide a team structure, escalation path, service-level expectations, and documented access to your systems. That does not mean every MSP offers the same quality. Ask who answers after-hours calls, how urgent incidents are prioritized, whether procedures are documented, and what happens when your primary technician is unavailable.
Strategic planning is another dividing line. A consultant can provide excellent strategic counsel. Yet ongoing planning requires current information about asset health, recurring support issues, security posture, licensing, backup results, and upcoming business changes. An MSP that manages the environment daily has a stronger foundation for vCIO or vCTO guidance because recommendations can be tied to operational evidence.
When a Consultant Is the Better Fit
Choose a consultant when your business has reliable internal ownership of day-to-day IT and needs focused outside expertise. This may include an internal IT team that needs help with a specialized migration, an acquisition, an application rollout, or an independent review of its security controls.
A consultant can also be the right short-term answer for a small organization with simple technology needs and a low-risk operating model. Even then, leadership should identify who handles patching, backup checks, user onboarding, cybersecurity incidents, vendor management, and emergencies. If the answer is “we will call someone when it breaks,” the business is accepting avoidable operational risk.
Consulting works best when scope is specific and ownership is clear. Define the deliverables, timeline, decision-makers, documentation requirements, and post-project support expectations before work begins.
When an MSP Is the Better Fit
An MSP is usually the better fit when technology downtime affects revenue, client service, compliance, or employee productivity. It is particularly valuable for organizations with no internal IT department, a small internal team stretched across too many responsibilities, multiple locations, remote users, or sensitive data.
Healthcare practices, law firms, financial services organizations, engineering firms, and manufacturers often need more than occasional technical help. They need consistent user access, protected data, auditable processes, dependable backups, and a response plan for security events. Those needs require discipline over time, not just technical skill during a project.
A co-managed model can be especially effective for businesses with internal IT leadership. Rather than replacing the team, the MSP handles routine support, monitoring, security operations, or specialized infrastructure work. Internal staff can then focus on applications, business process improvements, and projects that require organizational knowledge.
For DFW businesses facing rapid growth or stricter client security expectations, a security-first MSP can provide the operating maturity that is difficult to build internally. Sigma Networks, for example, combines managed IT, cybersecurity operations, and strategic advisory so clients have one accountable partner across the technology environment.
Questions to Ask Before You Choose
The most useful decision comes from examining responsibility, not marketing labels. Ask a prospective consultant or MSP how they handle 24/7 incidents, how often they test backups, who owns cybersecurity monitoring, how they document systems and credentials, and how they report on service performance.
Also ask what is excluded. Some providers offer monitoring but not remediation. Others provide help desk support but treat security, backup testing, compliance preparation, and strategic planning as separate services. There is nothing inherently wrong with a narrower scope, provided leadership understands the gaps and assigns ownership.
Finally, look for evidence of accountability. You should know who is responsible for keeping systems current, reducing repeated problems, advising leadership, and coordinating recovery when an incident occurs. The answer should be specific, measurable, and documented in the service agreement.
The best choice is the one that gives your business the right level of coverage for its real risk. A consultant can solve a defined problem exceptionally well. An MSP can create the ongoing discipline that keeps many problems from becoming business interruptions. Choose the partner model that lets your team spend less time wondering whether technology will hold up and more time moving the business forward.
