SOC Versus Internal Security Team: Which Fits?

SOC Versus Internal Security Team: Which Fits?

A ransomware alert at 2:13 a.m. does not wait for the IT manager to return from vacation. That is the practical issue behind the SOC versus internal security team decision. Business leaders are not simply choosing who receives alerts. They are deciding how consistently the company can detect threats, contain incidents, protect sensitive data, and document its security posture when the stakes are high.

For small and mid-sized businesses, the answer is rarely as simple as outsourcing everything or hiring more people. The right model depends on your risk, regulatory obligations, existing IT capability, budget, and tolerance for business disruption.

SOC Versus Internal Security Team: The Core Difference

A security operations center, or SOC, is a dedicated function for continuously monitoring, investigating, and responding to cybersecurity events. A managed SOC is typically provided by an MSSP and supported by security analysts, threat intelligence, monitoring tools, documented response processes, and around-the-clock coverage.

An internal security team is made up of employees who work directly for your organization. Depending on company size, that could mean a security manager, a systems administrator with security responsibilities, an IT director, or a larger team with specialized roles in engineering, governance, compliance, and incident response.

The key distinction is not just who employs the people. It is the operating model. A SOC is built to maintain continuous visibility and incident response at scale. An internal team is often better positioned to understand the business context behind a system, user, vendor, or operational exception.

A well-run security program needs both capabilities. The real question is whether your organization can build and sustain them internally, or whether a managed security partner should provide the monitoring and response layer.

What an Internal Security Team Does Well

Internal teams bring institutional knowledge that is hard to replicate quickly. They understand which applications are business-critical, which employees need elevated access, how a manufacturing line or legal case-management system operates, and when an unusual login may actually be legitimate.

That context improves decision-making. An internal security leader can align security investments with business plans, help executives prioritize risk, and work directly with departments that may resist operational changes. They can also own policy development, vendor reviews, user training, asset lifecycle planning, and compliance coordination.

For organizations with complex environments, significant proprietary systems, or strict regulatory requirements, internal leadership is especially valuable. Healthcare groups, financial firms, engineering companies, and multi-location businesses often need someone accountable for security decisions within the organization.

However, internal ownership does not automatically create 24/7 protection. A skilled IT manager may be excellent at infrastructure, projects, and user support while still lacking the time, tooling, or specialized analyst coverage needed to investigate security events at all hours. Assigning security to an already busy IT generalist can create a dangerous gap between policy and real-world response.

Where a Managed SOC Adds Value

A managed SOC provides depth that is difficult for most mid-sized organizations to assemble internally. It can monitor endpoint, network, cloud, email, identity, and log data continuously, then triage suspicious activity using a defined process. When an event is confirmed, analysts can escalate it, recommend containment, and in many service models take approved response actions.

This matters because attackers do not work business hours. Credential misuse, malicious inbox rules, impossible travel alerts, and ransomware behaviors can emerge overnight, on weekends, or during periods when internal IT is focused on a major project.

A SOC also brings repeatable operational discipline. Analysts work from playbooks, correlate indicators across multiple systems, and have access to threat intelligence that helps distinguish ordinary noise from activity requiring immediate attention. That can reduce alert fatigue for internal staff and shorten the time between detection and action.

For businesses that need stronger security without building an enterprise-scale department, a managed SOC can provide a predictable monthly operating model. It is often more practical than hiring enough people to staff a round-the-clock operation, especially when recruiting and retaining experienced security professionals is difficult.

Still, a SOC is not a substitute for basic IT hygiene or leadership. Monitoring cannot compensate for unmanaged devices, weak identity controls, missing backups, undocumented systems, or a lack of executive decisions about acceptable risk.

Cost Is More Than Salary Versus Subscription

Many organizations begin the SOC versus internal security team comparison with price. That is reasonable, but the comparison needs to be complete.

The cost of an internal team includes salary, benefits, recruiting, training, certifications, management time, coverage for absences, security platforms, log storage, and incident-response readiness. One security hire can improve your posture, but one person cannot provide continuous coverage, specialized analysis, and reliable redundancy.

A managed SOC turns much of that operational expense into a defined service cost. Yet not all services provide the same value. Some vendors primarily forward alerts. Others investigate, prioritize, and assist with response. Decision-makers should understand what is monitored, who validates alerts, how fast critical events are escalated, and whether the provider can take containment actions when authorized.

The most meaningful financial comparison includes the cost of an incident. A few hours of downtime, a compromised email account, a missed compliance obligation, or a failed recovery can cost far more than the monthly difference between security models.

Control, Accountability, and Response Authority

Business leaders sometimes worry that outsourcing security means giving up control. In a properly structured relationship, it should mean gaining clearer accountability.

Your organization should retain ownership of its systems, data, risk decisions, and security policies. The provider should operate within agreed response procedures, maintain documentation, report on security activity, and escalate decisions that require business judgment. For example, a managed SOC may isolate a suspected infected device under a preapproved process, while a business leader decides whether to shut down a revenue-critical application during a broader incident.

Clear response authority matters before an incident occurs. If a suspicious login is detected, who can disable the account? If an endpoint shows ransomware behavior, who can isolate it? If a vendor system is involved, who contacts the vendor? Ambiguity adds minutes when minutes matter.

An internal team may have faster access to stakeholders and stronger authority over business systems. A managed SOC may have faster threat validation and wider security coverage. The strongest programs define how those strengths work together rather than forcing an either-or decision.

The Hybrid Model Is Often the Best Fit

For many growing companies, the practical answer is co-managed security. Internal IT or technology leadership owns the business relationship, strategic priorities, system knowledge, and day-to-day coordination. A managed security partner supplies 24/7 monitoring, managed detection and response, security expertise, and incident support.

This model avoids a common failure point: expecting a small internal team to be both strategic and continuously reactive. Your internal people can focus on improving infrastructure, supporting users, completing projects, and guiding the business. The SOC watches for threats and helps ensure a serious event does not sit unnoticed in a queue.

It also creates a better path for maturity. A company can begin with managed endpoint protection, identity security, email protection, backup oversight, and monitoring. As its needs evolve, it can formalize incident-response plans, compliance reporting, risk assessments, tabletop exercises, and executive technology planning.

How to Choose the Right Model

Start with your exposure, not a preferred service label. A professional services firm that stores client financial information has different requirements than a small office with limited systems. A healthcare organization subject to HIPAA, a manufacturer with operational technology, or a law firm managing confidential records may need higher levels of monitoring, documentation, and response preparedness.

Next, assess what your internal team can reliably do today. Can someone review critical alerts after hours? Is there a current inventory of devices and privileged accounts? Are backups tested? Does the business have a documented incident-response plan? Can leadership produce security evidence for a client, insurer, or auditor without a scramble?

If the answer to several of those questions is no, a managed SOC can close meaningful gaps quickly. If you already have mature security leadership and a capable internal team, external SOC coverage can still add scale, specialized tools, and off-hours protection.

Security operations are not a badge of independence. They are a business continuity function. Choose the model that gives your organization clear ownership, dependable response, and the confidence to keep operating when a threat becomes real.
Who Needs Cyber Insurance? A Business Risk Test

Who Needs Cyber Insurance? A Business Risk Test

A single fraudulent email can trigger more than an IT problem. It can halt invoicing, expose client records, interrupt operations, and force leadership into costly decisions under pressure. So, who needs cyber insurance? For most small and mid-sized businesses that rely on email, cloud systems, digital payments, customer data, or connected vendors, the more useful question is whether they can comfortably absorb the financial impact of a cyber incident without it.

Cyber insurance is not reserved for large corporations with dedicated security teams. It is a business continuity tool for organizations that would face meaningful expense, downtime, contractual fallout, or reputational damage after an attack. The right policy can help fund recovery. It does not replace strong cybersecurity, disciplined IT management, or employee training.

Who Needs Cyber Insurance Most?

Any organization that stores, processes, transmits, or depends on sensitive digital information should evaluate cyber insurance. That includes companies that believe they are “too small” to attract attention. Cybercriminals often target small and mid-sized businesses precisely because their controls, recovery resources, and internal security staff may be limited.

The need becomes more urgent when an incident would affect customers, revenue, compliance obligations, or the ability to deliver services. A ransomware event that locks a manufacturer out of production systems, a business email compromise that redirects a law firm’s payment, or a phishing attack that exposes a medical practice’s patient information can all create losses that extend well beyond the initial technical repair.

Organizations in healthcare, legal services, financial services, engineering, architecture, consulting, manufacturing, and professional services commonly have a clear exposure. They manage confidential records, intellectual property, payment data, regulated information, or operational systems that cannot be unavailable for long.

However, industry alone does not determine the answer. A five-person consulting firm that holds client credentials and receives electronic payments may have more cyber exposure than a larger business with limited data and segmented systems. The issue is how deeply technology is connected to the company’s revenue, obligations, and reputation.

The Business Risks a Cyber Policy Can Address

Cyber insurance policies vary, but they generally help with the financial consequences of a covered event. First-party coverage may address costs your business directly incurs, such as incident response, forensic investigation, data recovery, business interruption, breach notification, credit monitoring, ransomware-related expenses where legally permitted, and public relations support.

Third-party coverage may help when clients, partners, regulators, or other parties claim your organization failed to protect information or meet contractual obligations. Depending on the policy and circumstances, this can include legal defense, settlements, judgments, and certain regulatory costs.

This distinction matters. Restoring servers after ransomware is expensive, but it may not be the largest cost. A firm may also lose billable hours, miss contractual deadlines, face notification requirements, or need to explain an incident to clients who trusted it with sensitive information. Those secondary effects can strain cash flow and leadership capacity at the same time.

Coverage is never automatic. Policies include limits, retentions, exclusions, sublimits, and conditions. Some may limit coverage for funds transfer fraud, impose specific ransomware conditions, or exclude incidents tied to inadequate controls. Business leaders should review policy language with their insurance broker and legal counsel rather than assuming every cyber loss is covered.

Signs Your Business Has a Meaningful Cyber Insurance Need

A practical risk review should start with operations, not fear. Cyber insurance deserves serious consideration if your business depends on Microsoft 365, cloud applications, remote access, online banking, e-commerce, VoIP, automated equipment, or a networked line-of-business platform to operate.

It is also a strong consideration if you keep personally identifiable information, protected health information, financial records, payment card data, employee data, proprietary designs, or confidential client documents. The more sensitive the information, the higher the potential cost of notification, legal review, remediation, and lost trust.

Contractual requirements are another signal. Larger customers, government entities, healthcare partners, and financial institutions increasingly require vendors to carry cyber liability coverage. They may also require proof of security practices before awarding or renewing a contract. Without a policy and documented safeguards, a growing business can find itself excluded from valuable opportunities.

Finally, consider the recovery question: if systems were unavailable for several days, could the company continue serving customers, paying employees, and communicating reliably? If the answer is no, cyber insurance should be part of a broader resilience strategy.

Why Strong Security Still Comes First

Cyber insurance transfers some financial risk. It does not prevent phishing, secure an exposed account, restore an untested backup, or make an unprepared employee recognize a fraudulent wire request. Insurers know this, which is why underwriting has become more demanding.

Many carriers expect controls such as multi-factor authentication, endpoint protection, secure backups, email security, access management, vulnerability management, documented incident response procedures, and security awareness training. Requirements differ by carrier and policy, but the direction is clear: businesses must demonstrate reasonable security hygiene to obtain favorable coverage and avoid disputes after a claim.

This creates a useful discipline. The controls that support insurability are often the same controls that reduce the odds and impact of an incident. A managed IT and cybersecurity partner can help identify gaps, maintain evidence of security practices, monitor threats, and build a recovery plan that works under real-world pressure.

For example, multi-factor authentication can stop many account takeover attempts, but it needs to be deployed correctly across email, remote access, administrative accounts, and critical cloud services. Backups matter, but they must be isolated where appropriate, monitored, and regularly tested for restoration. A policy cannot compensate for discovering too late that recovery data is incomplete.

How Much Coverage Is Enough?

There is no universal coverage amount. A professional services firm with 20 employees may need a very different policy than a 200-person manufacturer, even if their revenue is similar. The appropriate limit depends on the volume and sensitivity of data, the probable duration of downtime, contractual commitments, available cash reserves, and the potential for funds transfer fraud or legal claims.

Business owners should also pay attention to the retention, which is the amount the company pays before coverage applies. A lower premium can look attractive until a retention is too high to manage during a disruptive event. Sublimits deserve equal attention. A policy may offer a substantial overall limit while providing far less for social engineering, business interruption, or digital asset restoration.

Ask direct questions before buying or renewing a policy. Does it cover an attack on a cloud provider or managed service provider? How is business interruption calculated? Are dependent business interruptions covered when a critical vendor goes down? Is wire fraud coverage separate? Which security controls are required, and what evidence will be expected if a claim is filed?

The answers should align with the way your business actually operates, not with a generic checklist.

Make Insurance Part of an Incident Plan

The strongest approach connects insurance, security, and response planning before an incident occurs. Keep the policy, carrier hotline, broker contact, legal counsel information, and incident response contacts available outside the primary network. Many policies require prompt notice and may require the insured to use approved breach counsel or forensic providers. Calling the wrong resource first can complicate a claim.

Leadership should also know who can authorize emergency spending, communicate with clients, approve public statements, and make operational decisions during an outage. These responsibilities should not be invented while email is unavailable and systems are encrypted.

Sigma Networks helps businesses build the security foundations that insurers and customers increasingly expect, including 24/7 monitoring, managed detection and response, secure cloud management, backup oversight, and continuity planning. The objective is not merely to qualify for a policy. It is to reduce the chance that your organization ever needs to rely on one.

Cyber insurance is most valuable when it supports a prepared business, not a neglected one. Review your exposure while operations are stable, validate your security controls, and make sure the policy you carry reflects the real cost of keeping your business moving after an incident.

Best Ways to Prevent Downtime for SMBs

Best Ways to Prevent Downtime for SMBs

A down server is not just an IT problem. It can stop billing, delay client work, disrupt phones, prevent access to patient or case files, and leave employees unable to do their jobs. For small and mid-sized businesses, the best ways to prevent downtime begin with treating technology as a business-critical system that requires active oversight, not an expense to revisit only when something fails.

Downtime rarely has one cause. A hardware issue may expose an outdated backup plan. A phishing email may become an account takeover because multifactor authentication was not enforced. A network outage may last longer than necessary because no one documented the recovery process. Prevention means addressing those connected risks before they interrupt operations.

Best Ways to Prevent Downtime Before It Starts

The most dependable approach combines proactive IT management, layered security, tested recovery capabilities, and clear accountability. The goal is not to promise that nothing will ever fail. Hardware, internet carriers, cloud platforms, and people can all fail. The goal is to limit the likelihood of disruption, contain its impact, and restore critical operations quickly when an incident occurs.

Monitor systems around the clock

Many outages give warning signs before they become visible to employees. A server may be running out of storage, a firewall may be dropping connections, a backup job may be failing, or a workstation may be reporting a failing drive. Without monitoring, these warnings often remain unnoticed until a service stops working.

Centralized 24/7 monitoring gives IT teams visibility into the health of endpoints, servers, networks, cloud services, and backup systems. Effective monitoring is more than receiving alerts. Alerts must be prioritized, reviewed, and acted on by people who understand the business impact. A low disk-space alert on a file server, for example, should not wait until Monday morning if that server supports a firm’s daily workflow.

For businesses with internal IT, co-managed monitoring can extend coverage without replacing the existing team. For organizations without a dedicated IT department, a managed services partner provides the consistency and response discipline that reactive support models usually lack.

Keep patching and lifecycle management on schedule

Unpatched software is a common path to ransomware, system instability, and avoidable application failures. Yet patching requires more than clicking update. Updates need to be tested where practical, scheduled to reduce disruption, verified after deployment, and documented for compliance purposes.

A disciplined patch management process covers operating systems, browsers, firewalls, productivity applications, line-of-business software, and firmware. It also includes exceptions. Some specialized applications in healthcare, manufacturing, engineering, or legal environments cannot accept every update immediately. In those cases, the right answer is not to ignore the risk. It is to document the exception, add compensating security controls, and establish a safe update plan with the software vendor.

Lifecycle planning matters just as much. Aging servers, unsupported operating systems, end-of-life firewalls, and consumer-grade network equipment introduce risk that cannot be fixed with better help desk response. Replacing critical infrastructure on a planned schedule is less disruptive and more predictable than replacing it during an outage.

Build security into business continuity

Cybersecurity and uptime are inseparable. Ransomware, credential theft, malicious email rules, and unauthorized remote access can all bring operations to a halt. A continuity plan that does not account for cyber incidents is incomplete.

Start with identity protection. Multifactor authentication should be enforced for Microsoft 365, remote access, cloud applications, privileged accounts, and any system containing sensitive business data. Access should follow least-privilege principles, meaning employees have the access they need to perform their roles and no more. When someone changes roles or leaves the company, access must be adjusted or removed promptly.

Email security, endpoint protection, managed detection and response, and security awareness training provide additional layers. No one control catches every threat. The value of layered protection is that a malicious email, stolen password, or missed software vulnerability does not automatically become a company-wide outage.

For regulated businesses, these practices also support compliance obligations. Healthcare, financial services, legal, and professional firms need evidence that security controls, access reviews, and incident processes are managed consistently. Good documentation protects the business when auditors, insurers, or clients ask hard questions.

Protect Data With Backups That Can Actually Restore

A backup is only useful when it can be restored within the timeframe your business can tolerate. That distinction matters. Copying data to a device or cloud service is not the same as proving that your team can recover a deleted file, a corrupted database, or an entire server after a ransomware event.

A practical backup strategy typically maintains multiple copies of important data, separates at least one copy from the production environment, and protects backup access with strong credentials and multifactor authentication. Immutable or otherwise protected backup copies can reduce the risk that attackers encrypt or delete the backups along with the primary systems.

Recovery objectives should be defined in business terms. Recovery time objective, or RTO, answers how quickly a system must be restored. Recovery point objective, or RPO, defines how much data loss is acceptable. An accounting platform that processes daily transactions may need a much tighter RPO than an archive of historical project files. There is a cost trade-off: faster recovery and more frequent backups generally require greater investment. The right design reflects the operational and financial impact of being offline.

Just as critical, test restores on a schedule. Restore a representative file, application, virtual machine, or database and confirm that the recovered data works. Testing exposes gaps in permissions, encryption keys, application dependencies, and recovery documentation while there is time to correct them.

Design the network to avoid single points of failure

A single internet connection, firewall, switch, or power source can become a single point of failure. Not every business needs full redundancy everywhere, but every business should understand which failures would stop critical work and decide whether the risk is acceptable.

For many organizations, a secondary internet connection with automatic failover is a practical investment, especially when cloud applications, VoIP phones, remote access, and customer communication depend on connectivity. Cellular failover may be sufficient for basic continuity, while a second wired circuit may be justified for higher-demand environments.

Network segmentation also limits the spread of an incident. Separating guest Wi-Fi, employee devices, servers, phones, operational technology, and sensitive systems can reduce both security exposure and the scope of network problems. Secure networking is not merely a technical preference. It keeps one issue from becoming an organization-wide interruption.

Create and Rehearse a Business Continuity Plan

Technology recovery does not happen in a vacuum. During an outage, employees need to know who makes decisions, how to communicate with clients, which services take priority, and what work can continue manually. A concise business continuity plan answers those questions before stress and uncertainty take over.

The plan should identify critical applications, key vendors, recovery contacts, escalation paths, and alternative communication methods. It should also establish an incident communications process. If email and phones are unavailable, how will leadership coordinate? If a client portal is offline, who communicates status updates and expected next steps?

Run tabletop exercises at least annually and after major technology changes. A tabletop exercise does not need to be elaborate. Walk through a realistic scenario, such as ransomware affecting shared files or an internet outage affecting phones and cloud access. Identify what the team would do, where decisions could stall, and whether the documented plan matches current systems and responsibilities.

Give technology ownership a seat at the leadership table

Many downtime risks are created by business decisions made without a technology review: opening a new office, adopting a new SaaS platform, changing a workflow, acquiring another company, or delaying a hardware refresh. Strategic IT planning brings infrastructure, security, compliance, and budget considerations into those discussions early.

A vCIO or vCTO function can help leadership translate technology risk into business priorities. Rather than reacting to a growing list of support tickets, leaders can review a documented technology roadmap, risk register, lifecycle plan, and recovery priorities. This creates accountability for the decisions that shape resilience over time.

Sigma Networks helps organizations apply this security-first operating model across managed IT, cybersecurity, backup, cloud services, and communications. The focus is straightforward: keep people productive, protect critical systems, and give leadership a clear view of technology risk.

The best time to improve resilience is when the business is operating normally. Review the systems your teams cannot work without, test whether they can be recovered, and assign ownership for the gaps you find. That work may not feel urgent on a quiet day, but it is what protects the business when the unexpected happens.

10 Best Secure File Sharing Platforms for SMBs

10 Best Secure File Sharing Platforms for SMBs

A client portal, a cloud drive, and an email attachment can all move the same document. They do not create the same level of control. For businesses handling contracts, financial records, protected health information, engineering files, or client data, the best secure file sharing platforms provide more than a place to upload documents. They help enforce access rules, preserve audit trails, limit accidental exposure, and keep work moving without pushing employees toward personal file-sharing accounts.

The right choice depends on how your team works, the data you handle, and the systems already in place. A firm standardized on Microsoft 365 has different needs than a law office exchanging sensitive files with external clients or a manufacturer sending large design packages to vendors. Security is not a feature you bolt on after deployment. It is the operating model around identity, permissions, retention, monitoring, and user behavior.

What Makes a File Sharing Platform Secure?

Encryption in transit and at rest is the baseline, not the finish line. A platform should support strong identity controls, including multi-factor authentication, single sign-on where appropriate, and the ability to require access from managed devices. Administrators should be able to see who accessed a file, when they accessed it, and what actions they took.

For many small and mid-sized businesses, the most useful controls are practical ones: expiring links, password-protected sharing, download restrictions, external-sharing policies, version history, and the ability to revoke access immediately. Data loss prevention, sensitivity labels, legal holds, and detailed audit logging become more important in regulated environments.

The platform also needs to fit your people. If sharing secure files takes too many steps, employees will find a shortcut. The goal is controlled collaboration that is easy enough to become the approved way work gets done.

10 Best Secure File Sharing Platforms for SMBs

1. Microsoft OneDrive and SharePoint

Microsoft OneDrive and SharePoint are often the strongest starting point for organizations already using Microsoft 365. OneDrive works well for individual work files, while SharePoint provides shared document libraries, team sites, structured permissions, version control, and collaboration around business content.

Their advantage is integration. Teams can co-author documents, share through Outlook and Teams, apply sensitivity labels, and manage identities through Microsoft Entra ID. With the right licensing and configuration, organizations can use conditional access, data loss prevention, retention policies, and audit capabilities. The trade-off is administrative complexity. Poorly designed SharePoint permissions and unrestricted external sharing can create the exposure these tools are meant to prevent.

2. Google Drive

Google Drive is a practical choice for organizations built around Google Workspace. Its real-time collaboration is intuitive, and staff adoption is often fast. Administrators can manage sharing settings, prevent external sharing by default, use two-step verification, and apply data governance controls based on their Workspace edition.

Google Drive can be especially effective for professional services teams that need quick, browser-based collaboration. However, businesses with complex folder permissions, formal document retention requirements, or Microsoft-heavy workflows may find Microsoft 365 a better operational fit. As with any cloud platform, consumer Google accounts should never become an unofficial extension of the corporate environment.

3. Box

Box is designed for content management and external collaboration with a strong business and compliance focus. It offers granular access controls, workflow features, audit reporting, retention tools, and integrations with common business applications.

Box is a strong contender for legal, healthcare, financial, and enterprise-adjacent organizations that share documents frequently with clients, partners, and vendors. It can provide a cleaner external-sharing experience than a general-purpose file drive. The consideration is cost and overlap: if your Microsoft 365 or Google Workspace environment already meets your needs, adding Box may introduce another system to secure and support.

4. Dropbox Business

Dropbox Business remains popular because it is familiar, simple, and reliable for syncing files across devices. It supports team folders, file recovery, sharing controls, device management options, and administrative reporting. Its external collaboration experience is particularly straightforward for businesses sending large files to customers or contractors.

Dropbox can be a good fit for creative, architecture, engineering, and field-based teams. Still, convenience should not lead the security conversation. Organizations need clear policies for approved folders, external links, offboarding, and personal Dropbox accounts. It is best used as a governed business service, not an open-ended storage location.

5. Egnyte

Egnyte combines cloud file sharing with governance and content intelligence features. It is well suited to organizations that manage large volumes of files across office, remote, and sometimes on-premises environments. It can support detailed permissions, auditing, ransomware detection capabilities, and policy-driven data governance.

For construction, engineering, architecture, and manufacturing organizations, Egnyte can address challenges that simpler collaboration platforms do not always handle well. It may be more capability than a small office needs, but it is worth evaluating when file size, distributed teams, project folders, and compliance oversight are central concerns.

6. Citrix ShareFile

Citrix ShareFile is built around secure client file exchange and document workflows. It is frequently considered by accounting firms, legal practices, and financial services organizations that need branded client portals, secure requests for documents, and controlled delivery of sensitive information.

ShareFile is especially useful when the primary issue is not internal collaboration but secure exchange with people outside the organization. A client can upload tax documents or receive a sensitive report without relying on unsecured email attachments. Its best value appears when the portal becomes part of a defined client-service process rather than another disconnected repository.

7. Tresorit

Tresorit emphasizes end-to-end encryption and privacy-focused file sharing. It offers encrypted storage spaces, controlled sharing links, access permissions, and audit features designed for teams with heightened confidentiality needs.

This platform deserves consideration for legal, healthcare, consulting, and executive teams handling highly sensitive information. The trade-off is that privacy-forward tools may not offer the same broad workflow ecosystem or familiarity as Microsoft 365 and Google Workspace. Evaluate how well it fits existing identity management, productivity applications, and support processes before making it the organization-wide standard.

8. Sync.com for Teams

Sync.com for Teams is another privacy-oriented option that emphasizes encrypted file storage and sharing. It provides team folders, access controls, password-protected links, expiry dates, and administrative oversight in a comparatively simple interface.

It can work well for smaller organizations that prioritize confidentiality and need a straightforward platform without extensive enterprise collaboration features. Businesses should confirm that the platform’s integrations, reporting, and compliance documentation align with their specific obligations before relying on it for regulated workflows.

9. Kiteworks

Kiteworks focuses on secure content communications, including file sharing, managed file transfer, secure email, and governance. It is intended for organizations that need to control and document sensitive data exchanges across employees, clients, vendors, and automated processes.

Kiteworks can be a strong match for businesses with strict compliance requirements or high-volume external data exchange. It is generally a more specialized, process-driven solution than a basic cloud drive. That capability can be valuable, but it requires thoughtful planning and ownership to avoid an overly complicated rollout.

10. FileCloud

FileCloud offers secure file sharing with deployment flexibility, including cloud and self-hosted options. It supports file sync, external sharing, granular permissions, audit trails, and policy controls. For organizations with data residency, customization, or infrastructure requirements, that flexibility can be a meaningful advantage.

A self-hosted approach can offer more direct control, but it also creates more responsibility. Your organization must maintain the underlying infrastructure, patching, backups, monitoring, and access controls. For many SMBs, a properly configured cloud service is the safer operational choice unless there is a clear business or compliance reason to manage the platform directly.

How to Choose the Right Platform

Start with the data, not the product list. Identify the information your employees share, who receives it, where those people work, and whether they use managed devices. Then determine which controls are mandatory. A healthcare practice may need auditability and business associate agreement support. A law firm may prioritize client portals, permissions, and retention. A growing professional services company may get the strongest return from securing and optimizing the Microsoft 365 tools it already pays for.

Next, examine external sharing. Many security incidents begin with a link that was never meant to be public, a former employee whose account was not disabled, or a vendor who retained access long after a project ended. Require expiration dates for external links, limit anonymous sharing, review guest access regularly, and make offboarding part of the security process.

Finally, account for operations. The best platform is one your team can support consistently. It needs documented ownership, baseline configuration standards, monitoring, backup coverage, user training, and periodic permission reviews. Sigma Networks helps businesses treat these controls as part of a broader security and continuity strategy, not as isolated settings inside a file-sharing application.

File Sharing Security Is a Management Discipline

No platform can compensate for shared passwords, unmanaged devices, excessive permissions, or a lack of visibility into where sensitive documents travel. A secure file-sharing decision should improve the way your organization governs information, responds to access requests, and protects client trust.

Choose the platform that matches your existing productivity environment and risk profile, then give it the same attention you would give any other business-critical system. Review access before a problem forces the issue, test what employees can actually share externally, and make the secure path the easiest path for your team.

Cybersecurity Automation That Reduces Risk

Cybersecurity Automation That Reduces Risk

A suspicious Microsoft 365 login at 2:13 a.m. should not wait until someone opens a ticket the next morning. By then, a stolen credential may have been used to create inbox rules, access financial data, or send convincing fraud emails from a trusted account. Cybersecurity automation gives small and mid-sized businesses a faster, more disciplined way to respond when every minute matters.

For business leaders, the value is not simply faster technology. It is a security operation that can identify routine warning signs, take approved protective actions, and document what happened without relying on a single person to see every alert. That reduces exposure, supports compliance, and helps internal teams focus on decisions that require judgment.

What Cybersecurity Automation Actually Does

Cybersecurity automation uses defined rules, integrations, and workflows to perform repeatable security tasks. It connects security tools so that an event detected in one system can trigger investigation, containment, notification, or documentation in another.

For example, an identity platform may flag an impossible-travel login, where an employee account appears to sign in from Texas and another country within an unrealistic timeframe. An automated workflow can enrich that alert with the user’s recent activity, check whether multi-factor authentication was completed, identify the device involved, and temporarily restrict access if the risk meets a defined threshold.

The goal is not to let software make every security decision. The goal is to remove delay and inconsistency from high-volume, well-understood tasks. A security analyst or IT leader can then review the context, confirm the right response, and investigate incidents that require deeper expertise.

Automation is not “set it and forget it” security

Automation can act quickly, but it only works as well as the policies, configurations, and monitoring behind it. A poorly designed rule can block a legitimate employee, overlook an exception, or generate so many notifications that the team starts ignoring them.

That is why an effective program starts with clear security baselines, documented response procedures, tested backups, identity controls, and ownership. Automation reinforces disciplined operations. It does not replace them.

Where Automation Creates the Most Business Value

Small and mid-sized organizations often have the same threat exposure as larger enterprises but fewer dedicated security resources. Phishing, account compromise, ransomware, vendor fraud, and unpatched systems do not wait for a business to build a large internal security team.

Automation helps close that gap in practical ways. It can prioritize alerts based on risk rather than volume, reducing the chance that a meaningful warning gets buried in routine noise. It can also respond around the clock, even when an internal IT manager is off duty or focused on a critical business project.

The greatest value usually appears in several repeatable areas:

  • Identity protection: Detecting unusual sign-ins, risky account changes, disabled multi-factor authentication, and privileged access activity.
  • Endpoint response: Isolating a workstation that shows signs of ransomware, malicious code execution, or unauthorized tools.
  • Email security: Quarantining suspicious messages, removing known malicious emails from mailboxes, and flagging likely business email compromise attempts.
  • Vulnerability management: Identifying missing patches, escalating critical findings, and verifying that remediation has occurred.
  • Compliance evidence: Recording alerts, approvals, response actions, and system changes that support audits and incident reviews.

Consider a common scenario: a user enters credentials on a phishing page. Without coordinated controls, the attacker may sign in, create forwarding rules, search for payment information, and impersonate the employee. With the right workflows in place, suspicious login behavior can trigger password reset requirements, session revocation, mailbox-rule inspection, endpoint review, and a notification to the appropriate people. The business moves from a scattered reaction to a coordinated response.

Faster Response Matters More Than More Alerts

Security tools can produce thousands of events. Most are not emergencies, but a small percentage may signal an active threat. The operational challenge is separating normal activity from behavior that deserves immediate attention.

Cybersecurity automation improves this process by collecting context before a person reviews the event. Instead of receiving a bare alert that says “suspicious login,” the analyst can see the user, location, device status, recent account changes, related email activity, and previous security events. That context shortens investigation time and supports better decisions.

This is especially valuable for organizations with lean IT teams. An office manager, controller, or internal IT generalist should not have to become a full-time security analyst just to understand whether an alert is serious. Well-designed workflows route the right information to the right resource with clear next steps.

The Trade-Off: Speed Must Be Matched With Control

Not every alert should automatically result in a locked account or isolated computer. A traveling executive may trigger an unusual-login rule. An engineering application may behave differently than standard office software. A manufacturing device may require special handling because taking it offline could interrupt operations.

The right level of automation depends on the organization’s risk tolerance, technology environment, and business requirements. High-confidence indicators, such as confirmed malware activity or sign-in attempts from known malicious infrastructure, may justify immediate containment. Lower-confidence events may be better suited for enrichment, ticket creation, and analyst review.

This distinction matters. Overly aggressive automation can create business disruption. Underused automation can leave the organization exposed while teams manually sort through preventable work. The strongest approach uses graduated response actions based on severity, confidence, and potential operational impact.

Build approval paths for sensitive actions

Some actions should require human approval, particularly those that affect executive accounts, production systems, financial workflows, or client-facing services. Others can be automated with appropriate safeguards, such as disabling a compromised standard user account or opening a high-priority incident ticket.

Documenting these decisions helps establish accountability. It also ensures that security response does not depend on tribal knowledge held by one employee or vendor contact.

How to Implement Cybersecurity Automation Responsibly

A practical rollout begins with visibility. An organization needs an accurate picture of its users, endpoints, cloud applications, privileged accounts, data locations, and critical business systems. If asset inventories are incomplete or logging is inconsistent, automation will make decisions with incomplete information.

Next, identify the recurring tasks that consume time and follow predictable patterns. Password-related account risk, suspicious inbox rules, malware detections, missing critical patches, and inactive accounts are common starting points. Focus first on workflows with a clear trigger, a known response, and measurable business impact.

Then establish ownership. Someone must review automated outcomes, tune rules, approve exceptions, and investigate incidents that exceed the workflow’s limits. For many small and mid-sized businesses, this is where a managed security operations partner can add meaningful value. The partner provides continuous monitoring and trained analysts while the internal team retains business context and approval authority.

Testing is essential. Run workflows in observation mode before allowing automatic containment. Review false positives, confirm that notifications reach the right people, and verify that response actions do not create unintended downtime. Security automation should be treated like any other important operational control: configured carefully, monitored continuously, and adjusted as the environment changes.

What Leaders Should Ask Before Investing

Business leaders do not need to evaluate every technical feature. They do need clear answers about outcomes and accountability. Ask whether the proposed solution will reduce response time, improve visibility across email, endpoints, identities, and cloud systems, and create usable documentation for compliance or insurance requirements.

Also ask who watches the system after hours, who has authority to contain an active threat, and how the provider will communicate during an incident. A dashboard alone is not a security operation. The real measure is whether the business can detect, decide, and respond before a manageable event becomes material downtime or data loss.

For regulated organizations in healthcare, legal services, financial services, and professional consulting, automation can also strengthen consistency. Required reviews, access controls, remediation records, and incident documentation are easier to maintain when essential actions are built into the operating process rather than left to memory.

Security That Supports Growth

As a business grows, its attack surface grows with it. More employees, devices, cloud services, remote access, vendors, and data create more opportunities for mistakes and misuse. Adding headcount alone is rarely the most efficient answer.

Cybersecurity automation gives growing organizations a way to scale disciplined security operations without accepting slower response times or relying on manual effort for every routine event. It supports stronger oversight while preserving human judgment where it matters most.

The right question is not whether every security task can be automated. It is whether your business has a defined, accountable response when the next high-risk alert arrives after hours. Building that response now protects more than systems. It protects customer trust, business continuity, and the confidence to grow.

Microsoft Azure Cost Optimization for SMBs

Microsoft Azure Cost Optimization for SMBs

A cloud invoice should not be a monthly surprise. Yet many small and mid-sized businesses find that Azure spending grows faster than the workloads it supports. Microsoft Azure cost optimization gives leaders a disciplined way to control that growth without weakening security, slowing teams down, or creating new operational risk.

For a growing organization, the objective is not simply to make the Azure bill smaller. The objective is to pay for the right capacity, at the right time, with clear ownership and controls that support business priorities. That distinction matters. A poorly planned cost-cutting effort can remove redundancy, delay critical updates, or leave an application unable to handle a busy period.

Why Azure costs become difficult to control

Azure is designed to scale quickly, which is valuable when a business needs to launch a new application, support remote work, or recover from an outage. The same flexibility can create waste when resources are deployed without standards for sizing, tagging, ownership, and retirement.

A development server may run all night and through the weekend. A virtual machine selected for a short-term performance issue may remain oversized for a year. Old snapshots, unattached disks, dormant public IP addresses, and duplicate storage accounts can continue generating charges long after their original purpose is forgotten. None of these are unusual mistakes. They are signs that cloud governance has not kept pace with cloud adoption.

For regulated organizations, the stakes are higher. Healthcare providers, law firms, financial services firms, and manufacturers cannot treat every cost reduction as harmless. Retention requirements, recovery objectives, encryption, logging, and access controls may be necessary operating costs. The right question is not, “Can we eliminate this expense?” It is, “Does this expense protect a documented business, security, or compliance need?”

Start Microsoft Azure cost optimization with visibility

Cost optimization begins with accurate visibility. Before resizing resources or committing to long-term pricing, establish who owns each workload and why it exists. A monthly invoice alone rarely provides enough context to make sound decisions.

Create a consistent tagging structure for business unit, application, environment, owner, cost center, and data classification. Tags should be required during provisioning rather than added later as a cleanup project. When a controller can see which department owns a workload and an IT leader can see whether it is production, testing, or disaster recovery, cost conversations become factual instead of speculative.

Budgets and alerts should be set at more than one level. A total subscription budget protects against major surprises, while resource group and department budgets identify where spending is changing. Alerts are most effective when they trigger an assigned response. An alert sent to an unattended shared mailbox does not create accountability.

It also helps to establish a regular review cadence. A brief monthly review may be enough for stable environments. Businesses with active development, acquisitions, seasonal demand, or major modernization projects may need weekly reporting during periods of change. The review should compare spending against workload activity, planned initiatives, and prior forecasts.

Look for the gap between provisioned and used

The fastest savings opportunities often come from resources that are running but lightly used. Review virtual machine CPU, memory, disk throughput, and network activity over a meaningful period, not a single quiet day. A server used heavily for month-end processing may need its current capacity even if it appears idle most of the month.

Right-sizing means selecting a service tier that reflects actual demand and required headroom. It does not mean shrinking every resource to its lowest possible level. Production systems need room for growth, maintenance events, and unexpected demand. The best decision balances performance, resilience, and cost.

Nonproduction workloads deserve separate attention. Development, test, training, and proof-of-concept environments often have predictable schedules. Automating shutdown outside business hours can reduce unnecessary run time significantly, provided teams have a clear way to restart approved resources when needed.

Match pricing commitments to stable workloads

Azure offers pricing options that reward predictable usage, including reservations and savings plans. These can reduce compute costs, but they are commitments, not automatic savings. They are most appropriate for workloads with stable, well-understood demand, such as a core line-of-business server or a database that has run consistently for months.

Do not apply long-term commitments to a workload that may be retired, migrated, or substantially redesigned soon. A company preparing to replace a legacy application with software as a service, for example, should first confirm the migration timeline. Otherwise, it may exchange variable costs for unused committed capacity.

A practical approach is to separate workloads into three groups: stable production services, variable production services, and temporary or experimental workloads. Stable services are candidates for commitments after utilization is validated. Variable workloads may benefit more from autoscaling or flexible pricing. Temporary systems should have an expiration date and an owner responsible for removal.

Storage requires the same level of discipline. The least expensive storage tier is not always the appropriate tier when recovery time, regulatory retention, or user access requirements are considered. Classify data by how often it is accessed, how quickly it must be restored, and how long it must be retained. Then apply lifecycle policies that move eligible data to lower-cost tiers without violating recovery or compliance obligations.

Build guardrails before cloud waste returns

One-time cleanup creates a temporary improvement. Governance prevents the same expenses from returning. Azure policies, role-based access, standardized deployment templates, and approval workflows give organizations a way to control spend without turning IT into a bottleneck.

For example, a policy can restrict high-cost resource types, require approved regions, or prevent public exposure where it is not justified. Role-based access can ensure that users who need to manage applications do not also have unrestricted authority to create costly infrastructure. Standard templates can deploy approved configurations with required tags, security settings, backup requirements, and monitoring already in place.

These controls support cybersecurity as well as financial discipline. An unapproved resource can create both an unexpected bill and an unmanaged attack surface. Consistent provisioning makes it easier to verify encryption, identity controls, logging, vulnerability management, and backup coverage. Cost governance and security governance should be managed together because both depend on knowing what exists and who is responsible for it.

Keep disaster recovery separate from waste

Backup and disaster recovery costs are frequent targets for budget pressure, especially when no incident has occurred recently. That is understandable, but it requires careful analysis. Reducing backup retention, removing geographic redundancy, or eliminating recovery infrastructure may lower monthly spend while increasing the financial impact of ransomware, data corruption, or a regional outage.

Start with documented recovery point and recovery time objectives. Then verify that the protection design meets those objectives at a cost the business understands. Older backups, duplicate copies with no retention requirement, and recovery resources for retired applications may be candidates for reduction. Protection for critical systems should be treated as a risk decision approved by business leadership, not as incidental cloud waste.

Assign ownership beyond the IT team

Cloud financial management works best when finance, operations, security, and IT share responsibility. Finance brings budget discipline and forecasting. Operations identifies revenue-generating processes and seasonal demand. Security and compliance teams define necessary controls. IT translates those needs into architecture and operating standards.

A useful monthly discussion asks a few direct questions: What changed in spend? Which changes were planned? Which resources have no identified owner? What commitments are approaching renewal? Are new projects using approved architectures? These questions are straightforward, but they expose the drift that produces avoidable cloud costs.

For organizations without a dedicated cloud operations team, a managed services partner can provide the ongoing review that internal staff may struggle to sustain. Sigma Networks helps businesses connect cloud oversight to security monitoring, backup planning, compliance requirements, and executive technology strategy rather than treating Azure as a standalone invoice.

Measure progress in business terms

Savings are meaningful, but cost optimization should also improve predictability. Track the percentage of resources with complete ownership tags, the number of idle assets removed, budget variance by department, commitment utilization, and the cost of critical applications over time. Pair these measures with operational indicators such as uptime, recovery readiness, and security coverage.

This balanced view prevents false wins. If monthly spend falls because a team disabled monitoring or shortened backup retention below policy requirements, the organization has not become more efficient. It has shifted risk into a less visible category.

A well-managed Azure environment gives executives a clearer answer to a basic question: what are we paying for, and does it support the business? Begin with ownership and visibility, make measured changes, and keep protection requirements in the decision process. That is how cloud spending becomes a planned investment instead of a recurring source of uncertainty.

How to Implement Zero Trust in Your Business

How to Implement Zero Trust in Your Business

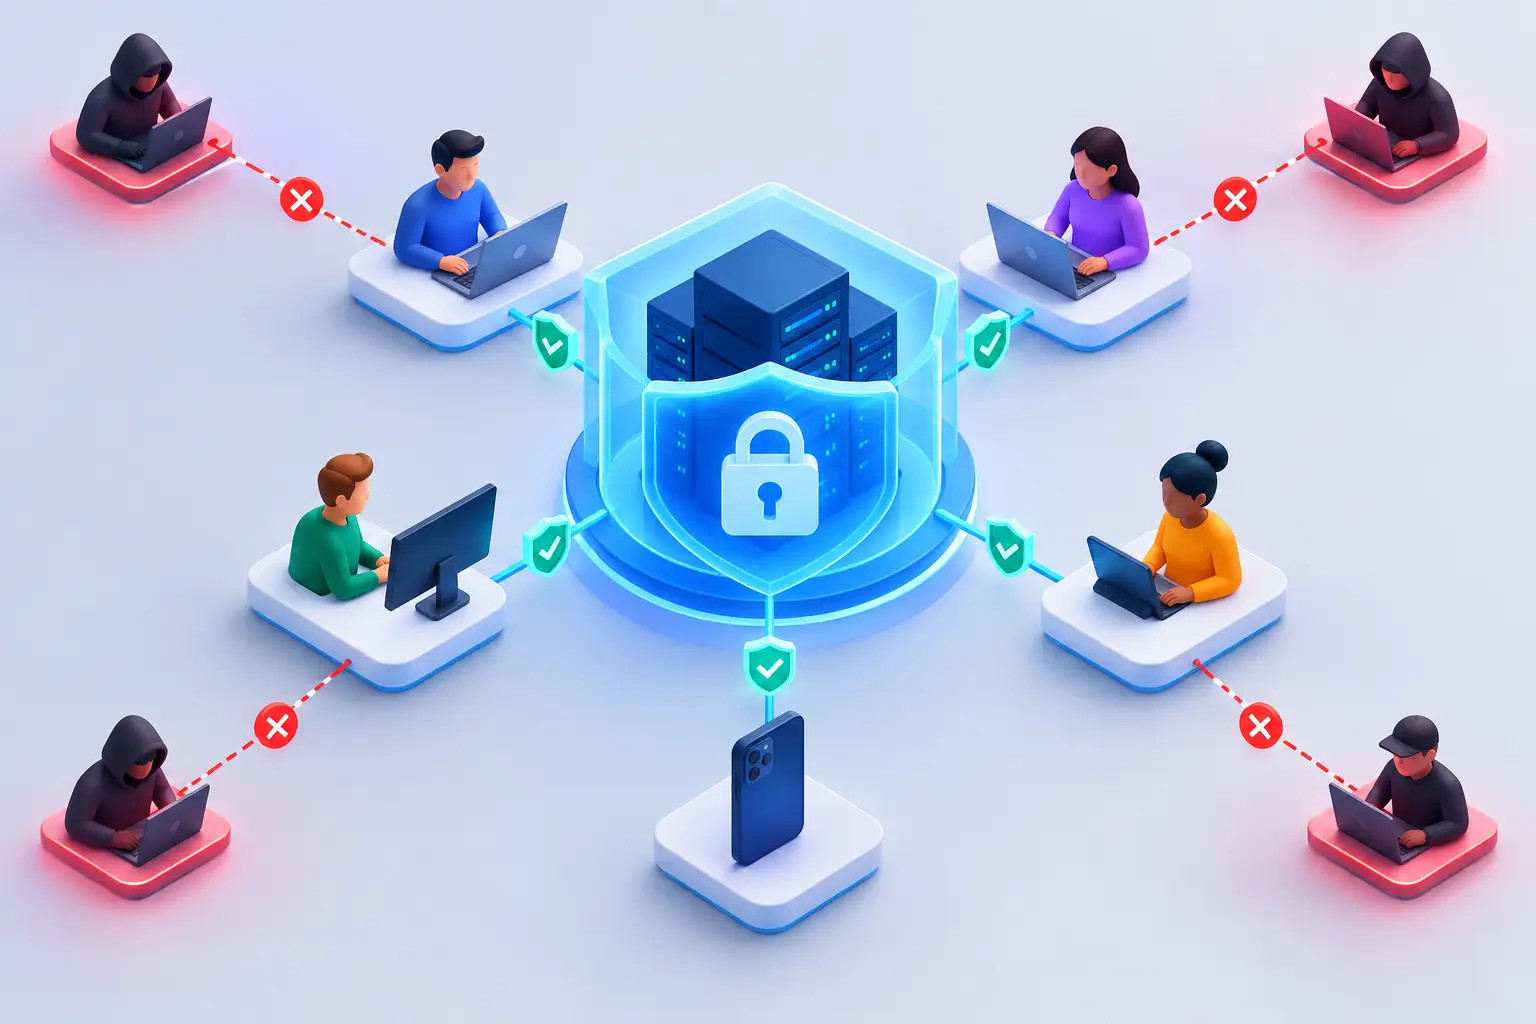
A compromised Microsoft 365 account can give an attacker a foothold in minutes. If that user can access every shared drive, application, and administrative system from any device, one stolen password can become a business-wide incident. Learning how to implement zero trust changes that equation by requiring every user, device, and connection to prove it belongs before access is granted.

Zero trust is not a single product or a switch your IT team can flip. It is an operating model for reducing risk while keeping employees productive. For small and mid-sized businesses, the goal is practical: limit unnecessary access, validate identities continuously, protect the devices that handle business data, and detect abnormal activity before it turns into downtime, fraud, or a compliance problem.

What zero trust means for a growing business

The traditional network model assumed that someone connecting from the office, through a company VPN, or with the right password was trustworthy. That model does not match how most businesses operate now. Employees work remotely, access cloud applications, use mobile devices, and collaborate with outside vendors. The network perimeter is no longer the sole security boundary.

Zero trust replaces broad, assumed access with a simple principle: never trust by default, always verify. A user requesting access is evaluated based on identity, authentication strength, device condition, location, behavior, and the sensitivity of the requested resource.

This does not mean employees must complete a security challenge every time they open a document. A well-designed program applies stronger controls where the business risk is higher. Opening a standard internal document may require routine sign-in, while approving a wire transfer, accessing protected health information, or entering a financial system may require multifactor authentication, a compliant device, and additional verification.

Start with the business risks, not the technology

The fastest way to create a costly zero trust project is to buy tools before defining what must be protected. Begin with a business-focused assessment of systems, data, users, and workflows.

Identify where sensitive information resides. For many organizations, the most critical assets are Microsoft 365 email and files, accounting systems, customer databases, line-of-business applications, intellectual property, and backup administration consoles. Then identify who needs access and why. The accounting team may need access to financial applications, but not to engineering project folders. An outside consultant may need a specific application for a limited period, not a company-wide account.

This exercise often exposes long-standing access issues: former employees with active accounts, generic shared logins, administrators using privileged credentials for daily email, or departments retaining access after a role change. These gaps are common, and they are exactly where zero trust creates immediate value.

For regulated businesses, map the review to existing obligations. Healthcare organizations should consider HIPAA safeguards. Financial firms, legal practices, manufacturers serving government or defense clients, and companies handling payment data may face additional contractual or regulatory requirements. Zero trust supports compliance readiness, but it does not replace a formal compliance program.

Build a reliable identity foundation

Identity is the center of a zero trust strategy. If an attacker can impersonate a trusted user, network controls alone will not protect the business.

Enforce multifactor authentication everywhere it matters

Require multifactor authentication for email, cloud applications, remote access, privileged accounts, and administrative portals. Phishing-resistant methods, such as authenticator apps with number matching, security keys, or passkeys, offer stronger protection than text-message codes when available.

Do not create exceptions casually. Executives, finance personnel, and IT administrators are frequent targets because their accounts can authorize payments, access sensitive records, or change security settings. If a workflow makes multifactor authentication difficult, solve the workflow problem rather than weakening the control.

Apply least-privilege access

Users should receive only the access required for their current responsibilities. Review access when someone joins, changes roles, works with a temporary project team, or leaves the company. This is especially important for shared cloud storage, accounting platforms, customer relationship management systems, and remote management tools.

Administrative access deserves separate treatment. IT staff should use standard accounts for ordinary work and dedicated privileged accounts only when performing administrative tasks. Where possible, provide elevated access just in time rather than permanently. That reduces the damage a compromised credential can cause.

Establish device trust before granting access

A valid password should not be enough to connect an unmanaged, outdated laptop to sensitive company resources. Device posture is a core part of how to implement zero trust effectively.

Enroll company-owned computers and mobile devices in centralized management. At a minimum, the organization should be able to confirm that devices are encrypted, supported by current operating system updates, protected by endpoint security software, and configured with screen locks. Lost devices should be capable of remote lock or wipe when business data is at risk.

For personally owned devices, the right approach depends on the role and the data involved. A bring-your-own-device policy can work for limited email or collaboration access when mobile application management and data protection controls are in place. It may not be appropriate for administrators, employees handling regulated data, or users who need access to sensitive financial and operational systems. Company-managed devices provide more assurance and more consistent support.

Conditional access policies connect these device requirements to actual access decisions. For example, a user may be allowed to access email from an enrolled, encrypted laptop but blocked from downloading company files to an unknown personal device. Start with monitoring or report-only modes where available, then enforce policies after testing business impact.

Segment access so one breach does not spread

Zero trust reduces lateral movement. In plain terms, an attacker who compromises one account or device should not be able to move freely through the rest of the environment.

Network segmentation remains valuable, particularly for organizations with on-premises servers, production equipment, voice systems, or specialized applications. Separate guest wireless networks from business systems. Isolate sensitive systems from general user networks. Limit communication between segments to the specific ports and services required for business operations.

Cloud environments need similar discipline. Use separate administrative roles, restrict access to management portals, and avoid placing sensitive data in broadly shared folders. Secure access service edge and zero trust network access solutions can provide application-level access without exposing an entire network through a traditional VPN. The best choice depends on your applications, workforce, budget, and existing infrastructure.

Add monitoring, detection, and response

Preventive controls reduce the chance of a successful attack, but no environment is risk-free. A zero trust program also needs visibility into what happens after access is granted.

Centralize logs from identity providers, endpoints, firewalls, cloud platforms, and critical applications. Monitor for behavior that deserves investigation, such as impossible travel logins, repeated failed multifactor prompts, a user downloading an unusual volume of files, or an administrator creating new privileged accounts.

For many small and mid-sized businesses, continuous monitoring requires a managed detection and response service or security operations center. Alerts are only useful when someone can validate them, investigate quickly, and take defined containment actions. A 24/7 response capability matters because many attacks begin outside normal business hours.

Your incident response plan should also reflect zero trust controls. Define who can disable a user account, isolate a device, revoke application sessions, contact cyber insurance carriers, and communicate with leadership. Test the plan with realistic scenarios, including a compromised executive email account and a ransomware event.

Roll out zero trust in phases

Trying to enforce every control at once can interrupt business operations and create resistance. A phased rollout protects the organization while allowing employees and system owners to adapt.

A practical sequence is to secure identities first, then managed devices, then conditional access and privileged access, followed by network and application segmentation. Start with the accounts and systems that present the greatest business impact, including executives, finance, administrators, and high-value cloud applications.

Measure progress with outcomes leaders can understand: percentage of users protected by multifactor authentication, number of unmanaged devices accessing company data, dormant accounts removed, privileged accounts reviewed, and time required to contain a suspected compromise. These metrics connect security investment to reduced operational and financial risk.

Employee communication is part of the deployment. Explain what is changing, when it will happen, and where employees can get help. Security controls that are poorly communicated often become workarounds. Controls that are supported, documented, and aligned to real work are far more likely to last.

Make zero trust an operating discipline

Zero trust is not a project with a finish date. Employees change roles, applications are added, vendors require access, and attackers change tactics. Review access rights, device compliance, conditional access policies, and security alerts on a recurring schedule.

The most effective approach balances protection with business reality. A 15-person professional services firm will not deploy zero trust exactly like a multi-site manufacturer, but both can apply the same principles of verified identity, controlled access, secure devices, and continuous monitoring. The next useful step is not to chase every security feature. It is to identify the access decision that creates the greatest risk for your business and put a stronger control around it.

Best HIPAA Compliant Email Solutions for SMBs

Best HIPAA Compliant Email Solutions for SMBs

A missed encryption setting, an unapproved mobile app, or an employee forwarding a message to personal email can turn a routine patient communication into a reportable incident. For healthcare practices and healthcare-adjacent businesses, choosing among the best HIPAA compliant email solutions is not simply a software decision. It is a decision about how reliably the organization protects protected health information, documents its controls, and keeps daily work moving.

The right platform depends on your existing environment, the volume and sensitivity of patient communication, and who will manage the configuration. A small clinic using Microsoft 365 has different needs than a billing company exchanging high volumes of records or a multi-site provider organization with an internal IT team. The common requirement is accountability: email security must be configured, monitored, and supported as an operational control, not treated as a one-time purchase.

What Makes an Email Solution HIPAA Ready?

No vendor can make an organization HIPAA compliant by itself. HIPAA compliance includes administrative, physical, and technical safeguards, along with policies, training, risk analysis, and incident response. An email provider can support those requirements, but the covered entity or business associate remains responsible for using the service correctly.

At a minimum, evaluate whether a provider will sign a business associate agreement, commonly called a BAA. Without a BAA, a service should not be used to create, receive, maintain, or transmit protected health information on behalf of a covered entity.

The platform also needs appropriate safeguards. Encryption in transit and at rest matters, but it is only part of the picture. Organizations should look for access controls, multi-factor authentication, audit logging, secure message delivery options, data retention controls, and administrative visibility. For many small and mid-sized organizations, protection against phishing, account takeover, and accidental misdelivery is just as important as message encryption.

A practical solution should not force staff to abandon normal workflows for every sensitive message. If the secure process is too difficult, users will find workarounds. That creates the exact risk the technology was intended to reduce.

Best HIPAA Compliant Email Solutions by Use Case

The strongest option is usually the one that fits the organization’s workflow and can be governed consistently. Here are several common approaches and where they tend to fit.

| Solution approach | Best fit | Key strengths | Watch-outs | | — | — | — | — | | Microsoft 365 with HIPAA-focused configuration | Organizations already using Outlook and Teams | Familiar tools, centralized identity, strong security options | Requires careful licensing, configuration, monitoring, and a BAA | | Google Workspace with HIPAA-focused configuration | Teams built around Gmail and Google collaboration | Simple collaboration and browser-based administration | Secure use depends on configuration and supported services under the BAA | | Paubox | Practices that want secure outbound email with minimal recipient friction | Encrypted delivery experience designed for healthcare workflows | May not replace broader email security and collaboration controls | | Virtru | Teams that need message-level encryption and granular control | Persistent protection, secure sharing, policy controls | Users and administrators need clear processes for adoption | | LuxSci | Organizations with specialized healthcare messaging or high-volume needs | Healthcare-focused secure email, forms, and delivery options | More specialized setup may require technical planning |

Microsoft 365 for organizations that need broad control

Microsoft 365 is often the most practical foundation for growing healthcare organizations because it combines email, identity, collaboration, device controls, and security tooling in one environment. With the right licensing and configuration, organizations can apply multi-factor authentication, conditional access, data loss prevention policies, retention rules, audit logging, mobile device controls, and secure email workflows.

Its trade-off is complexity. Microsoft 365 is not automatically safe for PHI because it has been purchased with a business subscription. A secure implementation requires a signed BAA, confirmation that the intended services are covered, appropriate security settings, and ongoing review. It also requires someone to own alerts, user access, policy changes, and incident response.

For an established practice, provider group, or professional services firm supporting healthcare clients, this approach can reduce tool sprawl. It is especially valuable when email security needs to align with broader cybersecurity and business continuity planning.

Google Workspace for collaboration-first teams

Google Workspace can be a strong fit for smaller teams that rely on Gmail, Google Drive, and shared documents. It offers centralized account management, multi-factor authentication, audit capabilities, and controls that can support a HIPAA-aligned environment when configured correctly and used under an appropriate BAA.

The decision point is governance. Teams should define which apps and sharing methods may be used for PHI, how external sharing is controlled, and how employee access is removed when roles change. A common problem is assuming that a secure email inbox solves the risks created by uncontrolled attachments, shared links, or unmanaged devices.

Paubox for straightforward secure patient email

Paubox is built around a simple goal: help healthcare organizations send encrypted email without forcing recipients through a difficult portal experience. That can be valuable for appointment details, follow-up instructions, billing questions, and other patient communications where ease of use affects response rates.

It is a compelling choice when a practice wants a specialized healthcare email tool and does not need it to serve as its entire productivity platform. However, Paubox should be assessed as part of the larger security stack. Identity security, endpoint protection, backups, employee training, and phishing defense still need clear ownership.

Virtru for controlled sharing beyond the inbox

Virtru is well suited to organizations that need more granular control over sensitive messages and files. Its encryption and access controls can help teams protect information after it leaves the inbox, including the ability to manage recipient access in certain workflows.

This model is useful when a business shares PHI with external partners, consultants, payers, or distributed teams. It can add meaningful control, but only if employees understand when and how to apply it. Organizations should test the user experience with both internal staff and outside recipients before a full rollout.

LuxSci for specialized healthcare communications

LuxSci is a healthcare-oriented option for organizations with specialized messaging requirements, including secure email, secure forms, and high-volume communication needs. It can fit organizations that need more than standard employee email, such as patient outreach workflows or secure operational communications.

The trade-off is that specialized capabilities often require more deliberate implementation. That is not a drawback when the use case demands it, but it does make planning, testing, and documentation essential.

How to Choose the Right Platform

Start with the communication paths that actually carry PHI. This includes patient emails, referrals, billing messages, shared documents, scanned records, mobile access, and any third-party systems that relay messages. A platform that protects only outbound email may leave other common workflows exposed.

Next, confirm who owns administration. A solution with powerful security controls is valuable only when policies are maintained, access is reviewed, logs are available, and suspicious activity receives attention. Small organizations often underestimate the operational work behind compliance-ready email. Shared administrator accounts, inactive former employee mailboxes, and inconsistent multi-factor authentication are frequent weaknesses.

Then evaluate the vendor relationship. Request the BAA, understand what services it covers, and document the configuration requirements. Ask how the provider handles security incidents, audit data, backups, retention, support access, and service changes. If a vendor cannot clearly explain these items, it may not be the right fit for sensitive communication.

Finally, design for people. Train users on when PHI may be sent, how to verify recipients, how to recognize phishing messages, and what to do after a suspected misdirected email. Technology reduces risk, but a clear process helps prevent a routine mistake from becoming a compliance event.

Email Compliance Needs Ongoing Oversight

Email platforms change, employees change roles, and attackers constantly adjust their tactics. A compliant implementation from two years ago may no longer reflect current licenses, user behavior, mobile access, or security settings. Periodic risk assessments and configuration reviews are necessary to keep controls aligned with the business.

For healthcare organizations in DFW and beyond, Sigma Networks helps turn email security from a loosely managed tool into a documented, monitored part of the IT environment. That includes Microsoft 365 security, identity protection, user access governance, incident readiness, and the strategic planning needed to support growth.

The best choice is rarely the product with the longest feature list. It is the solution your organization can secure, administer, document, and use consistently when patient information is on the line.

How to Create a Backup Policy That Works

How to Create a Backup Policy That Works

A backup is only useful when it restores the right data, within the time your business can afford to be down. That is why learning how to create backup policy standards is more than an IT exercise. It is a business continuity decision that affects revenue, client trust, compliance, and your ability to recover from ransomware or a simple human error.

For a small or mid-sized business, the policy should give leadership clear answers: What are we protecting? How quickly must it return? Who owns the process? And how do we know the backups will work when the pressure is real?

Start With Business Risk, Not Storage Capacity

A backup policy should not begin with a storage quote or a retention setting. Begin by identifying the systems that keep the company operating. For a law firm, that may include case management files, email, and document repositories. For a manufacturer, it may be production systems, engineering drawings, and line-of-business applications. For a healthcare organization, patient records and scheduling platforms may be the priority.

Classify data based on the impact of its loss or unavailability. Financial records, client data, intellectual property, Microsoft 365 data, configuration files, and core application databases usually belong in the highest protection tier. Shared files that can be recreated may have a different recovery expectation.

This exercise also exposes a common problem: many organizations back up servers but overlook cloud data, employee endpoints, network configurations, or specialized software. A policy must account for where business information actually lives, not just what sits in the server room.

Define Recovery Objectives Leadership Can Approve

Two measurements make a backup policy practical: recovery time objective and recovery point objective.

The recovery time objective, or RTO, is the longest acceptable amount of downtime. If a critical accounting system must be available by the next business morning, its RTO may be 12 hours. If a production application supports active operations, the acceptable window may be much shorter.

The recovery point objective, or RPO, defines how much data the business can afford to lose. An RPO of four hours means the organization could lose up to four hours of work after an incident. A database that changes continuously may require frequent backups or replication, while archived records may only need daily protection.

These targets have cost implications. Faster recovery and tighter data-loss limits generally require more frequent backups, higher-performance recovery infrastructure, and more hands-on management. Not every system needs the same level of protection. The policy should prioritize spending where downtime creates the most damage.

How to Create a Backup Policy With Clear Scope

Write the policy in plain language that business leaders, IT staff, and compliance stakeholders can follow. Technical procedures can sit in separate runbooks, but the policy should establish the rules and responsibilities.

At a minimum, define which systems and data sources are included, how often backups run, where copies are stored, how long records are retained, and who reviews success or failure alerts. Include cloud platforms such as Microsoft 365, SaaS applications with valuable records, virtual servers, on-premises systems, laptops, and network device configurations where appropriate.

Retention periods should reflect business and regulatory needs. A short retention window may be enough for routine operational recovery, while financial, legal, healthcare, or contractual requirements may demand longer preservation. Retaining every version forever is not automatically safer. It raises storage costs, complicates management, and may create legal obligations. Set retention tiers intentionally, then revisit them when regulations or business requirements change.

The policy should also identify exclusions. If a department stores data in an unsupported application or a personal cloud account, document that risk instead of allowing assumptions to persist.

Use the 3-2-1-1-0 Approach

A useful framework for modern backup planning is 3-2-1-1-0. Maintain at least three copies of important data, on two different types of storage, with one copy kept offsite. Add one immutable or offline copy and aim for zero unverified backup errors.

The extra immutable copy matters because ransomware often targets backup repositories before it encrypts production data. Immutability prevents backups from being altered or deleted for a defined retention period. An offline copy provides another layer of protection when credentials, networks, or cloud environments are compromised.

This does not mean every file needs five expensive copies. Apply the framework according to the data tier and risk profile. Critical systems should receive the strongest protection. Lower-risk data may have a more cost-conscious design, provided the business accepts the recovery trade-off.

Secure the Backup Environment

Backups are a high-value target, so the policy must include security controls. Use separate administrative accounts for backup systems, require multifactor authentication, and limit access to the people who need it. Backup credentials should not be shared broadly or tied to a single employee’s personal account.

Encrypt backup data in transit and at rest. Protect encryption keys, recovery codes, and administrator credentials with the same discipline applied to other sensitive business assets. Logging should show who changed retention settings, deleted a backup job, initiated a restore, or modified access rights.

Segmentation also matters. If the backup environment is fully exposed to the same network and credentials as everyday operations, an attacker may be able to compromise both. Separation does not eliminate risk, but it gives the business a better recovery path when a security incident spreads.

Assign Ownership and Build a Response Process

A backup policy without ownership becomes a collection of settings that nobody reviews. Name the accountable role for backup oversight, alert response, policy approval, and annual review. In a co-managed IT environment, clarify what the internal team owns and what the managed service provider owns.

Define what happens when a backup fails. The response process should specify who receives alerts, how quickly failures are investigated, when leaders are notified, and how exceptions are documented. A failed backup for a noncritical workstation is not the same as a failed backup for a core database, so escalation should match the business impact.

The policy should also state who can authorize a restore during a cyber incident. Restoring too early can reintroduce malware or overwrite evidence needed for investigation. Security and recovery teams need a coordinated decision process, especially when ransomware or potential data exposure is involved.

Test Restores, Not Just Backup Jobs

A green dashboard confirms that a job completed. It does not prove that data is recoverable, applications will function, or recovery will meet the stated RTO. Restore testing is the difference between having backups and having a recovery capability.

Test a range of scenarios: individual files, mailbox recovery, server restoration, critical application data, and a broader disaster recovery event. Document the time required, the steps that caused delays, and any dependencies discovered during the test. A restored server may still be unusable if its DNS settings, application licenses, firewall rules, or database connections are missing.

For regulated organizations, testing records can also support compliance readiness. Keep evidence of test dates, results, corrective actions, and approvals. If a test exposes a gap, treat it as a planning opportunity rather than a failure. The point is to improve before an outage forces the issue.

Review the Policy as the Business Changes

A backup policy should be reviewed at least annually and whenever the organization adds a major application, moves workloads to the cloud, acquires another company, changes compliance obligations, or experiences a security event. Growth changes the value of data and the cost of downtime.

The best policy is one that aligns recovery investments with operational reality. It gives leadership measurable expectations, gives IT clear accountability, and gives employees confidence that a mistake or attack does not have to become a business-ending event.

When recovery planning is treated as a leadership responsibility rather than a background IT task, backups become more than copies of data. They become a credible promise that the business can keep moving when disruption arrives.

IT Consultant Versus MSP: Which Fits Your Business?

IT Consultant Versus MSP: Which Fits Your Business?

A server failure at 9:00 a.m., a suspicious Microsoft 365 login, or a compliance questionnaire due Friday exposes a critical question: who owns the outcome? When comparing an IT consultant versus MSP, the real difference is not simply who can fix technology. It is whether your business has dependable, ongoing accountability for technology performance, cybersecurity, and planning.

For a small or mid-sized business, either model can be useful. The right choice depends on your internal capabilities, risk profile, growth plans, and tolerance for downtime. The mistake is assuming a talented individual consultant and a managed service provider deliver the same operating model.

IT Consultant Versus MSP: The Core Difference

An IT consultant is typically engaged for expertise, projects, advice, or specific technical problems. They may design a network, lead a cloud migration, assess security gaps, help select software, or step in when internal staff need specialized knowledge. A strong consultant can bring valuable perspective without requiring a long-term service commitment.

An MSP, or managed service provider, takes recurring responsibility for defined areas of your IT environment. That commonly includes user support, device management, network monitoring, patching, backups, vendor coordination, cybersecurity tools, documentation, and technology planning. The relationship is designed around continuous operation rather than a series of individual requests.

That distinction matters because businesses do not experience technology risk only during projects. Risks develop between projects: an unpatched laptop, an employee who clicks a credential-harvesting email, a backup that has not been tested, or an internet outage with no documented failover plan. An MSP is built to identify and reduce those recurring operational risks.

What an IT consultant does well

A consultant is often an effective choice when the work has a clear beginning, end, and scope. For example, a 25-person architecture firm may need an assessment before moving files and applications to the cloud. A manufacturer may need help selecting a new ERP platform. A business with a capable internal IT manager may bring in a consultant to validate a network redesign or address a difficult compliance requirement.

This model can be flexible. You pay for a defined outcome, gain access to specialized skills, and avoid paying for services you do not need. It can also be a practical way to get executive-level guidance before committing to a broader technology strategy.

The trade-off is continuity. A consultant may know your environment well during an engagement, but they are not necessarily monitoring it every day, managing every endpoint, documenting every change, or responding to after-hours security alerts. Those responsibilities must remain with internal staff or be assigned elsewhere.

What an MSP is designed to manage

An MSP provides a repeatable operating model for businesses that need technology to work consistently without building a full enterprise IT department. Instead of waiting for a problem to become disruptive, the provider monitors systems, applies maintenance, standardizes configurations, and tracks issues over time.

A mature MSP relationship should include more than a help desk. It should establish clear service ownership, documented standards, predictable support channels, and regular conversations about business priorities. If your company opens a second location, hires rapidly, adopts new applications, or must meet client security requirements, your IT provider should help prepare the environment rather than merely react after the fact.

For many organizations, security is the deciding factor. Managed IT services can include endpoint protection, identity controls, email security, vulnerability management, backup oversight, and incident response coordination. When these services are paired with 24/7 monitoring and managed detection and response, the provider moves closer to an MSSP model focused specifically on security operations.

Compare the Models by Business Outcome

Cost is often the first comparison point, but it should not be the only one. Hourly consulting can appear less expensive until a prolonged outage, ransomware event, failed audit, or repeated emergency call exposes the cost of gaps in coverage.

An IT consultant usually bills by the hour, project, or retainer. This can work well for discrete needs and makes spending easy to tie to a particular initiative. However, the budget may become unpredictable when problems arise unexpectedly. There can also be pressure to defer preventive work because it creates immediate billable expense without an obvious short-term crisis.

An MSP typically uses a monthly recurring model based on users, devices, locations, or a defined service package. The right agreement makes ongoing IT costs more predictable and encourages prevention. Because the provider is responsible for maintaining a stable environment, reducing recurring incidents benefits both parties.

Responsiveness also differs. A consultant may be highly responsive, especially if they have a long-standing relationship with your company. But availability is tied to that person’s schedule and capacity. If they are in the middle of another client project, on vacation, or no longer available, your business may have limited coverage.

An MSP should provide a team structure, escalation path, service-level expectations, and documented access to your systems. That does not mean every MSP offers the same quality. Ask who answers after-hours calls, how urgent incidents are prioritized, whether procedures are documented, and what happens when your primary technician is unavailable.

Strategic planning is another dividing line. A consultant can provide excellent strategic counsel. Yet ongoing planning requires current information about asset health, recurring support issues, security posture, licensing, backup results, and upcoming business changes. An MSP that manages the environment daily has a stronger foundation for vCIO or vCTO guidance because recommendations can be tied to operational evidence.

When a Consultant Is the Better Fit

Choose a consultant when your business has reliable internal ownership of day-to-day IT and needs focused outside expertise. This may include an internal IT team that needs help with a specialized migration, an acquisition, an application rollout, or an independent review of its security controls.

A consultant can also be the right short-term answer for a small organization with simple technology needs and a low-risk operating model. Even then, leadership should identify who handles patching, backup checks, user onboarding, cybersecurity incidents, vendor management, and emergencies. If the answer is “we will call someone when it breaks,” the business is accepting avoidable operational risk.

Consulting works best when scope is specific and ownership is clear. Define the deliverables, timeline, decision-makers, documentation requirements, and post-project support expectations before work begins.

When an MSP Is the Better Fit

An MSP is usually the better fit when technology downtime affects revenue, client service, compliance, or employee productivity. It is particularly valuable for organizations with no internal IT department, a small internal team stretched across too many responsibilities, multiple locations, remote users, or sensitive data.

Healthcare practices, law firms, financial services organizations, engineering firms, and manufacturers often need more than occasional technical help. They need consistent user access, protected data, auditable processes, dependable backups, and a response plan for security events. Those needs require discipline over time, not just technical skill during a project.

A co-managed model can be especially effective for businesses with internal IT leadership. Rather than replacing the team, the MSP handles routine support, monitoring, security operations, or specialized infrastructure work. Internal staff can then focus on applications, business process improvements, and projects that require organizational knowledge.

For DFW businesses facing rapid growth or stricter client security expectations, a security-first MSP can provide the operating maturity that is difficult to build internally. Sigma Networks, for example, combines managed IT, cybersecurity operations, and strategic advisory so clients have one accountable partner across the technology environment.

Questions to Ask Before You Choose

The most useful decision comes from examining responsibility, not marketing labels. Ask a prospective consultant or MSP how they handle 24/7 incidents, how often they test backups, who owns cybersecurity monitoring, how they document systems and credentials, and how they report on service performance.

Also ask what is excluded. Some providers offer monitoring but not remediation. Others provide help desk support but treat security, backup testing, compliance preparation, and strategic planning as separate services. There is nothing inherently wrong with a narrower scope, provided leadership understands the gaps and assigns ownership.

Finally, look for evidence of accountability. You should know who is responsible for keeping systems current, reducing repeated problems, advising leadership, and coordinating recovery when an incident occurs. The answer should be specific, measurable, and documented in the service agreement.

The best choice is the one that gives your business the right level of coverage for its real risk. A consultant can solve a defined problem exceptionally well. An MSP can create the ongoing discipline that keeps many problems from becoming business interruptions. Choose the partner model that lets your team spend less time wondering whether technology will hold up and more time moving the business forward.

Office hours:

Send us a message: