How to Implement Zero Trust in Your Business
A compromised Microsoft 365 account can give an attacker a foothold in minutes. If that user can access every shared drive, application, and administrative system from any device, one stolen password can become a business-wide incident. Learning how to implement zero trust changes that equation by requiring every user, device, and connection to prove it belongs before access is granted.
Zero trust is not a single product or a switch your IT team can flip. It is an operating model for reducing risk while keeping employees productive. For small and mid-sized businesses, the goal is practical: limit unnecessary access, validate identities continuously, protect the devices that handle business data, and detect abnormal activity before it turns into downtime, fraud, or a compliance problem.
What zero trust means for a growing business
The traditional network model assumed that someone connecting from the office, through a company VPN, or with the right password was trustworthy. That model does not match how most businesses operate now. Employees work remotely, access cloud applications, use mobile devices, and collaborate with outside vendors. The network perimeter is no longer the sole security boundary.
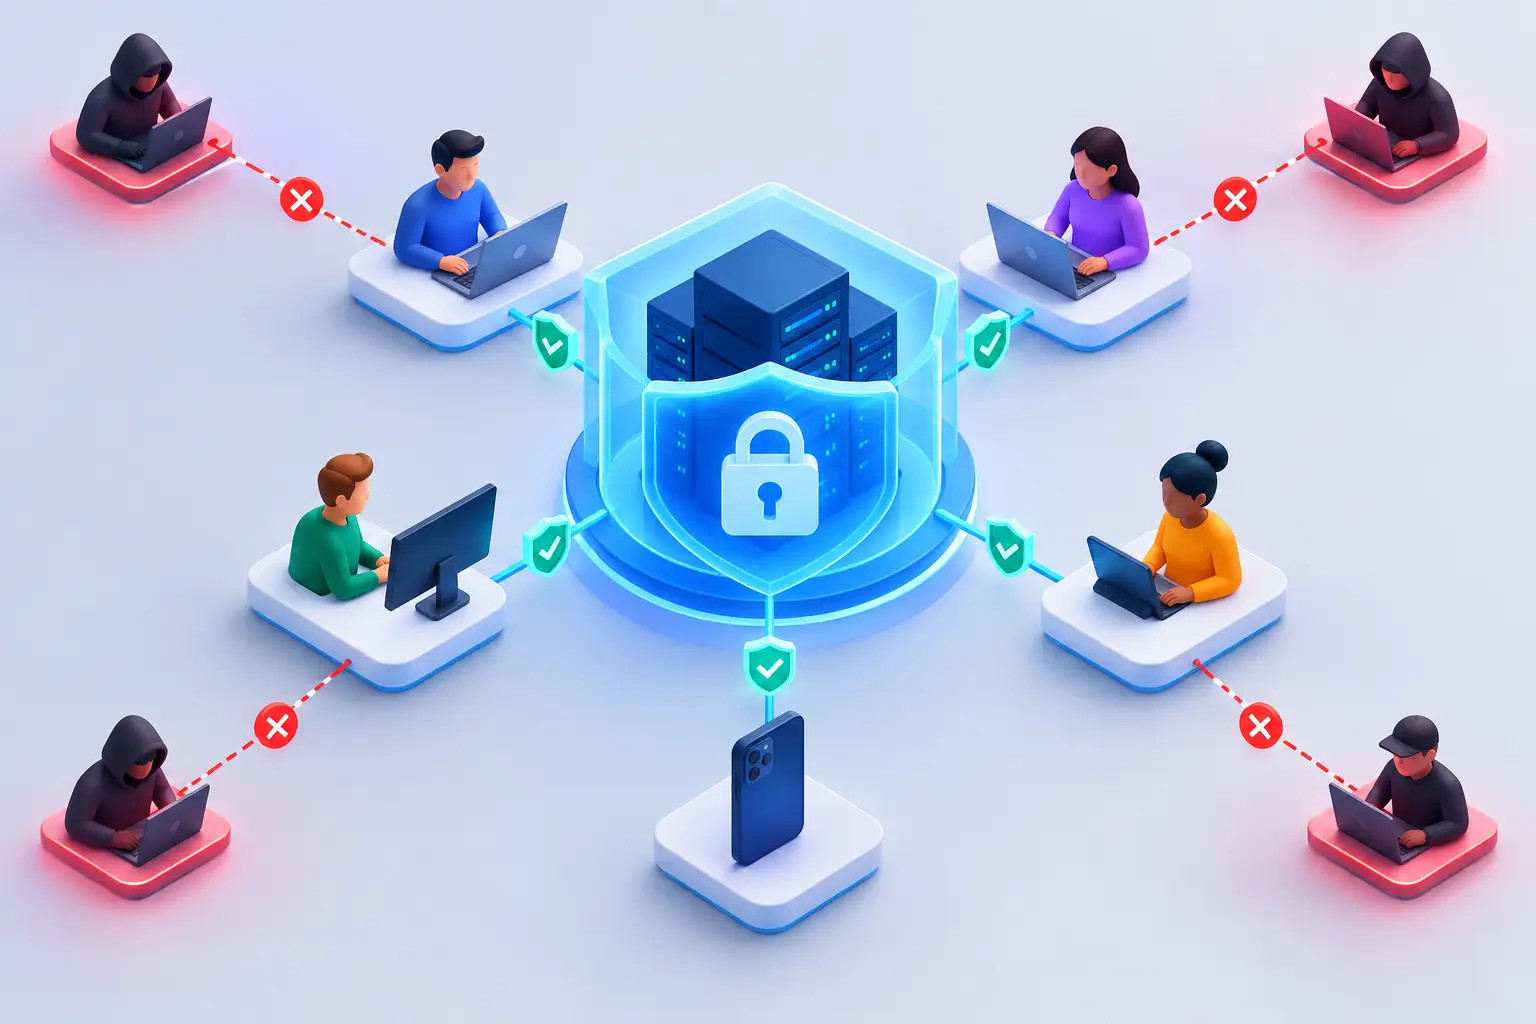
Zero trust replaces broad, assumed access with a simple principle: never trust by default, always verify. A user requesting access is evaluated based on identity, authentication strength, device condition, location, behavior, and the sensitivity of the requested resource.
This does not mean employees must complete a security challenge every time they open a document. A well-designed program applies stronger controls where the business risk is higher. Opening a standard internal document may require routine sign-in, while approving a wire transfer, accessing protected health information, or entering a financial system may require multifactor authentication, a compliant device, and additional verification.
Start with the business risks, not the technology
The fastest way to create a costly zero trust project is to buy tools before defining what must be protected. Begin with a business-focused assessment of systems, data, users, and workflows.
Identify where sensitive information resides. For many organizations, the most critical assets are Microsoft 365 email and files, accounting systems, customer databases, line-of-business applications, intellectual property, and backup administration consoles. Then identify who needs access and why. The accounting team may need access to financial applications, but not to engineering project folders. An outside consultant may need a specific application for a limited period, not a company-wide account.
This exercise often exposes long-standing access issues: former employees with active accounts, generic shared logins, administrators using privileged credentials for daily email, or departments retaining access after a role change. These gaps are common, and they are exactly where zero trust creates immediate value.
For regulated businesses, map the review to existing obligations. Healthcare organizations should consider HIPAA safeguards. Financial firms, legal practices, manufacturers serving government or defense clients, and companies handling payment data may face additional contractual or regulatory requirements. Zero trust supports compliance readiness, but it does not replace a formal compliance program.
Build a reliable identity foundation
Identity is the center of a zero trust strategy. If an attacker can impersonate a trusted user, network controls alone will not protect the business.
Enforce multifactor authentication everywhere it matters
Require multifactor authentication for email, cloud applications, remote access, privileged accounts, and administrative portals. Phishing-resistant methods, such as authenticator apps with number matching, security keys, or passkeys, offer stronger protection than text-message codes when available.
Do not create exceptions casually. Executives, finance personnel, and IT administrators are frequent targets because their accounts can authorize payments, access sensitive records, or change security settings. If a workflow makes multifactor authentication difficult, solve the workflow problem rather than weakening the control.
Apply least-privilege access
Users should receive only the access required for their current responsibilities. Review access when someone joins, changes roles, works with a temporary project team, or leaves the company. This is especially important for shared cloud storage, accounting platforms, customer relationship management systems, and remote management tools.
Administrative access deserves separate treatment. IT staff should use standard accounts for ordinary work and dedicated privileged accounts only when performing administrative tasks. Where possible, provide elevated access just in time rather than permanently. That reduces the damage a compromised credential can cause.
Establish device trust before granting access
A valid password should not be enough to connect an unmanaged, outdated laptop to sensitive company resources. Device posture is a core part of how to implement zero trust effectively.
Enroll company-owned computers and mobile devices in centralized management. At a minimum, the organization should be able to confirm that devices are encrypted, supported by current operating system updates, protected by endpoint security software, and configured with screen locks. Lost devices should be capable of remote lock or wipe when business data is at risk.
For personally owned devices, the right approach depends on the role and the data involved. A bring-your-own-device policy can work for limited email or collaboration access when mobile application management and data protection controls are in place. It may not be appropriate for administrators, employees handling regulated data, or users who need access to sensitive financial and operational systems. Company-managed devices provide more assurance and more consistent support.
Conditional access policies connect these device requirements to actual access decisions. For example, a user may be allowed to access email from an enrolled, encrypted laptop but blocked from downloading company files to an unknown personal device. Start with monitoring or report-only modes where available, then enforce policies after testing business impact.
Segment access so one breach does not spread
Zero trust reduces lateral movement. In plain terms, an attacker who compromises one account or device should not be able to move freely through the rest of the environment.
Network segmentation remains valuable, particularly for organizations with on-premises servers, production equipment, voice systems, or specialized applications. Separate guest wireless networks from business systems. Isolate sensitive systems from general user networks. Limit communication between segments to the specific ports and services required for business operations.
Cloud environments need similar discipline. Use separate administrative roles, restrict access to management portals, and avoid placing sensitive data in broadly shared folders. Secure access service edge and zero trust network access solutions can provide application-level access without exposing an entire network through a traditional VPN. The best choice depends on your applications, workforce, budget, and existing infrastructure.
Add monitoring, detection, and response
Preventive controls reduce the chance of a successful attack, but no environment is risk-free. A zero trust program also needs visibility into what happens after access is granted.
Centralize logs from identity providers, endpoints, firewalls, cloud platforms, and critical applications. Monitor for behavior that deserves investigation, such as impossible travel logins, repeated failed multifactor prompts, a user downloading an unusual volume of files, or an administrator creating new privileged accounts.
For many small and mid-sized businesses, continuous monitoring requires a managed detection and response service or security operations center. Alerts are only useful when someone can validate them, investigate quickly, and take defined containment actions. A 24/7 response capability matters because many attacks begin outside normal business hours.
Your incident response plan should also reflect zero trust controls. Define who can disable a user account, isolate a device, revoke application sessions, contact cyber insurance carriers, and communicate with leadership. Test the plan with realistic scenarios, including a compromised executive email account and a ransomware event.
Roll out zero trust in phases
Trying to enforce every control at once can interrupt business operations and create resistance. A phased rollout protects the organization while allowing employees and system owners to adapt.
A practical sequence is to secure identities first, then managed devices, then conditional access and privileged access, followed by network and application segmentation. Start with the accounts and systems that present the greatest business impact, including executives, finance, administrators, and high-value cloud applications.
Measure progress with outcomes leaders can understand: percentage of users protected by multifactor authentication, number of unmanaged devices accessing company data, dormant accounts removed, privileged accounts reviewed, and time required to contain a suspected compromise. These metrics connect security investment to reduced operational and financial risk.
Employee communication is part of the deployment. Explain what is changing, when it will happen, and where employees can get help. Security controls that are poorly communicated often become workarounds. Controls that are supported, documented, and aligned to real work are far more likely to last.
Make zero trust an operating discipline
Zero trust is not a project with a finish date. Employees change roles, applications are added, vendors require access, and attackers change tactics. Review access rights, device compliance, conditional access policies, and security alerts on a recurring schedule.
The most effective approach balances protection with business reality. A 15-person professional services firm will not deploy zero trust exactly like a multi-site manufacturer, but both can apply the same principles of verified identity, controlled access, secure devices, and continuous monitoring. The next useful step is not to chase every security feature. It is to identify the access decision that creates the greatest risk for your business and put a stronger control around it.
