DFW Outsourced IT Support Comparison Guide
A missed support call can be expensive. So can a ransomware incident, an expired Microsoft 365 backup, or a server failure that stops billing, scheduling, or production. For North Texas businesses, a DFW outsourced IT support comparison should go beyond who offers the lowest monthly rate. The right provider must reduce operational risk, protect sensitive data, and give leadership a clear path for technology decisions.
Outsourced IT can mean very different things from one company to another. One provider may primarily fix problems after users report them. Another may manage endpoints, monitor threats around the clock, maintain documentation, test backups, and meet with leadership to plan upgrades before they become emergencies. Both may call themselves managed IT providers. Their business impact is not the same.
What to Compare in DFW Outsourced IT Support
Start with the scope of responsibility. A dependable managed IT partner should be able to explain exactly what it owns, what your internal team owns, and what falls outside the agreement. Vague promises of “all-inclusive support” can become costly when an outage, security event, onboarding project, or compliance request exposes exclusions.
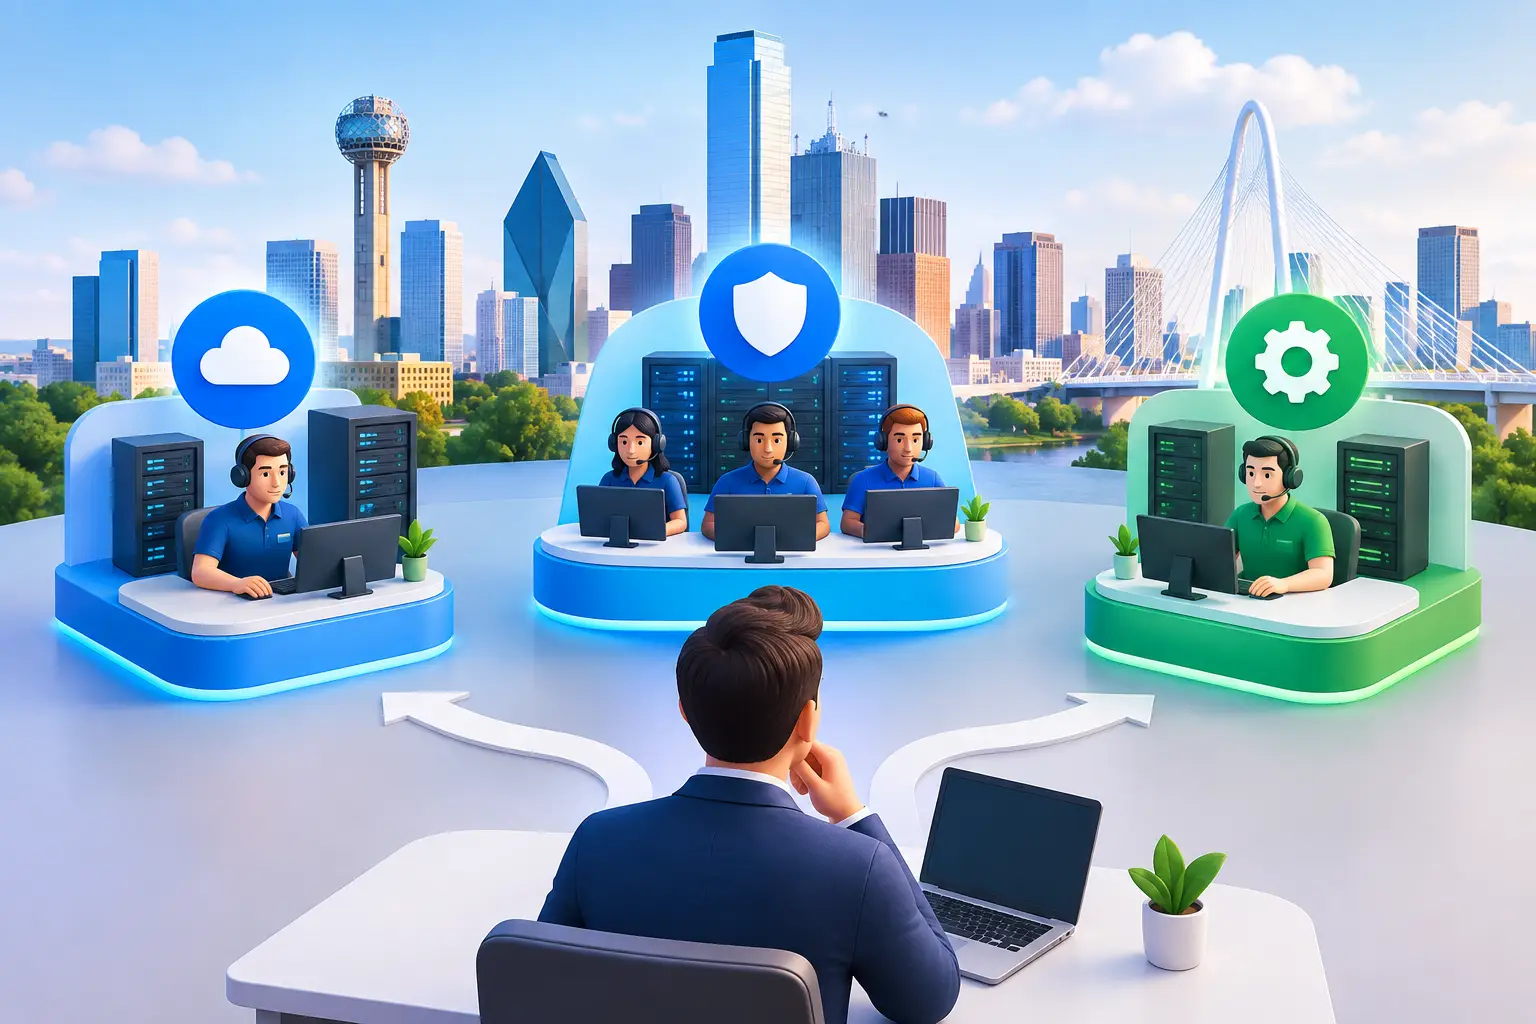
For many small and mid-sized businesses, the comparison comes down to three operating models. Break-fix support bills when something goes wrong. Fully managed IT assumes day-to-day responsibility for the technology environment. Co-managed IT supplements an internal IT employee or department with specialized tools, security operations, escalation support, and strategic guidance.
There is no universal winner. A 20-person professional services firm without internal IT may need fully managed support. A manufacturer with an experienced IT manager may benefit more from a co-managed model that adds 24/7 cybersecurity coverage and project capacity. The key is choosing a model that closes real gaps, rather than paying for overlapping services or leaving critical work unowned.
1. Response Times Are Not the Same as Resolution Accountability
Most providers promote help desk response times. That metric matters, but it is only the beginning. A quick acknowledgment does not restore a failed line-of-business application, contain a suspicious login, or resolve a recurring network problem.
Ask prospective providers how they prioritize issues, who handles escalations, and how they communicate during a business-impacting incident. A meaningful service commitment should distinguish between a password reset and a widespread outage. It should also explain whether support is available after hours, whether that support is US-based, and whether engineers with decision-making authority are available when an issue becomes urgent.
Look for accountability beyond the ticket queue. Providers should identify recurring causes, document fixes, and recommend improvements. If the same Wi-Fi, printing, or account-access problem returns every month, the service model is reactive by design.
2. Security Must Be Built Into the Service, Not Added Later
Cybersecurity is often the sharpest difference in an outsourced IT support comparison. Basic IT management may include antivirus and patching. That is no longer enough for organizations handling client records, financial information, healthcare data, or proprietary business information.
A security-first provider should be able to describe how it protects identities, endpoints, email, networks, and backups. That typically includes managed detection and response, multifactor authentication, vulnerability management, security monitoring, email protection, and an incident response process. The exact stack may vary by industry and risk profile, but the provider should be prepared to explain why each control is in place.
Ask who monitors alerts overnight and on weekends. Ask whether suspicious activity is merely reported or actively investigated and contained. Also ask how privileged accounts are protected and how quickly departed employees lose access. These are practical questions with direct consequences for business continuity.
For regulated organizations, security should connect to compliance readiness. Healthcare, legal, financial services, engineering, and professional firms may face contractual, insurance, or regulatory expectations that require documented controls. A provider does not need to replace legal counsel or a compliance officer, but it should help maintain evidence, policies, access records, risk assessments, and remediation plans that stand up to scrutiny.
3. Backup Is a Service. Recovery Is the Test.
Every IT company says it backs up data. The more useful question is whether it can restore your business within an acceptable timeframe.
Compare backup coverage across Microsoft 365, servers, workstations, cloud applications, and critical line-of-business systems. Confirm retention periods, encryption, immutable or isolated backup options, and the location of recovery copies. Then ask how often restores are tested and whether the provider has documented recovery objectives for your most important systems.
A low-cost provider may offer backup software while leaving restoration planning to the client. A strategic partner helps determine which systems must return first, how employees will work during an outage, and who will communicate with vendors, insurance carriers, and leadership. Those details matter far more than the word “backup” on a proposal.
Compare the Operating Model, Not Just the Tool List
Two providers can sell the same Microsoft licenses, firewall brand, or remote monitoring platform. The differentiator is how consistently those tools are managed and how well the provider understands your business.
Technology documentation is a good indicator. A mature provider maintains current records of users, devices, network diagrams, vendors, configurations, licenses, and recovery procedures. Without documentation, every support request takes longer and every transition becomes riskier. It also leaves your company dependent on individual technicians rather than a disciplined operating process.
Strategic planning deserves equal attention. Ask whether the provider includes vCIO or vCTO guidance, how often it meets with leadership, and what those meetings produce. The answer should include budget forecasting, lifecycle planning, risk priorities, compliance needs, and recommendations tied to business goals. If you are opening another office, acquiring a company, moving applications to the cloud, or preparing for a client security review, IT planning cannot begin after the decision is made.
Sigma Networks approaches outsourced and co-managed IT as a strategic responsibility: secure operations, accountable support, and a plan that supports growth. That approach is especially valuable when internal teams are already carrying too much operational and security risk.
Understand Pricing Before You Compare Monthly Fees
Per-user pricing can make budgeting easier, but it does not automatically mean comparable service. A lower quote may exclude security monitoring, onsite visits, executive planning, Microsoft 365 backup, after-hours support, projects, or remediation of existing problems. A higher quote may include those capabilities, reducing surprise costs and limiting exposure that could be far more expensive than the monthly difference.
Request a clear explanation of what is included, what is billed separately, and what assumptions support the price. Pay close attention to onboarding fees, minimum user counts, contract terms, hardware procurement policies, and hourly rates for projects. It is also reasonable to ask whether the provider requires an initial remediation period. If your environment has outdated systems, unmanaged devices, weak passwords, or incomplete backups, correcting those conditions is necessary work, not a sales tactic.
The best value is not the lowest invoice. It is the arrangement that gives your organization predictable support, measurable security coverage, and fewer disruptions to the people doing revenue-producing work.
Questions That Reveal a Provider’s Depth
During a provider review, listen for direct, specific answers. General assurances should not substitute for operating detail. Four questions often reveal whether a firm can function as a true technology partner:
- What happens in the first hour of a suspected ransomware event?
- Which security controls are monitored 24/7, and who responds to alerts?
- How do you test backups and prove that critical systems can be restored?
- What recommendations would you make in the first 90 days, and how would you prioritize them?
The answers should reflect your environment and industry, not a generic sales script. A capable provider will also ask thoughtful questions about your users, applications, contracts, cyber insurance, growth plans, and tolerance for downtime. Good IT support begins with understanding what the business cannot afford to lose.
Choose the Partner That Makes Risk Visible
A DFW outsourced IT support comparison is ultimately a decision about control. You are choosing whether technology will remain a collection of tickets and surprise costs or become a managed business function with clear ownership.
The provider you select should make risks visible before they become incidents, explain trade-offs in business terms, and take responsibility for the details that keep your organization operating. When support, cybersecurity, recovery, and planning work together, leadership has more room to focus on clients, employees, and growth.
